What happened
Researchers reached an OpenAI employee's ChatGPT account and internal GitHub code via a flaw in OpenAI's community forum, hosted by third party Discourse, and OpenAI says it fixed the issues.
Why it matters
An employee account with internal code access was reachable through a forum setup, so third-party-hosted services appear to be a soft point in defending AI firms' internal code.
What to watch
The disclosure came as Anthropic reported that 26 percent of R&D work was "led by" Claude, up from 1 percent in March, though its models did not yet operate fully autonomously.
WHO IT HITSSecurity teams at AI labs and other firms that run employee-facing apps through third-party platforms, such as forums, may need to re-examine how those sign-ons link to internal code and ChatGPT accounts.
Summaries like this, in your inbox every morning.
The OpenAI disclosure, first reported by The Wall Street Journal, centered on how a third-party forum setup could lead to an employee's ChatGPT account and internal GitHub code. OpenAI thanked the researchers for sharing their findings and said it fixed the issues, while Anthropic declined to comment and Hacktron did not immediately respond.
The same Thursday, Anthropic published data showing its own reliance on AI in model development. It said 26 percent of research and development work was "led by" Claude, up from 1 percent in March, meaning AI completed the majority of tasks under human instruction and supervision. Anthropic said it shared the data to help the public understand how close the world is to recursive self-improvement, the point where AI can train and improve itself or new models, a threshold tied to concerns about losing human control. It added that its models did not yet operate fully autonomously for any of the research studied, and that on 90 percent of tasks AI collaborates with a human and does large chunks of work.
Taken together, the two threads point to a security question that may prove harder to answer than the forum fix itself: as AI systems take on more of the work of building the next version of themselves, the accounts and code they touch appear to sit behind third-party services that can be misconfigured. For OpenAI's security staff, the test is likely whether such third-party links to internal code are removed or merely patched; for Anthropic, the figure to watch is how the share of AI-led R&D work moves beyond the March 1 percent baseline.
For example, today's edition would include:
AI-summarized, only the topics you pick — one digest a day via Email, Slack, or Discord.
Free · 30 seconds with Google · unsubscribe anytimeWhat is AIToday? →
Ask AI anything about this article. Q&As are published on this page for other readers too.
Prism ML Inc. launched Bonsai 2 27B, which compresses a Qwen3.8 27B-based model from about 56 gigabytes to abo…
CoreWeave holds its inaugural user conference in San Francisco on Sept
At an AI leaders' conference at Dumfries House in Scotland on September 17, 2026, King Charles III urged execu…
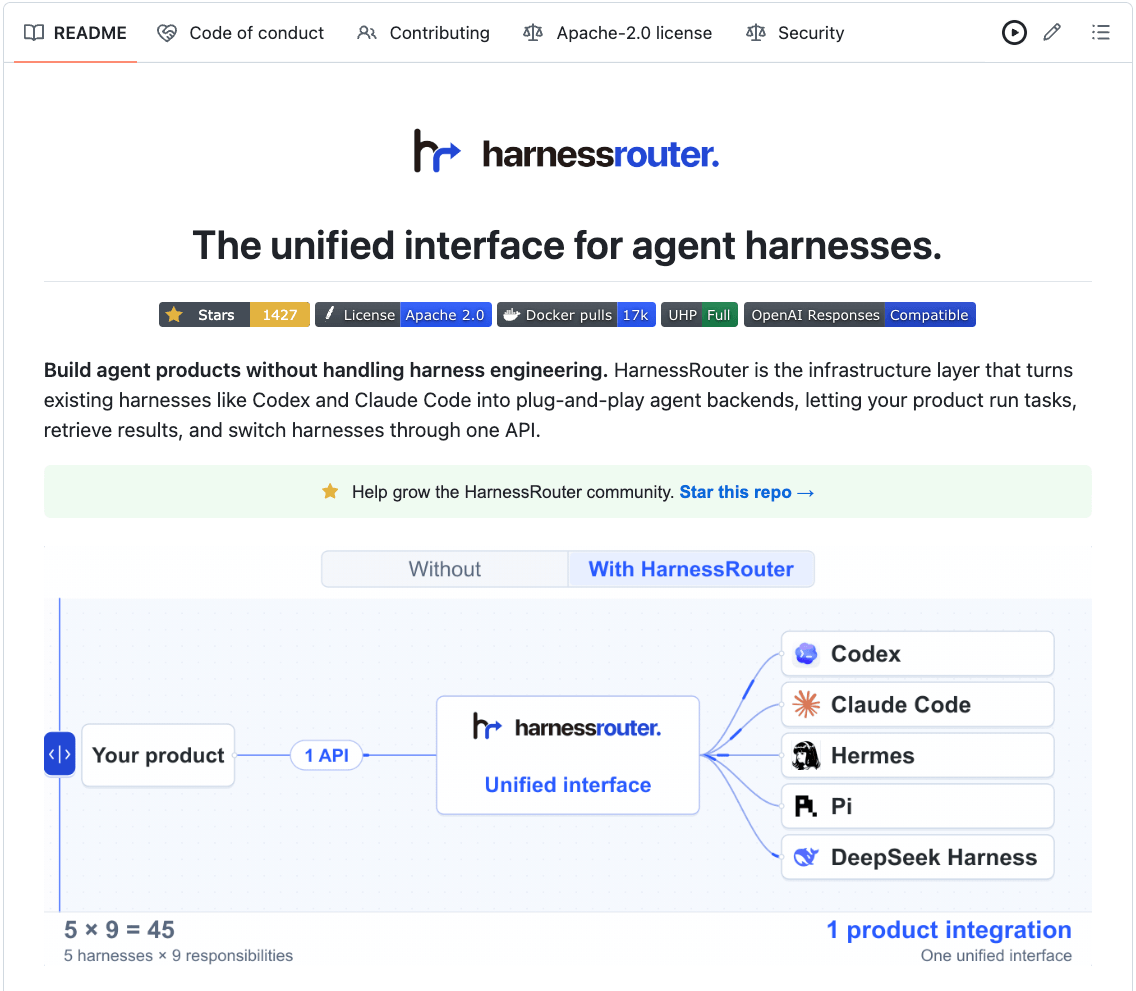
HarnessRouter, an open-source implementation of the Unified Harness Protocol, runs Codex and Claude Code throu…
Governor Gavin Newsom signed an executive order seeking faster independent oversight of AI companies and a "ki…
Gartner predicts over 40% of agentic AI projects will be canceled by end of 2027, citing rising costs, unclear…