What happened
Calif, a US security firm, disclosed a worm that hijacks WeChat accounts and spreads via contacts with no user clicks. The flaw was fixed after Calif alerted Tencent.
Why it matters
The incident follows an AI-powered hack of Hugging Face, highlighting that cyber vulnerabilities cross borders. Trust between US and China is nearly nonexistent, so private firms step in.
What to watch
Whether private cross-border collaboration can prevent future worms. The article suggests firms may rely on unofficial channels without government agreements.
WHO IT HITSEnterprise security teams and platform owners like Tencent must rely on private-sector cooperation to patch vulnerabilities, as government trust is minimal.
Summaries like this, every morning.
The WeChat worm, revealed by Calif, follows the AI-powered hack of Hugging Face and a Chinese open-source model used to investigate it. These incidents show that cyber threats span borders, as US-China expert Samm Sacks noted, making government-led solutions difficult due to minimal trust. Beijing and Washington define AI safety differently, complicating bilateral agreements.
Private companies, researchers, and technologists may offer a more technical foundation. The article suggests that without government cooperation, firms will rely on unofficial cross-border communication to prevent similar attacks. This hinges on whether private actors can effectively share threat information despite geopolitical tensions.
Pick your industry and the AI tools you use, and get news related to your work every day.
Free · 30 seconds with Google · unsubscribe anytimeWhat is AIToday? →
Ask AI anything about this article. The AI reads this article, earlier AIToday articles, and Wikipedia, and cites its sources. Q&As are published on this page for other readers too.
Amphenol reported adjusted earnings of 80 cents per share, up 74% year over year, and revenues of $10.23 billi…
Lockheed Martin's AI Center (LAIC) applies RAGE — Responsible AI Governance and Evaluation — at multiple tollg…
Analog Devices, collaborating with Nvidia on AI data-center infrastructure, physical AI and edge robotics, ran…
Charles Schwab is expanding AI tools for registered investment advisors, integrating Claude for Financial Advi…
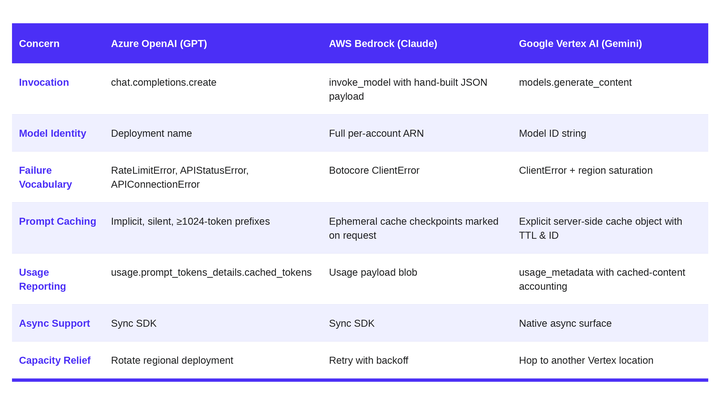
Octus says it routes more than 20 billion tokens a year through its data science models, using what it calls a…
T-Mobile beat forecasts and set out a mid-term plan covering an AI build-out and a pay-out