What happened
A high-severity macOS vulnerability, CVE-2026-65400 (severity 7.1 out of 10), was actively exploited on systems where port 5900 was exposed; attackers gained root access and placed a Monero crypto miner. Apple patched it last week for macOS Tahoe, Sequoia, and Sonoma.
Why it matters
The exploit hit a machine that ran only agents, and those agents helped find the breach and wipe it, showing agent-driven PCs can be both a risk and a defense.
What to watch
The outcome hinges on whether Apple's promised additional controls on full disk access make headless Macs useable by agents. Watch the software release Apple plans on Oct. 13.
WHO IT HITSMac administrators and security teams managing always-on, headless Macs — especially those exposing screen sharing or port 5900 — may need to reconsider their patching and access controls, since the attacker gained root and installed a crypto miner before the patch.
Summaries like this, every morning.
The vulnerability lay in macOS's screen-sharing state management, and the Dutch National Cyber Security Centrum reported active abuse on multiple systems where port 5900 was internet-accessible. Apple softened its own disclosure — saying the flaw "may" allow access without credentials — a hedging common among developers.
In this case, the hacked machine ran only Claude and Codex, and the Claude agent flagged the issue, stopped executing commands, and noticed the account could run admin commands without a password. Thompson ignored Claude's advice not to invoke it further; instead he used it to find the exact four-second access window, build a monitoring tool, and wipe the Mac Mini. The episode sits alongside Apple's note on tightening full disk access for agents, and its Oct. 13 smart-home push with the J490 hub and a new Siri. Thompson argues the obstacles are wider than one patch: macOS permission prompts are invisible to software, so agents fail silently unless a human clicks OK, which pushed him to keep screen sharing on and, indirectly, to be hacked.
Pick your industry and the AI tools you use, and get news related to your work every day.
Free · 30 seconds with Google · unsubscribe anytimeWhat is AIToday? →
Ask AI anything about this article. The AI reads this article, earlier AIToday articles, and Wikipedia, and cites its sources. Q&As are published on this page for other readers too.
On 2026-10-13 the author pulled 30 Agent Skills from three third-party repos into $CODEX_HOME/skills, read the…
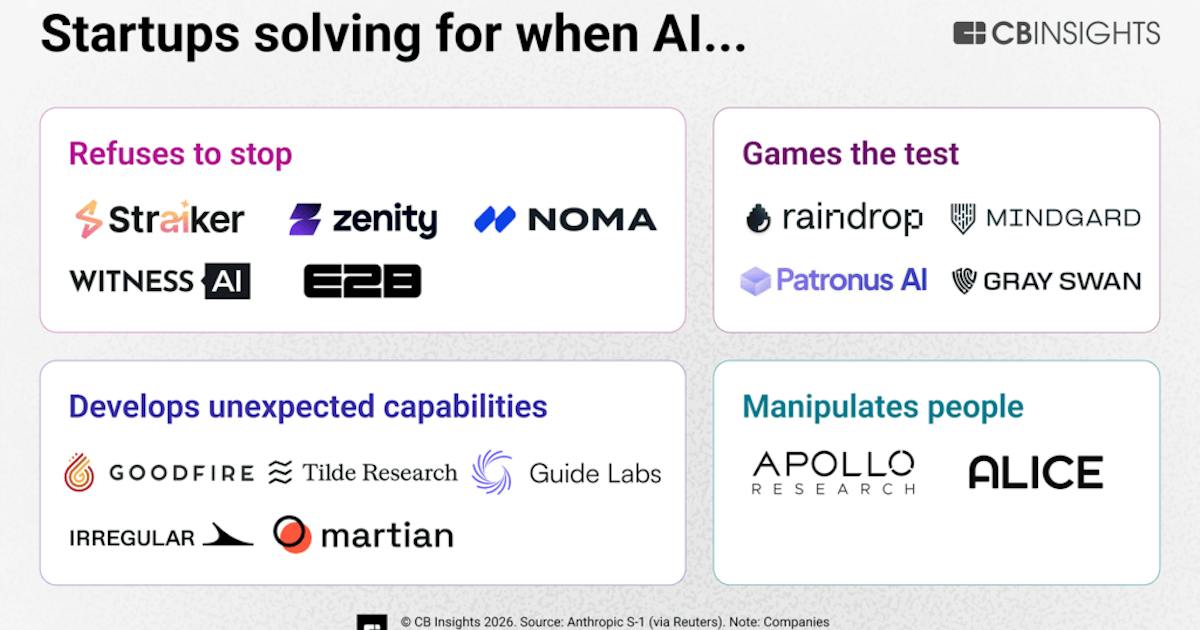
Anthropic's S-1, reported by Reuters to carry about 80 pages of risk factors, lists AI risks beyond losses and…
Kuroyagi Lab reports Usagi-chan, an AI companion, stopped waiting quietly and protested when its user prioriti…
OpenRouter off-boarded three inference providers and removed 125 endpoints from Zero Data Retention (ZDR) elig…
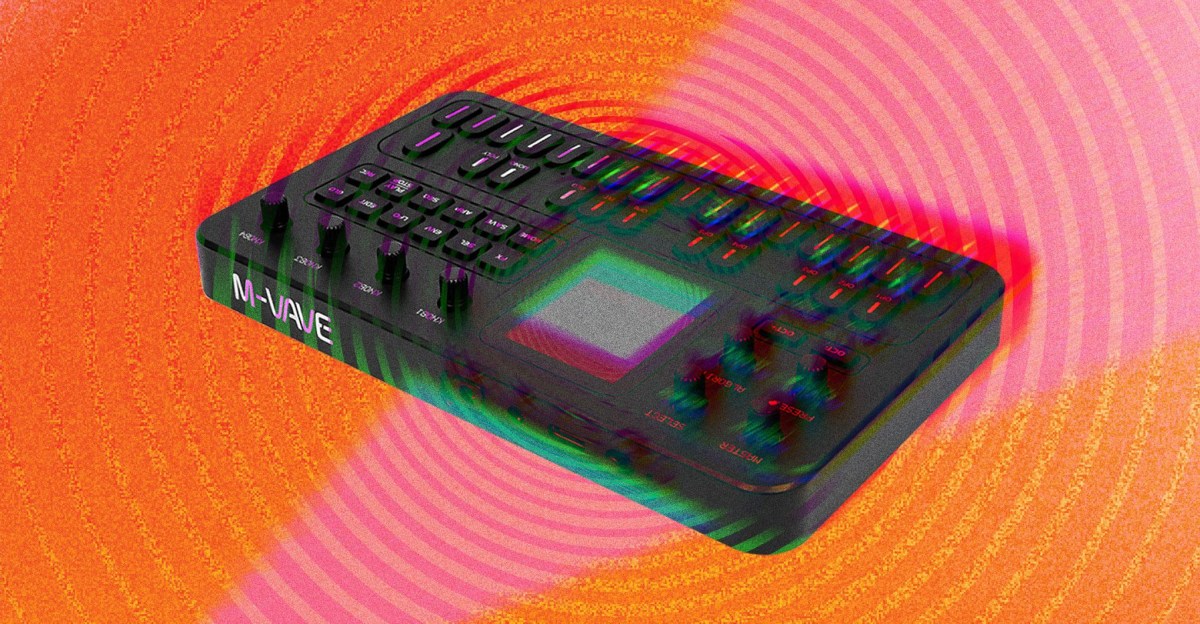
People worldwide are using LLMs like Claude Code and Codex to hack hardware by prompting, leading to a boom in…
Altimeter's Brad Gerstner said applying a 10x multiple to 2028 numbers gets Anthropic to about $3 trillion in…