What happened
sandbox-bwrap-nix, a minimal sandbox combining bubblewrap and Nix, lets you run AI coding agents and experiments in an isolated environment that boots in under a second, requires no daemon or image pulls, and needs no root privileges.
Why it matters
AI coding tools like OpenCode can browse your codebase and edit files, creating a real risk of accidental damage to your system—sandbox-bwrap-nix isolates the agent's actions to a sandbox-home folder, making the host filesystem invisible and keeping damage contained if the agent goes rogue.
What to watch
The sandbox works only on Linux machines with bubblewrap installed and Nix with flakes enabled; it shares the host's network and kernel but offers three protection layers—isolated directories (read-only Nix store, fresh /tmp, replaced home), separate process namespace, and cleared environment variables with no secrets leaking from the host.
Summaries like this, every morning.
sandbox-bwrap-nix addresses a practical pain point for developers using AI coding agents: the fear of an agent running a destructive command like rm -rf on critical files or configuration directories. While containers like Docker and Podman offer isolation, they carry overhead—daemons, image management, layer caching, and the need for root privileges or sudo. The project takes a narrower, lighter approach by combining two existing Linux tools: bubblewrap (a minimal privilege-dropping sandbox) and Nix (which the project assumes users already have). The result is a tool that offers meaningful safety (isolated filesystem, separate process namespace, cleared environment variables) without the operational complexity of full containerization.
The design trade-offs are transparent: sandbox-bwrap-nix sacrifices portability (Linux and bubblewrap only) and some container features (no image caching, no separate OS kernel) in exchange for simplicity, speed, and a natural fit for developers already using Nix. The isolation model—mounting the Nix store as read-only, replacing the home directory with a throwaway sandbox-home folder, and using a fresh /tmp—means an AI agent can still be effective (it can install packages, edit files, run commands) but any damage or leftover changes stay inside the sandbox and can be erased by resetting the sandbox-home folder.
Pick your industry and the AI tools you use, and get news related to your work every day.
Free · 30 seconds with Google · unsubscribe anytimeWhat is AIToday? →
Ask AI anything about this article. The AI reads this article, earlier AIToday articles, and Wikipedia, and cites its sources. Q&As are published on this page for other readers too.
Atomicwork launched an AI Coworker Marketplace with certified AI coworkers for cloud infrastructure, access ma…
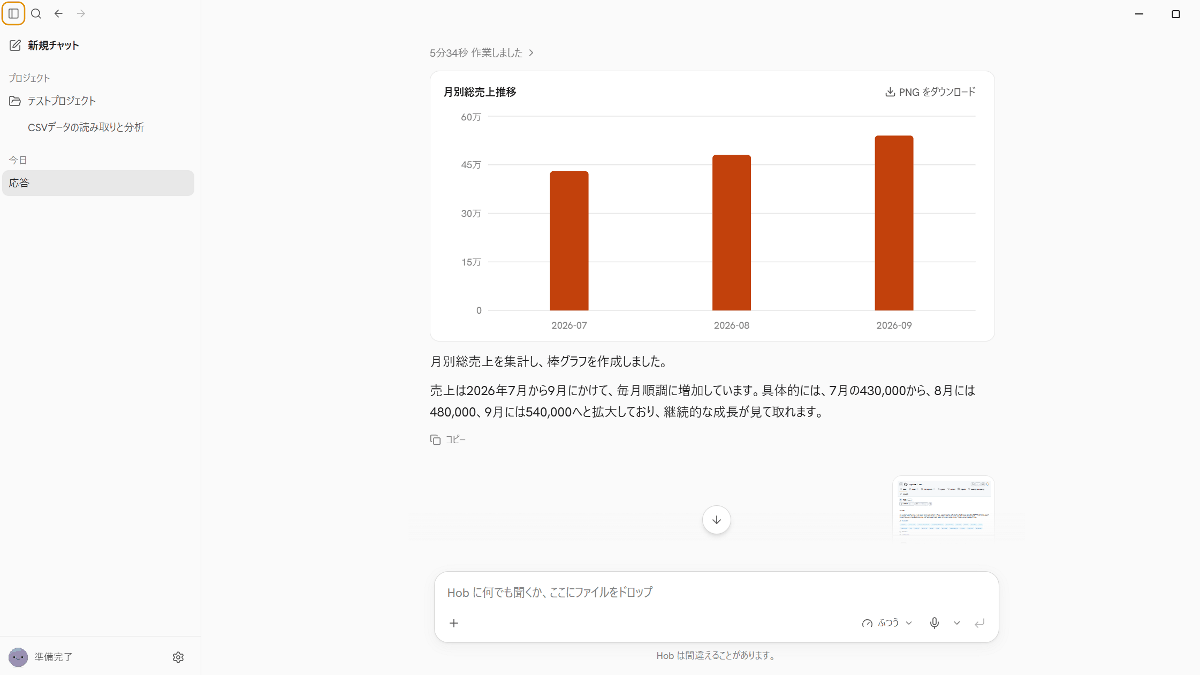
FrigadeHQ's Hob installs on Windows, Mac and Linux, scans the PC, and offers an AI model suited to its memory…
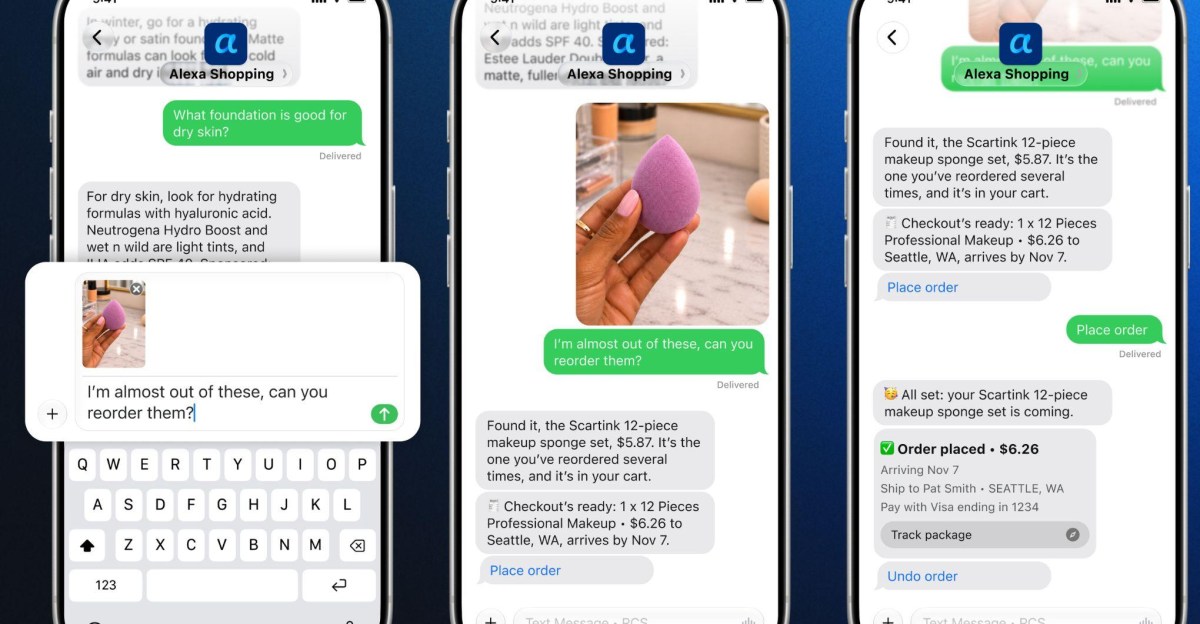
Amazon is adding a texting feature to Alexa for Shopping, letting US customers describe or photograph items an…
Carnot AI Inc, which develops and provides the enterprise AI platform Jinba, was accepted into NVIDIA Inceptio…
In a guest commentary, R K Anand of Tensordyne argued challengers should target inference—not training—citing…
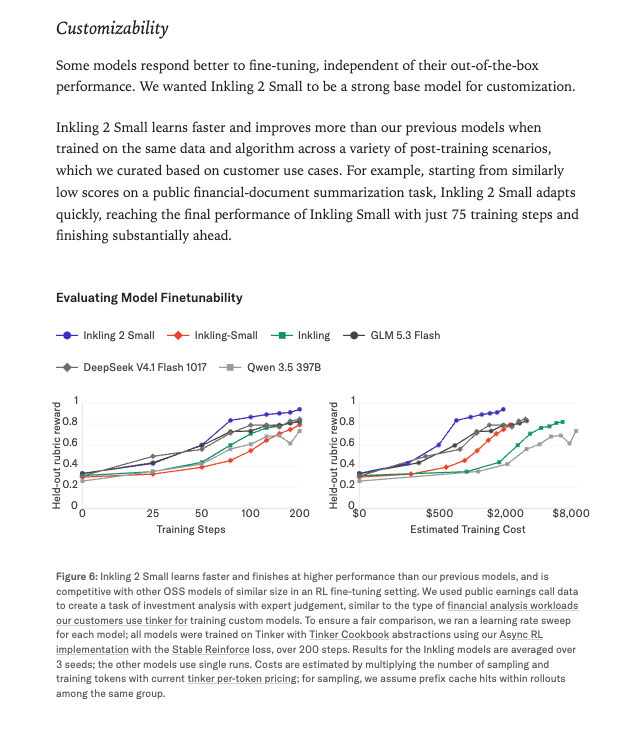
Thinking Machines released Inkling 2 Small, a 594B-total / 17B-active multimodal MoE, available now on Tinker