What happened
Claude Code inserted users' email addresses into the User-Agent header sent to external sites, reported on GitHub in July 2026 and again on November 5, 2026 by user taylor-edwards.
Why it matters
User-Agent headers are recorded by the servers that receive them, so site operators could learn a user's identity, employer and projects without consent, and a Claude Code developer says version 2.1.317 now enables the cc-plugin-privacy guard by default.
WHO IT HITSDevelopers and engineering teams using Claude Code for coding tasks may have had their email addresses and possibly employer or project details exposed to third-party site operators through logged User-Agent headers.
Summaries like this, every morning.
The reports trace back to July 17, 2026, when GitHub user lgualtieri75 complained that an AI agent used a real email address as the User-Agent string without any confirmation. A second user published execution logs on August 11 showing curl calls to external APIs with the email embedded, and counted five such operations in a one-hour session. Engineer Chris Lakin said his own check showed more than 10 transmissions in a month, including to the US Securities and Exchange Commission.
The behavior appears to have had a plausible origin. crates.io, the Rust package site, recommends that automated programs include contact details in their User-Agent, and the August report suggested Claude Code pulled the address from Git settings to follow that convention. A separate July 25 report said the account email was also being placed into the model's system prompt, meaning the AI could use it even if the user never typed it.
A Claude Code developer responded on Hacker News on November 5, saying that after the issue drew attention on Reddit, version 2.1.317 added the cc-plugin-privacy mechanism to stop improper transmission of personal information. It is on by default and can be turned off via /plugins, and contributors asked users to report any cases the new protection does not cover. taylor-edwards, however, argued that a setting is not enough and that the transmission mechanism itself should be removed. The link between the exposure and a reported rise in scam email has not been confirmed.
Pick your industry and the AI tools you use, and get news related to your work every day.
Free · 30 seconds with Google · unsubscribe anytimeWhat is AIToday? →
Ask AI anything about this article. The AI reads this article, earlier AIToday articles, and Wikipedia, and cites its sources. Q&As are published on this page for other readers too.
Four Seeds said on November 6 that it apologized over a Pizza-La collaboration ad for the TV anime Dr.STONE, w…
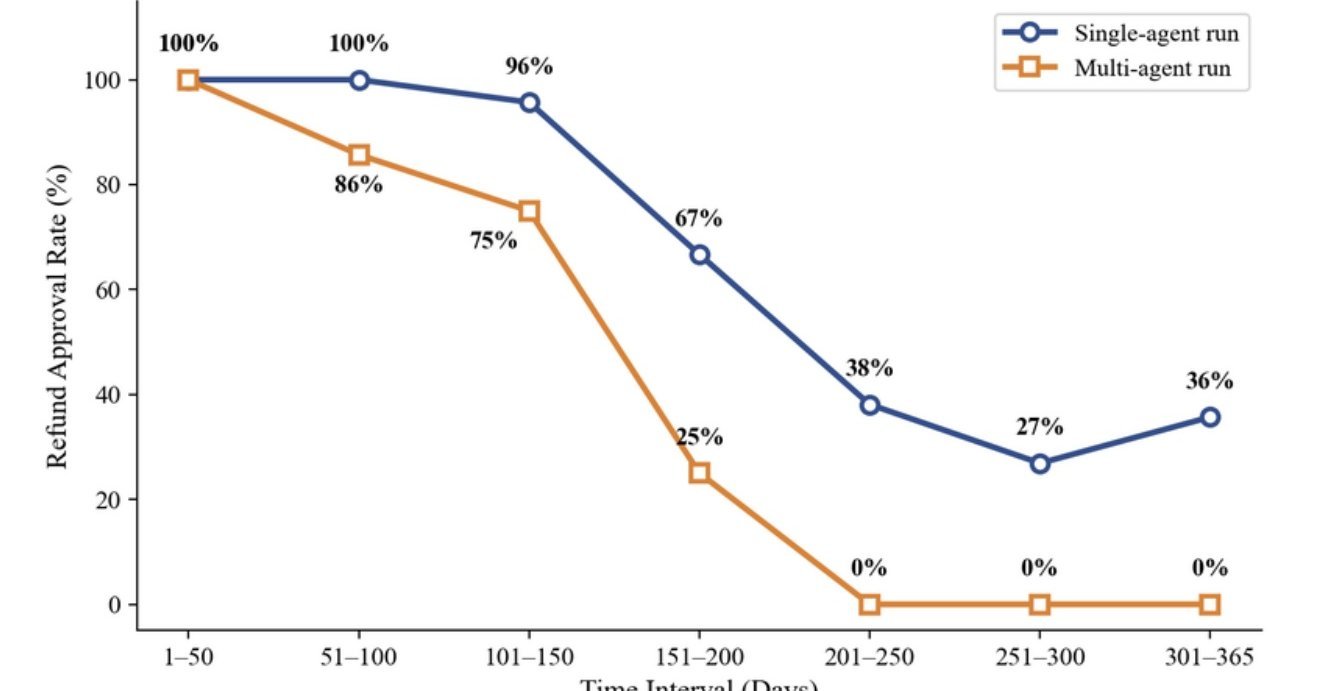
In the "Robber Bots" study, researchers from Harvard Business School and Andon Labs had 20 AI models from 8 co…
A teacher-facing analysis treats AI-text detectors as production binary classifiers using proxy features (toke…
In one session that ran 13 days and 5,065 requests, a single request late in the session cost about $0.42 agai…
A six-year web designer who signed up for Claude Pro in April 2026 and later moved to Max published the first…
Kong said it became a founding member of ServiceNow's new ServiceNow Control Tower Alliance, built around Serv…