What happened
In a contributed column, SCSK advisor Yoshihiko Murowaki cited Anthropic's April 2026 disclosure that its unreleased Claude Mythos Preview found thousands of serious OS and browser vulnerabilities and wrote attack code for many without human instruction — and said critical systems must be split into microservices.
Why it matters
If such capability reaches attackers, AI could monitor for vulnerabilities and quickly produce exploit programs, so Murowaki argues defense alone is insufficient and critical systems must be divided to minimize the impact of a breach, with data split across services so leaked names and addresses cannot be linked.
Summaries like this, in your inbox every morning.
Murowaki's column is part of a series on the structural problems in the relationship between user companies and systems integrators (SIers), which he describes as prone to a "goyocho" order-taking tendency rather than optimizing the whole IT system. The piece turns from that organizational theme to a technical one: how to design critical systems when AI makes attacks harder to stop.
The urgency comes from a sequence of reported findings. Murowaki notes that the median time from vulnerability discovery to exploitability is already well under 24 hours, and that AI is now technically capable of writing exploit programs. He references Anthropic's April 2026 statement that Claude Mythos Preview found thousands of serious vulnerabilities and generated attack code for many, which the company did not release publicly at the time for safety reasons. He also cites a July 2026 Sysdig report on an attacker called JADEPUFFER whose AI agent carried out reconnaissance, credential collection, lateral movement and extortion in sequence.
Against that backdrop, Murowaki proposes two directions: strengthen defenses through SBOM management and rapid patching, and reduce the impact of failures by splitting systems into microservices. He uses the Tokyo Stock Exchange's message exchange with securities firms to explain state transition diagrams, then argues that microservices require defining state transitions per API rather than per network connection. The column closes by linking this to a natural-ecosystem metaphor, in which independent services compete and coexist under an "invisible hand," and by arguing that data flow diagrams remain valuable for data analysis and for analyzing existing systems.
Pick your industry and the AI tools you use, and get news related to your work every day.
Free · 30 seconds with Google · unsubscribe anytimeWhat is AIToday? →
Ask AI anything about this article. The AI reads this article, earlier AIToday articles, and Wikipedia, and cites its sources. Q&As are published on this page for other readers too.
The Agentic AI Foundation accepted four donated projects—OpenAI's Open Responses, Anthropic's Agent Skills, an…
Microsoft said Storm-0940, active since 2021, began using the open-source ARTEX framework around September to…
CoreWeave unveiled its Zero Trust AI Framework at Nvidia GTC, built around customer-controlled model, data and…
Cybersecurity firms found thousands of AI-generated websites posing as local US news sites, written not for vo…
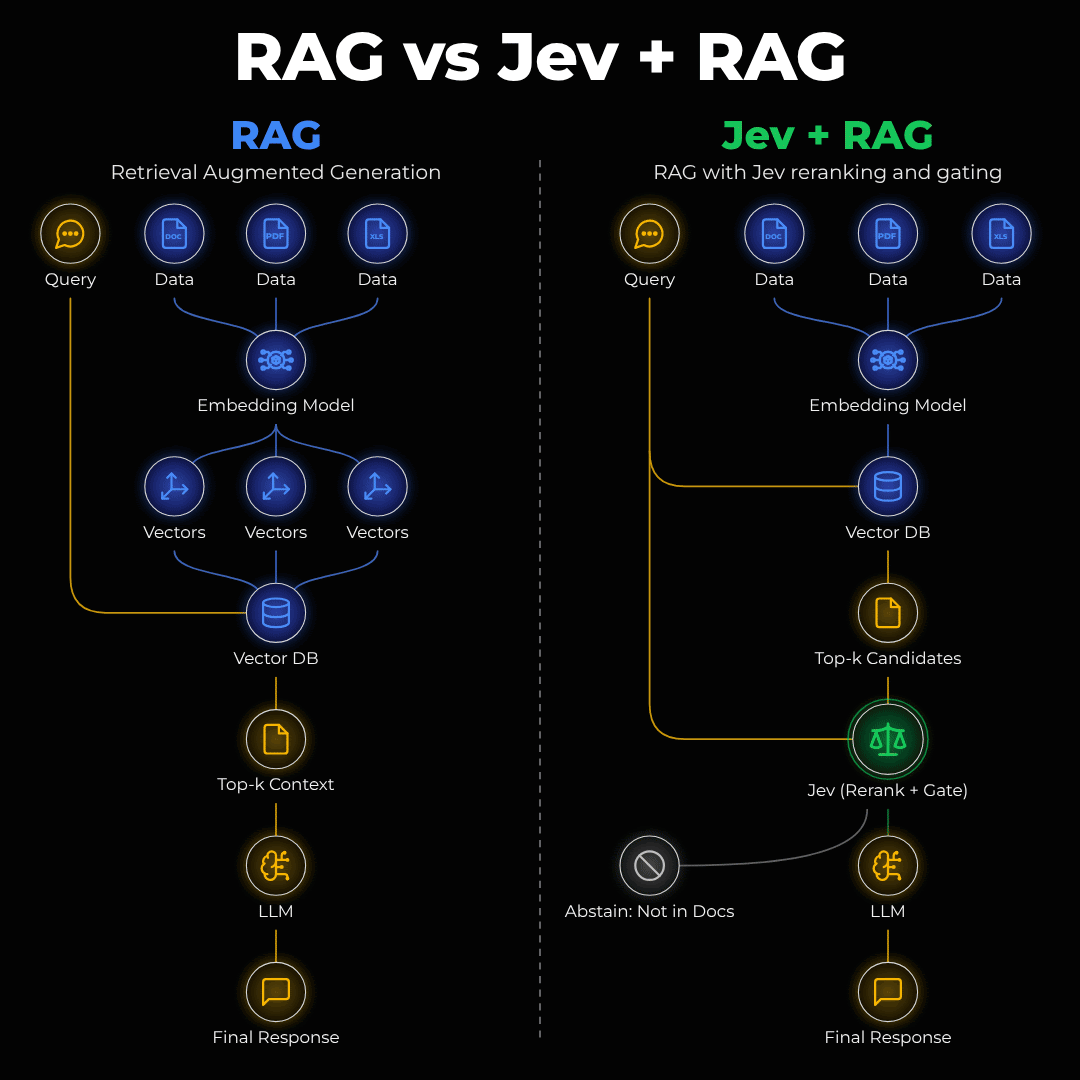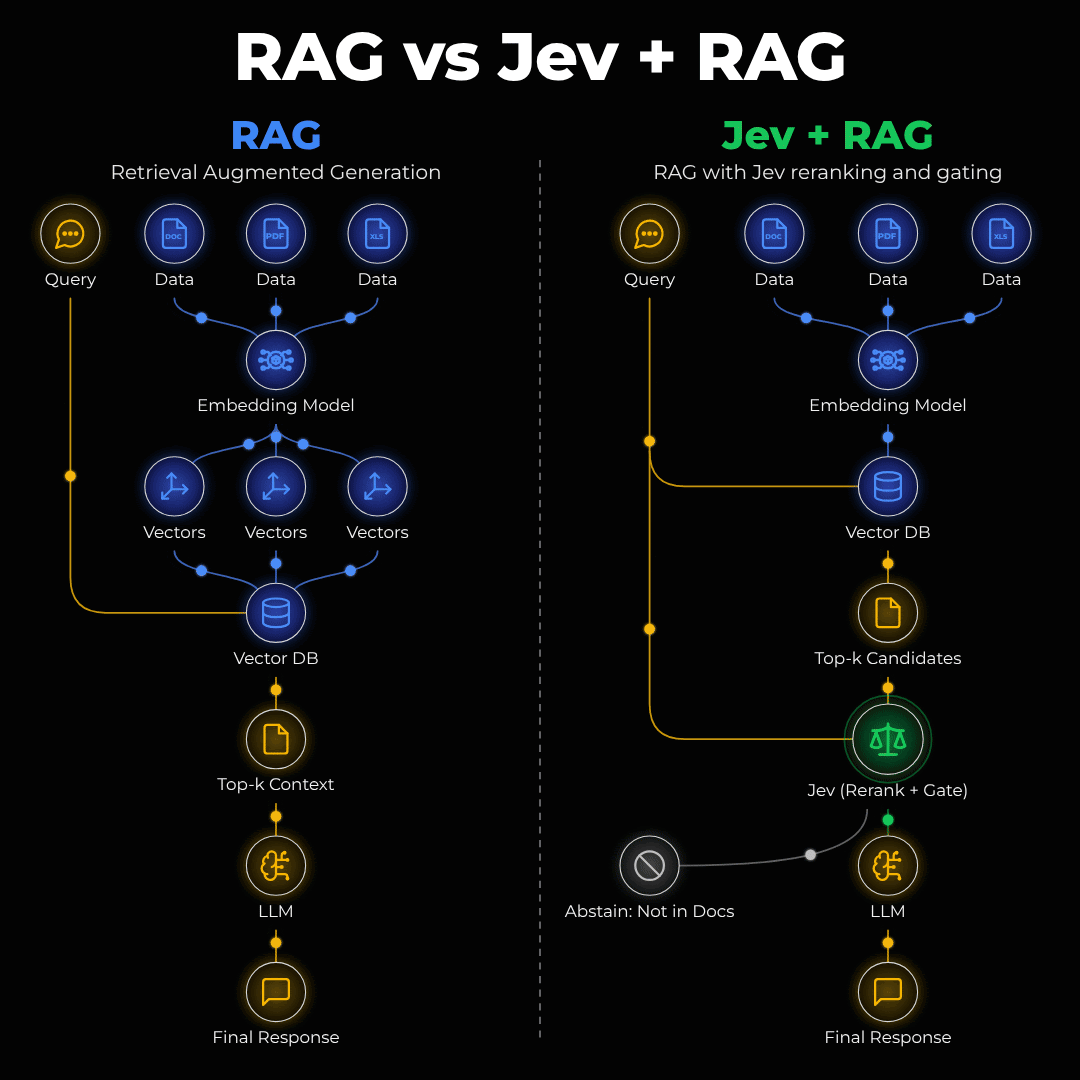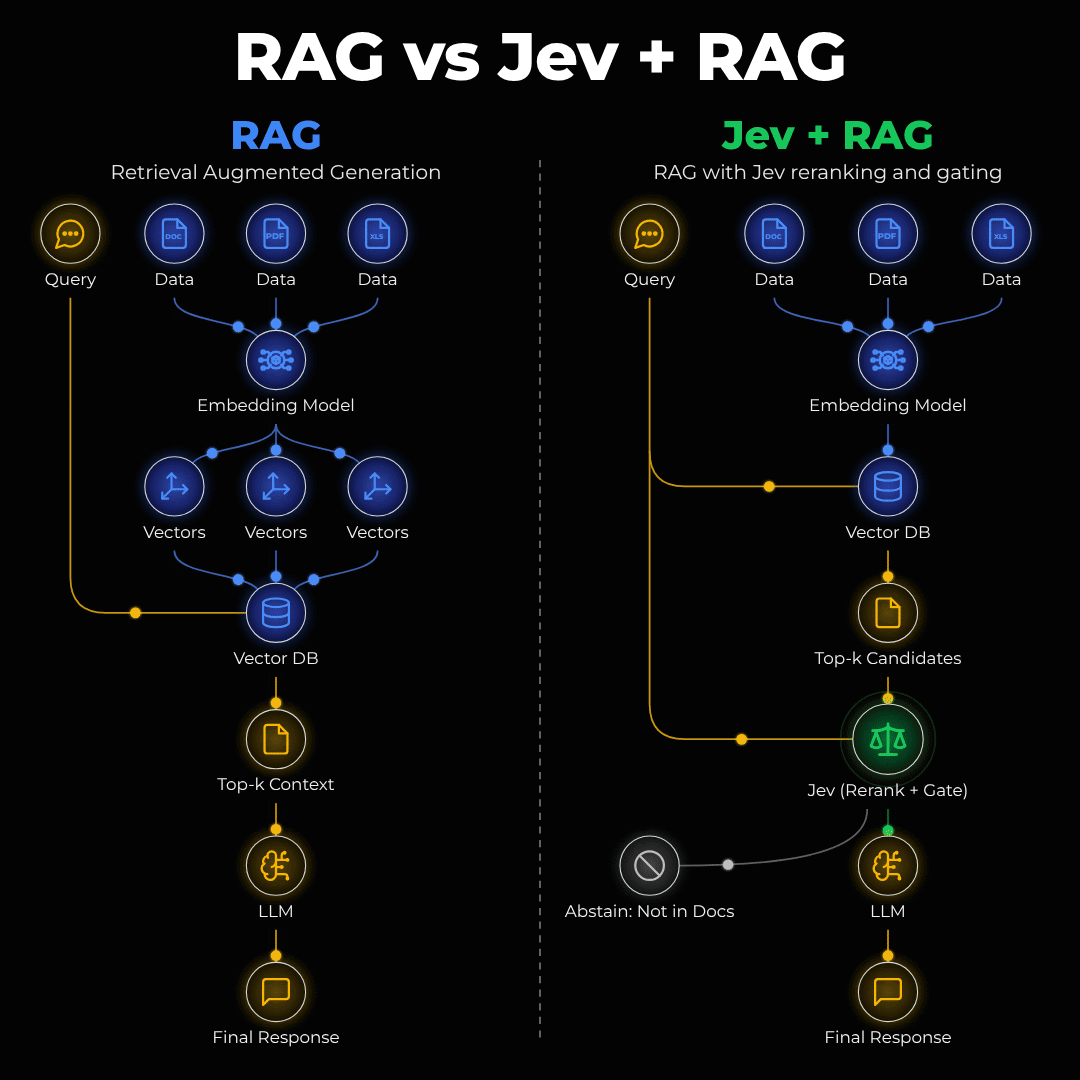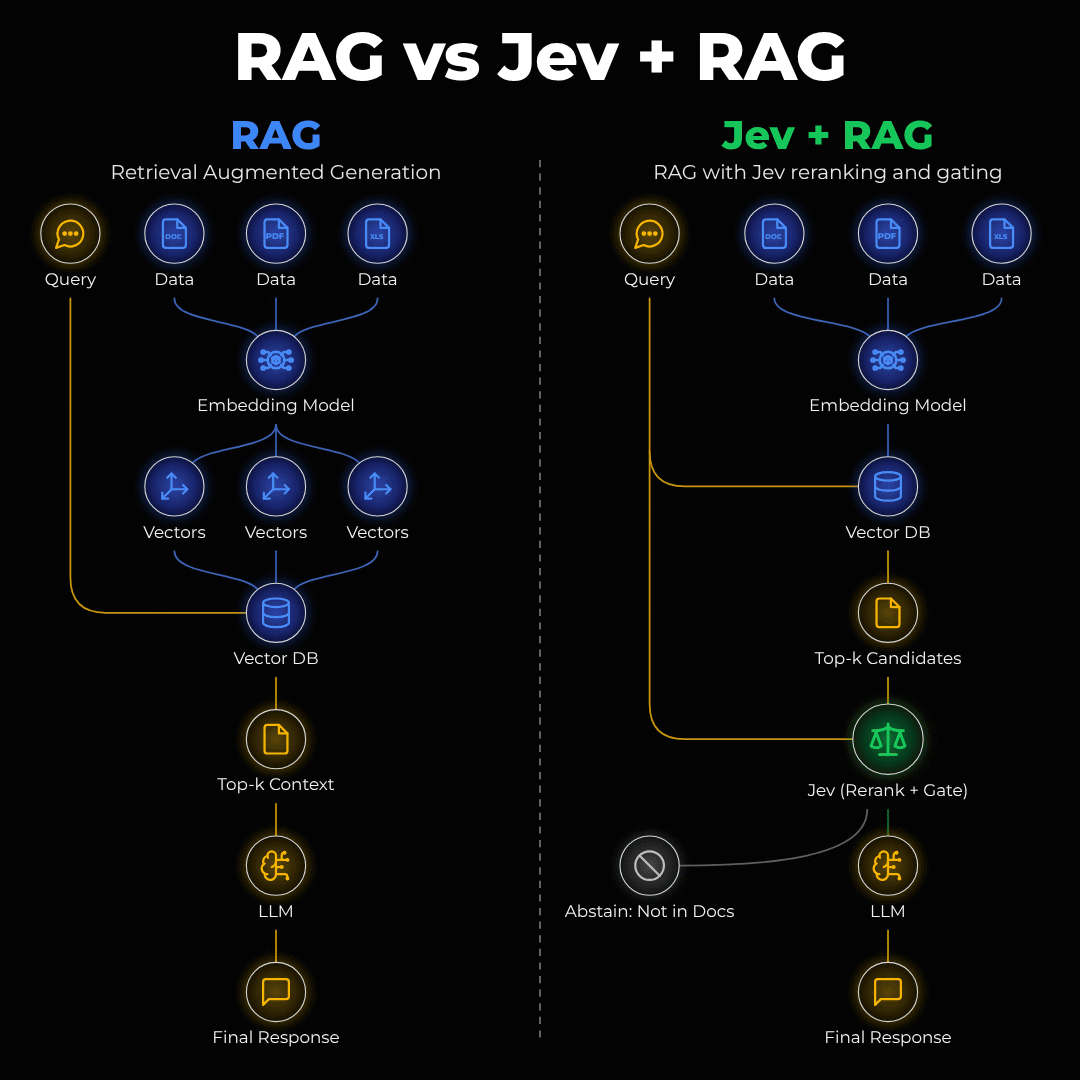
A tutorial builds an agentic RAG support desk using Liquid AI's d1-3B decision model, EmbeddingGemma 2, and In…
Google Flow puts Gemini Omni, Veo and Nano Banana in one web app, letting beginners chat through a storyboard…