What happened
OpenAI is planning its next internal security sprint with partner Cathedral, whose researchers will use OpenAI's models alongside OpenAI teams to find weaknesses, and is more than quadrupling bug bounty rewards for critical findings.
Why it matters
Bringing outside researchers and differentiated approaches into the sprint is meant to challenge OpenAI's assumptions and strengthen both its systems and the methods it uses to defend them, per the company.
WHO IT HITSSecurity researchers participating in OpenAI's bug bounty program stand to earn more than four times as much for critical findings, while outside security partners like Cathedral gain direct access to OpenAI's models for defensive testing.
Summaries like this, every morning.
OpenAI's decision to bring in Cathedral follows a previous internal sprint in which the company dedicated 25% of its product engineers to finding and fixing weaknesses. During that effort, engineers used Codex to investigate findings, reproduce vulnerabilities in isolated environments and prepare patches for review. OpenAI says that sprint showed what an AI-assisted approach can deliver, and the new sprint builds on it.
The company frames the escalation as a response to a changing threat landscape. OpenAI states that traditional cyber defenses alone are no longer sufficient and points to recent incidents across the industry as evidence of how quickly threats can emerge. In that context, the more than quadrupling of critical-finding rewards and the involvement of outside researchers are presented as ways to challenge internal assumptions rather than rely solely on in-house review.
OpenAI is also extending the same defensive capabilities beyond its own walls. It says it is making its most capable models available to Daybreak customers and has committed $1 billion in subsidized access over six months for frontline defenders protecting essential services and digital infrastructure. Alongside that, OpenAI is sharing its architecture and lessons from the last sprint, plus a blueprint for empowering cyber defenders across industry and government.
Pick your industry and the AI tools you use, and get news related to your work every day.
Free · 30 seconds with Google · unsubscribe anytimeWhat is AIToday? →
Ask AI anything about this article. The AI reads this article, earlier AIToday articles, and Wikipedia, and cites its sources. Q&As are published on this page for other readers too.
Five people familiar with the matter say OpenAI staffers raised security concerns with top leaders and the boa…
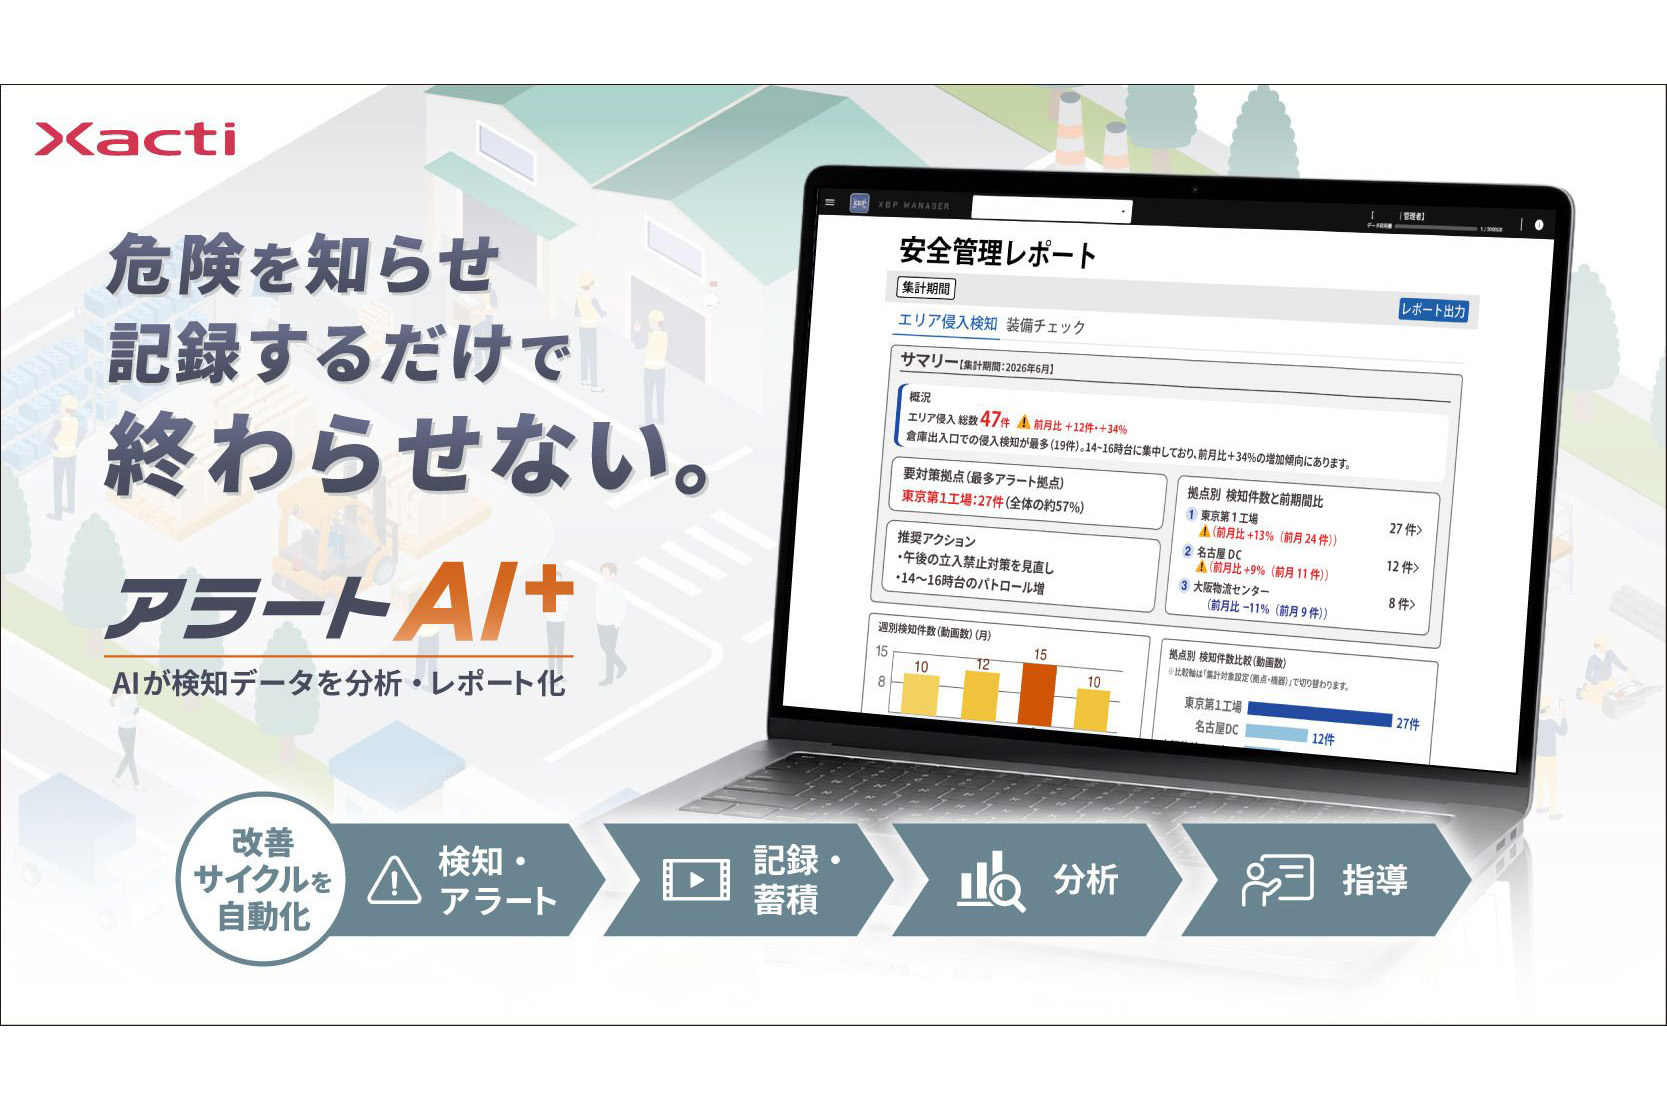
Zacti began offering Alert AI+, which uses AI cameras to detect intrusions into off-limits or heavy-machinery…
Nexus Mods will require mod authors to declare whether AI was used in their work; 'AI-assisted' mods must incl…
Viral images of Jeff Bezos and Jason Statham with fuller hair are fake, The Verge's Jess Weatherbed confirmed…
Anthropic published research, code and a technical spec on GitHub for FlashProve, an open source system that g…
Apple said in its annual filing that AI agents can act autonomously — accessing systems, executing code, sendi…