What happened
Norforge says one hacker used Cairn, an open-source AI platform, to direct largely autonomous agents against more than 100 websites in the US, Canada, Australia, and Japan, with successful breaches taking about 23 hours.
Why it matters
The intrusion shows that off-the-shelf open-source tooling can be repurposed to orchestrate cyberattacks at scale, with the attacker needing only a brief written set of intrusion tactics.
WHO IT HITSSecurity teams at companies running public-facing websites, especially those using third-party vendors for product support pages, may need to review whether open-source AI orchestration tools are being abused against their sites.
Summaries like this, in your inbox every morning.
The attacks came to light because Norforge was scanning for exposed instances of Cairn, an open-source platform that lets users set a start and end point for AI agents and watch them document their progress. That same design, meant for general problem-solving, can be pointed at corporate websites. Norforge found more than 20 exposed Cairn instances it describes as likely malicious, and the one behind the 100-plus breaches was the most active among them.
The victims span the US, Canada, Australia, and Japan, and the companies' responses suggest the damage was limited: John Deere said it saw no indication of sensitive information being accessed, SharkNinja said the affected site was a standalone product-support page and that it contained the threat, and Cummins said it is investigating a potential attack on a third-party vendor's site. Cairn's creator, who goes by @le1xia0, pushed back earlier this month, saying the platform was never a hacking tool and that misuse is a human decision rather than a feature of the engine. Norforge says it is working to get the malicious instances taken down.
Pick your industry and the AI tools you use, and get news related to your work every day.
Free · 30 seconds with Google · unsubscribe anytimeWhat is AIToday? →
Ask AI anything about this article. The AI reads this article, earlier AIToday articles, and Wikipedia, and cites its sources. Q&As are published on this page for other readers too.
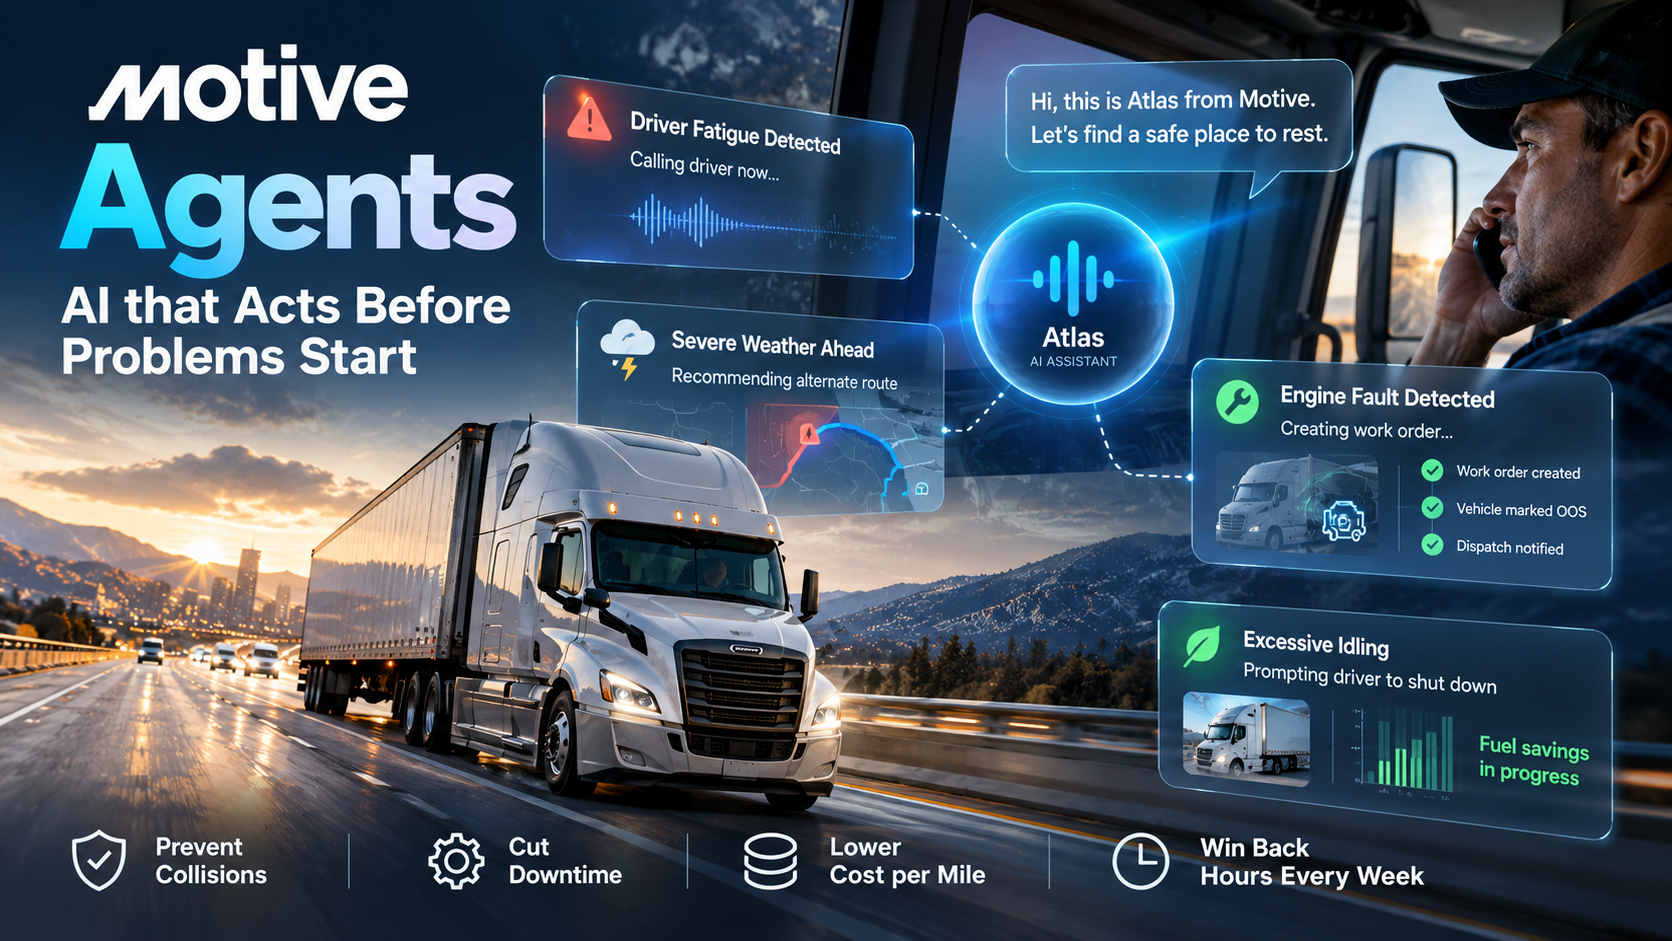
Motive launched Agents, which uses operational data already in its platform to contact drivers, open maintenan…
Stanford University, Together AI, the University of Illinois Urbana-Champaign and Meta unveiled Hybrid Reasoni…
Character.AI filed for bankruptcy after an investment banker found the company unbuyable due to litigation and…
Motive launched Agents, autonomous AI that resolves compliance, maintenance and safety issues without human in…
Anthropic said it would commit 5% of its shares — potentially more if it hits unspecified revenue targets — to…
Anthropic plans a fund holding 5% of its shares, with possible direct payments to workers displaced by AI; CEO…