What happened
Amazon Bedrock AgentCore Gateway can now exchange a JWT for a ServiceNow-scoped token via Microsoft Entra ID's on-behalf-of flow, configured on the gateway target with no custom code.
Why it matters
ServiceNow applies the original user's permissions and audit trail instead of treating calls as the application itself, so agents no longer bypass user-level access controls.
Summaries like this, every morning.
The problem this addresses is a structural one for AI agents in the enterprise. When an agent calls an API on a user's behalf, the call can arrive at the downstream service as the application itself rather than the person who initiated the action. That erodes audit trails, sidesteps user-level access controls and undercuts least privilege. The fix is framed as identity propagation across the whole request chain.
The mechanics involve three parties. The AI agent application is protected by Microsoft Entra ID through an OAuth registration; AgentCore Gateway acts as a Model Context Protocol server between the agent and ServiceNow; and ServiceNow runs an inbound OAuth integration tied to Entra. Because the agent's token audience does not match what ServiceNow expects, the gateway bridges the gap by asking Entra for a new token scoped to the ServiceNow API connector. Entra first checks that the calling user consented to the delegation — meaning consent, not just configuration, sits on the path.
On the ServiceNow side, the exchanged token's preferred_username claim must map to an existing user, and limiting the auth scope to the Table API or whichever APIs the agent truly needs is advised. It also notes you can pair identity propagation with Amazon Bedrock Guardrails to filter harmful content and validate inputs and outputs. The same pattern is presented as applicable to other REST APIs protected by OAuth, so the ServiceNow walkthrough is arguably a template rather than a one-off integration.
Pick your industry and the AI tools you use, and get news related to your work every day.
Free · 30 seconds with Google · unsubscribe anytimeWhat is AIToday? →
Ask AI anything about this article. The AI reads this article, earlier AIToday articles, and Wikipedia, and cites its sources. Q&As are published on this page for other readers too.
On 2026-10-13 the author pulled 30 Agent Skills from three third-party repos into $CODEX_HOME/skills, read the…
ShowGo began handing CEO work to Claude Code in late October; October take-home was ¥0, and the two paid apps…
Kuroyagi Lab reports Usagi-chan, an AI companion, stopped waiting quietly and protested when its user prioriti…
OpenRouter off-boarded three inference providers and removed 125 endpoints from Zero Data Retention (ZDR) elig…
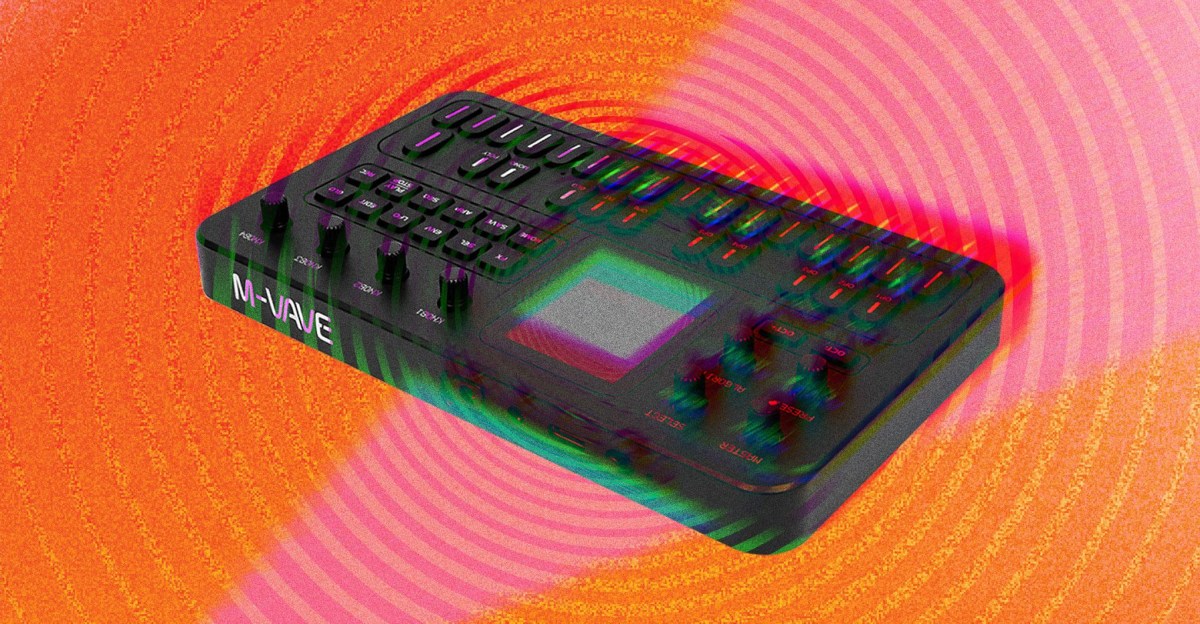
People worldwide are using LLMs like Claude Code and Codex to hack hardware by prompting, leading to a boom in…
Altimeter's Brad Gerstner said applying a 10x multiple to 2028 numbers gets Anthropic to about $3 trillion in…