What happened
Anthropic has integrated its most capable model, Claude Mythos 5, into Claude Security, a tool that scans codebases for vulnerabilities and recommends patches. The tool is available in public beta for Enterprise customers, with each finding categorized by CWE (a standard classification of software flaws), severity rating, and suggested fix. Mythos 5 is also being embedded into partner security products protecting hospitals, utilities, and banks.
Why it matters
Claude Mythos 5 is Anthropic's most capable model, particularly for cyber tasks, and has been kept from broad release. By channeling it through security products rather than making it publicly available, Anthropic aims to strengthen defenders against threats without giving attackers access to new AI-powered capabilities. Humans must still approve every patch before deployment.
What to watch
Several security partners already use Claude Opus for their tools and are expected to migrate to Mythos 5. Security vendors can sign up for partnership access. Scans count as normal token usage, so pricing follows standard Enterprise billing.
Summaries like this, in your inbox every morning.
Anthropic is taking a narrowly targeted approach to deploying its most powerful model, Claude Mythos 5, by anchoring it to defensive cybersecurity use cases rather than releasing it as a general-purpose product. The integration into Claude Security and existing partner workflows (replacing Claude Opus in some cases) reflects a deliberate strategy: keep the model's capabilities away from potential adversaries while maximizing benefit to defenders. This mirrors a broader tension in AI safety—how to allow beneficial deployment without enabling misuse. By requiring human approval of every patch and limiting direct end-user access to the model itself, Anthropic is maintaining a layer of human oversight even as it scales the tool's use.
Pick your industry and the AI tools you use, and get news related to your work every day.
Free · 30 seconds with Google · unsubscribe anytimeWhat is AIToday? →
Ask AI anything about this article. The AI reads this article, earlier AIToday articles, and Wikipedia, and cites its sources. Q&As are published on this page for other readers too.
Nvidia is in early talks to acquire open-weight model developer Reflection AI outright, take a bigger stake, o…
Cerebras Systems announced it is powering the Ultrafast mode for OpenAI's GPT-5.6 Sol, delivering up to 750 ou…
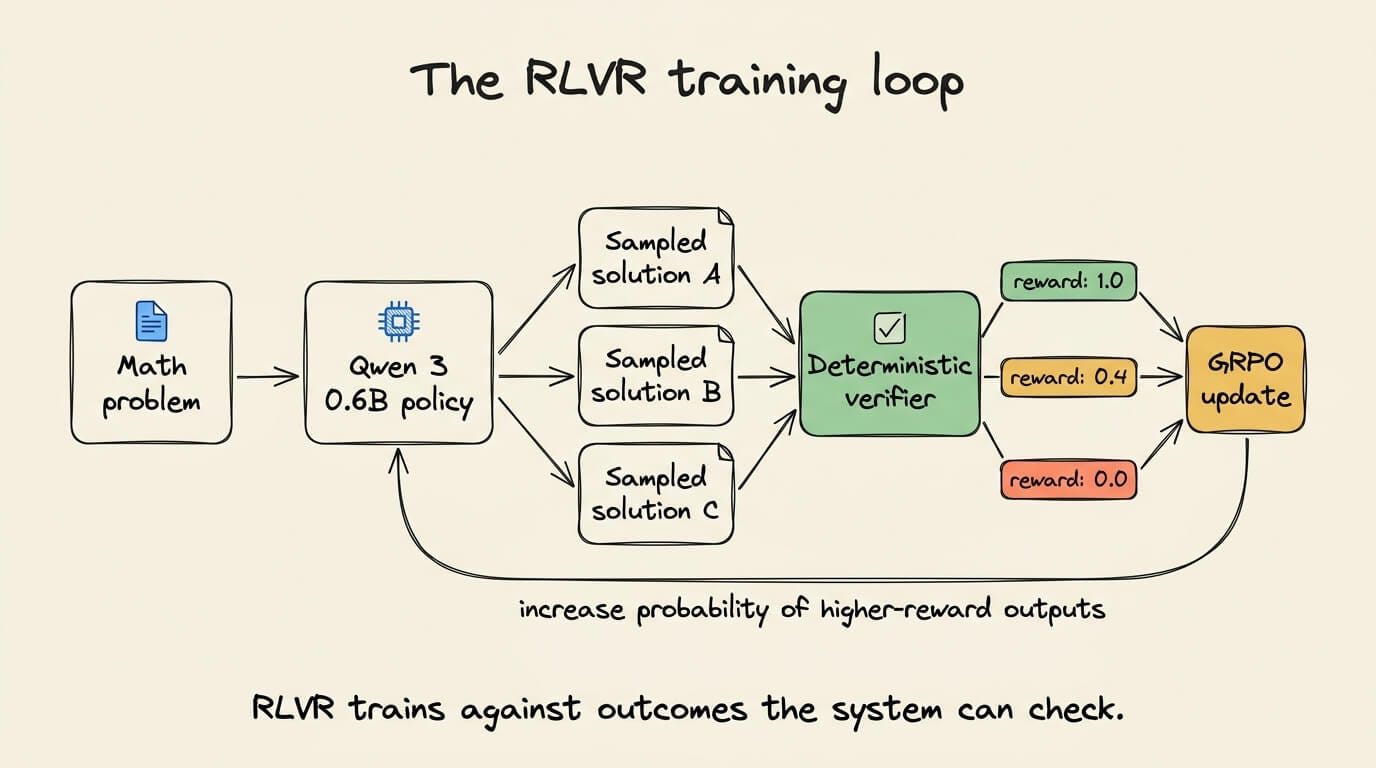
A walkthrough uses a custom four-signal reward (correctness 0.6, parseability 0.2, format 0.1, reasoning 0.1)…
Anthropic's Claude Code 2.1.294 fixed natural-language prompt and agent hooks that were allowing operations th…

Over three days (Oct 7–9, 2026) Masayoshi Uehara wired ChatGPT's dots into real Gmail, Calendar, Drive, GitHub…
CEO Brian Chesky said Airbnb is now an "AI-native company." As of Q1 2026, about 60% of engineer-produced code…

