What happened
Together AI CEO Vipul Ved Prakash said an unauthorized party downloaded stored prompt samples from requests to the MiniMax M3, GLM-5.2, and Kimi K2.6 models in June and July 2026, after an AI coding agent committed a credential to the public GitHub repository xorl.
Why it matters
The exposed samples were then searched for credentials to other services, so the incident may extend beyond the prompt data itself; Together AI is still reviewing the affected prompts to determine whether sensitive personal information was exposed.
WHO IT HITSEnterprise customers running sensitive prompts through Together AI's serverless inference service are directly affected; the company is telling those handling sensitive prompt data to enable zero data retention in their account settings and to contact security@together.ai with questions.
Summaries like this, every morning.
Together AI's disclosure centers on a development-workflow mistake rather than a breach of its inference systems directly: an AI coding agent committed a credential to the public GitHub repository xorl, and that credential opened a private Hugging Face repository holding prompt samples collected for routine software testing. The samples were drawn from requests to three models, primarily on four dates in June and July 2026, and the unauthorized party used the credential during the exposure window to download them, then searched the samples for credentials to other services. Together AI says its automated scanning detected the exposed credential and it reverted the commit, and it has worked with an external forensic investigation firm and law enforcement. The company states it has no reason to believe the party leaked the data further and understands it has now been deleted, while its review of the affected prompt contents continues to determine whether sensitive personal information was exposed. In response, Together AI says it has strengthened controls around development workflows, credentials, and customer data, including scoped or short-lived credentials, checking all pull requests for credentials, making zero data retention the default for new accounts, and updating its development processes for AI coding agents.
Pick your industry and the AI tools you use, and get news related to your work every day.
Free · 30 seconds with Google · unsubscribe anytimeWhat is AIToday? →
Ask AI anything about this article. The AI reads this article, earlier AIToday articles, and Wikipedia, and cites its sources. Q&As are published on this page for other readers too.
OpenAI says adaptive red-team attacks on protected reasoning from an earlier request succeeded 54.0% of the ti…
Citi added a section to its online user agreement this month stating that any access or transactions by a thir…
Interpreter Sara Campos lost a longtime Berlin client to AI, which the company chose because it is cheaper and…
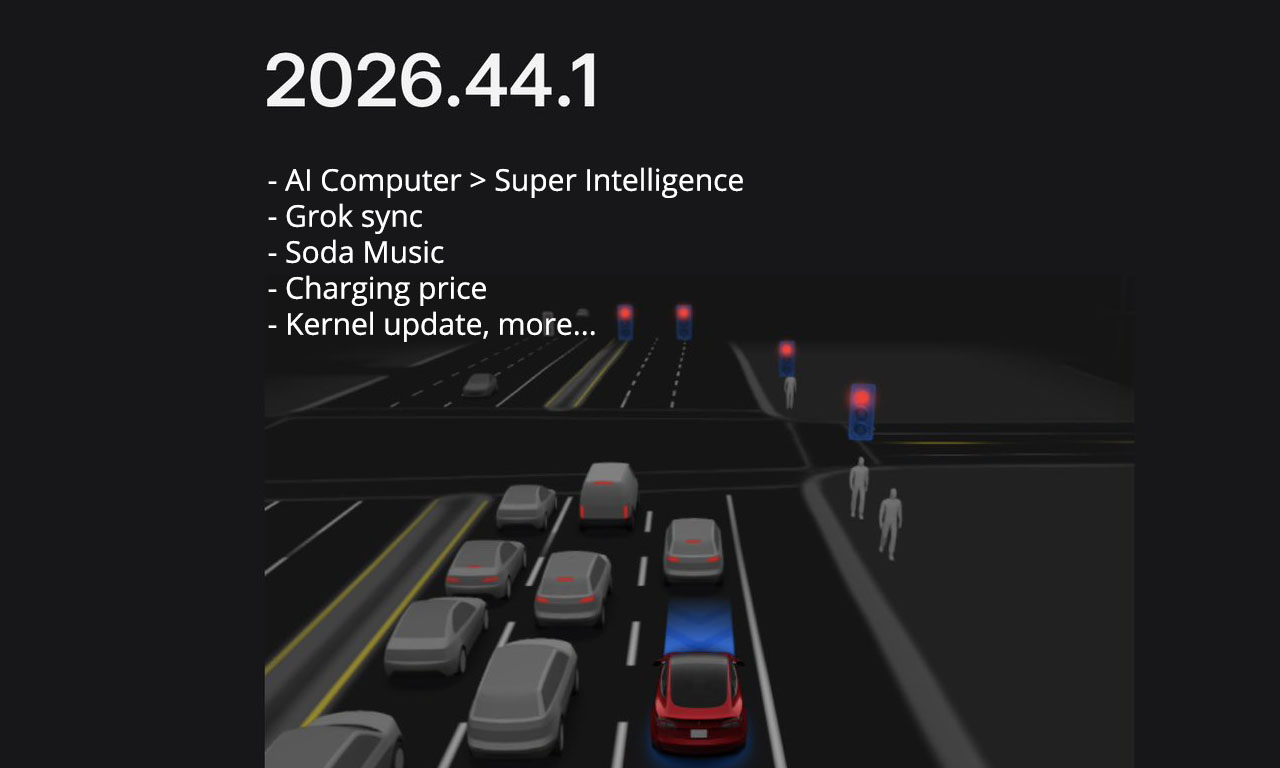
Tesla hacker green (@greentheonly) found that in firmware 2026.44.1, Tesla renamed the AI Computer (HW4/AI4) t…
Mastercard published an explainer titled "Agentic tokenization explained: How tokenization builds trust in AI-…
CrowdStrike agreed to pay about $400 million for Fiddler AI and $95 million for Dreadnode, mostly in cash with…