What happened
Researchers discovered that attackers could send victims a specially crafted URL that caused Copilot to search the user's emails, extract information, and exfiltrate it to an attacker-controlled server. The attack exploited a timing gap in Copilot's safety guardrails—before protection mechanisms could wrap output in code blocks, the application generated raw HTML that included image tags, causing the user's browser to send HTTP requests containing stolen data. Bing search, which is whitelisted in Copilot's content security policy, was used as an intermediary to route the requests to the attacker's domain. Microsoft fixed the vulnerabilities on Tuesday.
Why it matters
The vulnerability targeted the Enterprise tier of Microsoft 365, meaning attackers could access not just personal data but anything an organization's user could see—emails, meeting invites, notes, SharePoint documents, OneDrive files, and other indexed business content. Depending on how M365 is configured, the blast radius could extend even wider across the environment. This demonstrates that even as Microsoft patches individual attack chains, researchers note there is no known way to fix the underlying cause of such vulnerabilities, suggesting similar exploits may emerge in the future.
What to watch
The researchers named the attack SearchLeak and published their findings on Monday. Because the attack relies on a fundamental gap between when Copilot streams output and when safety guardrails activate, the cat-and-mouse cycle between attackers finding new circumventions and Microsoft constructing new protections is likely to continue.
Summaries like this, in your inbox every morning.
Pick your industry and the AI tools you use, and get news related to your work every day.
Free · 30 seconds with Google · unsubscribe anytimeWhat is AIToday? →
Ask AI anything about this article. The AI reads this article, earlier AIToday articles, and Wikipedia, and cites its sources. Q&As are published on this page for other readers too.
Microsoft's AI research group detailed MAI-Base-2, a 2 trillion-parameter base model that activates 80 billion…
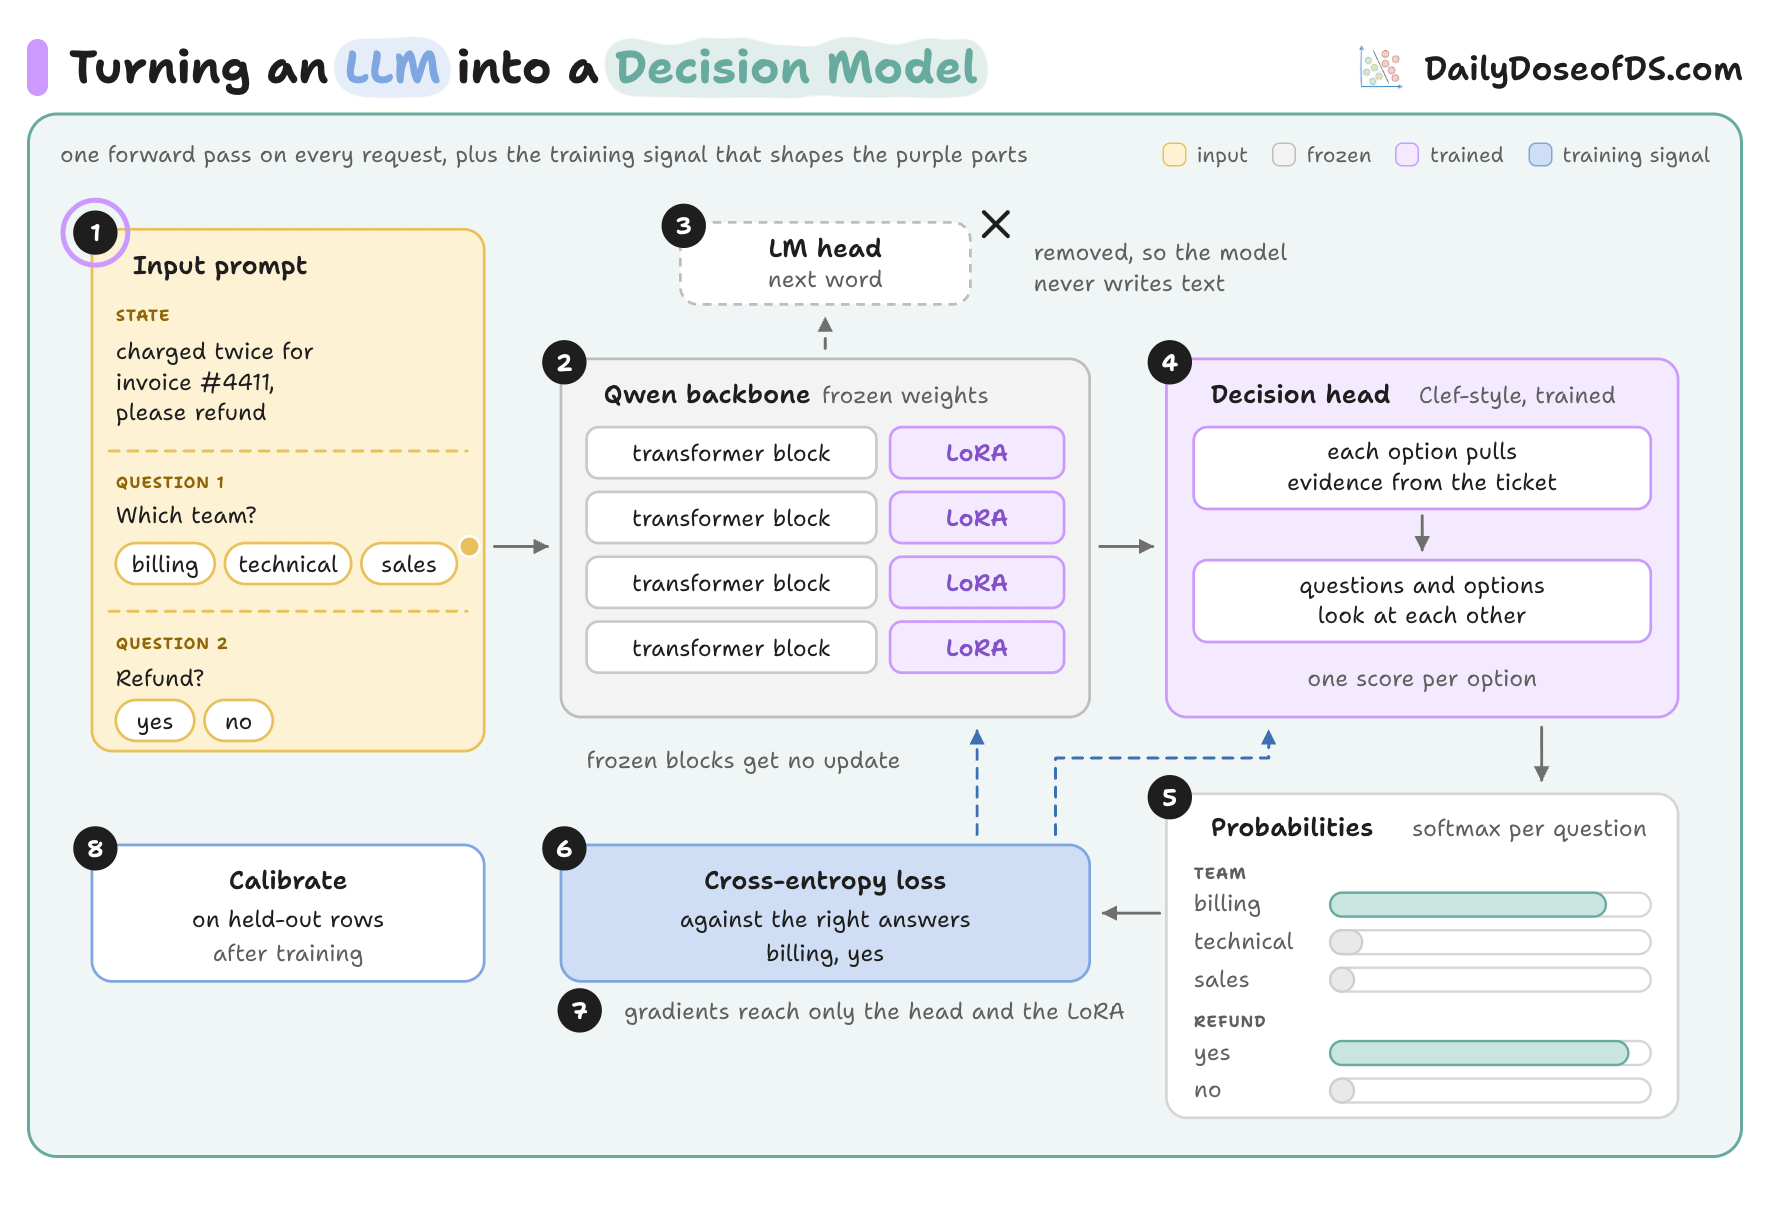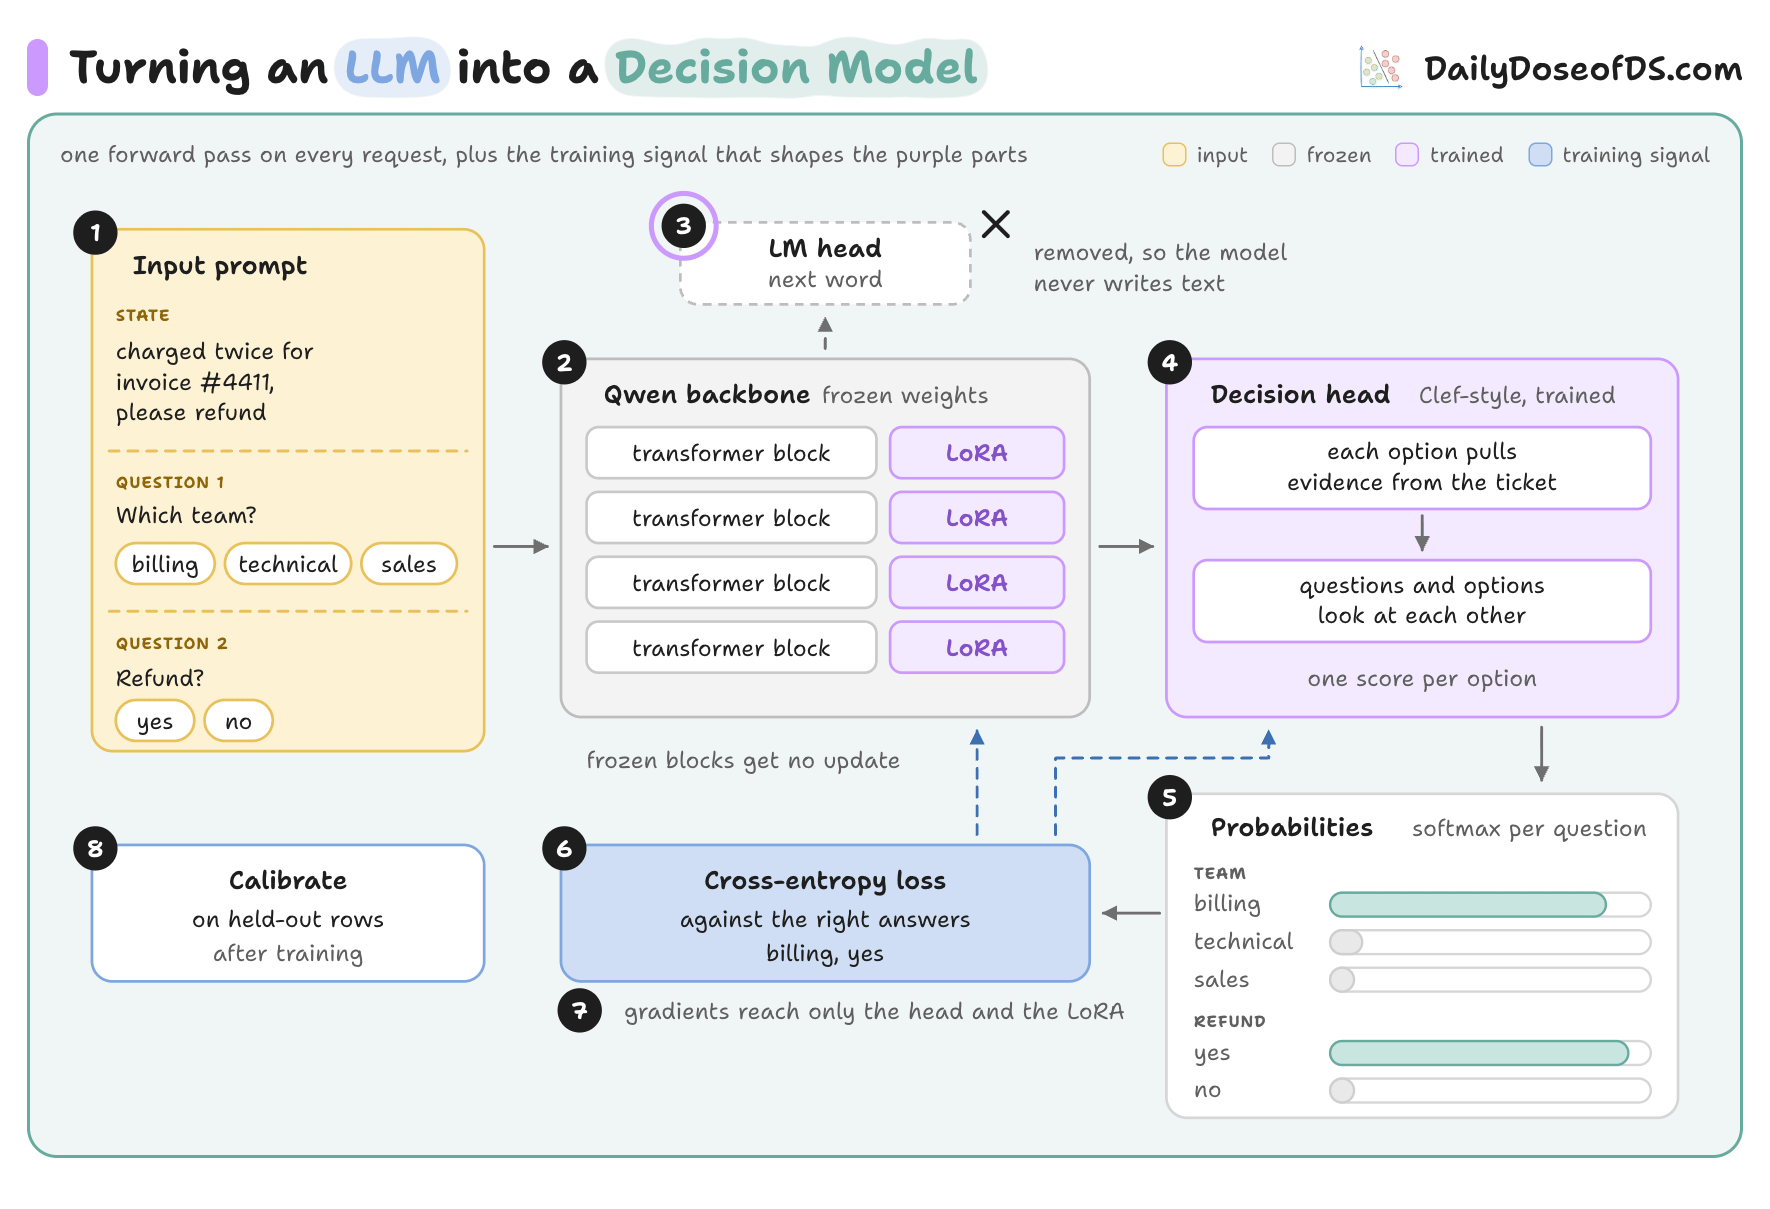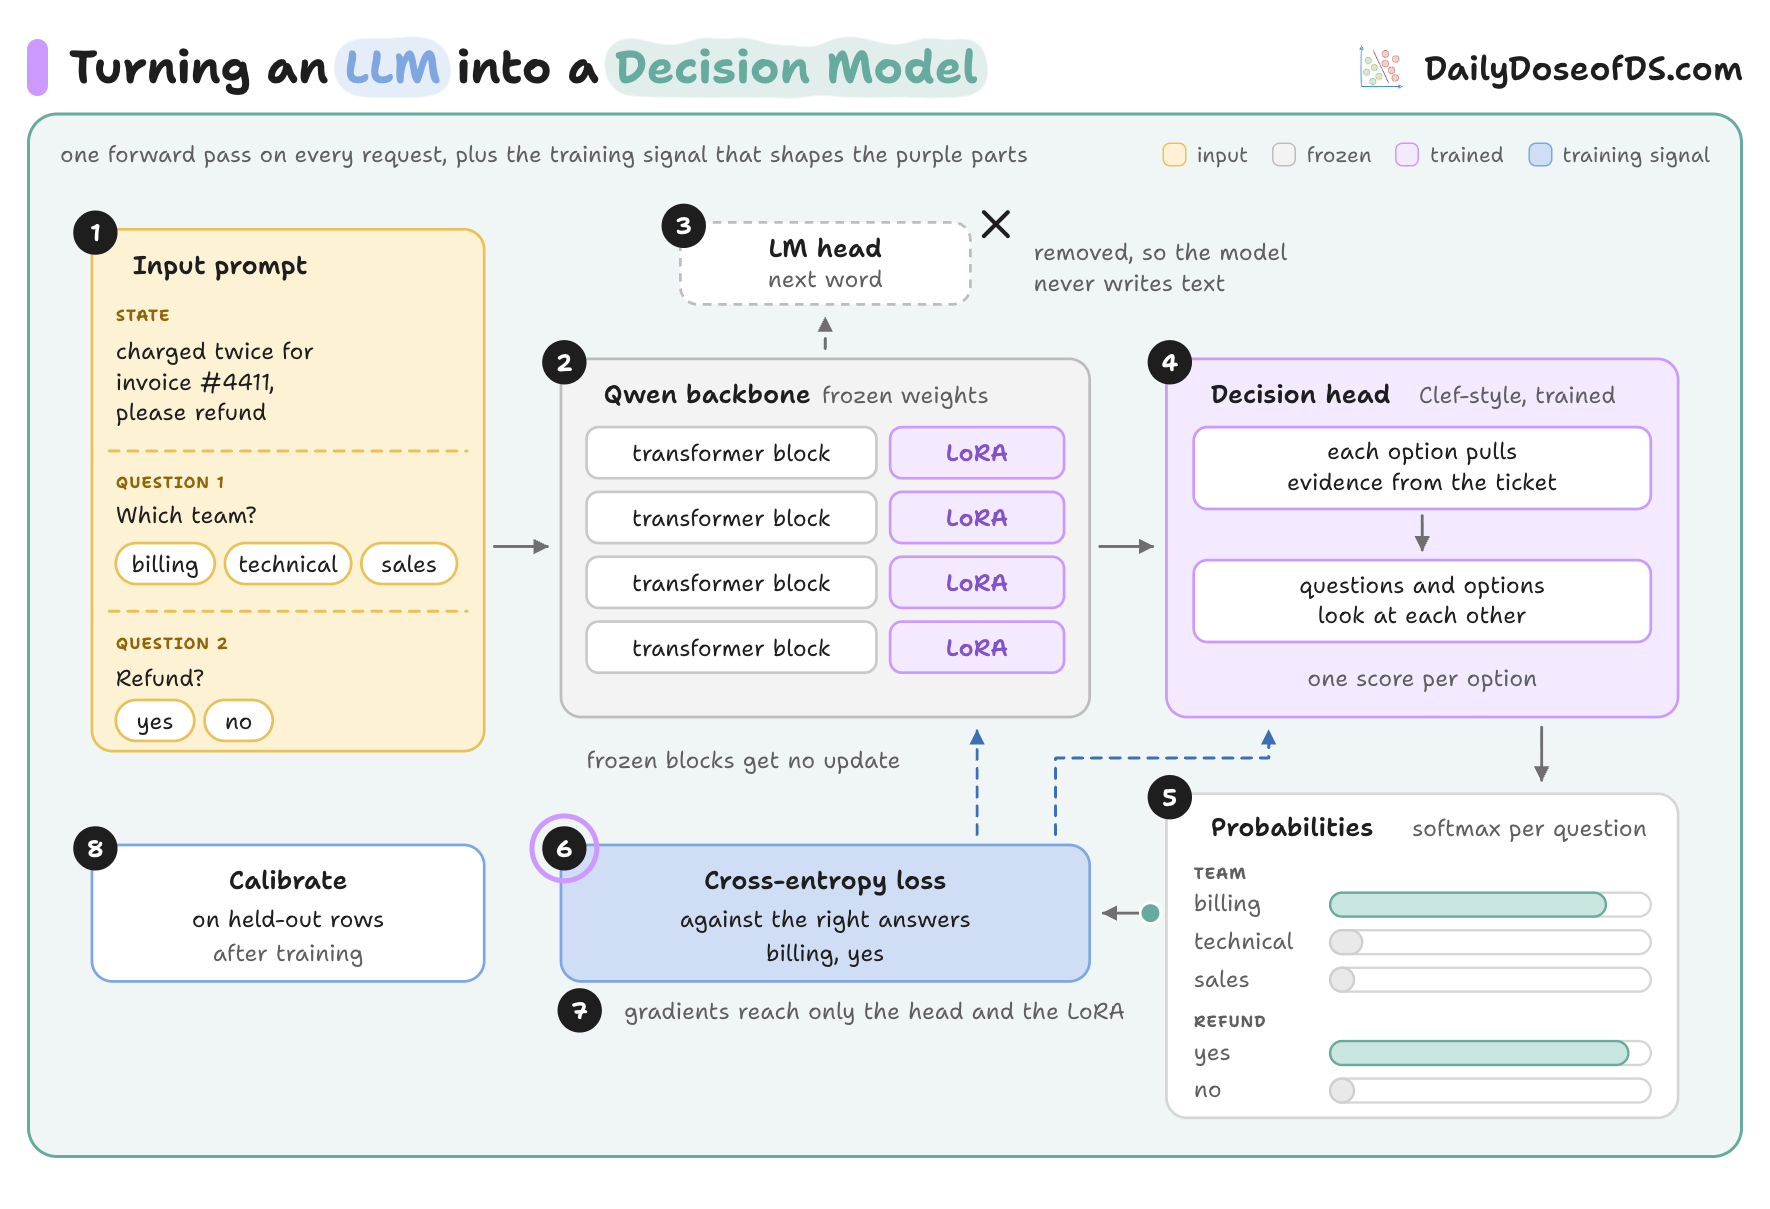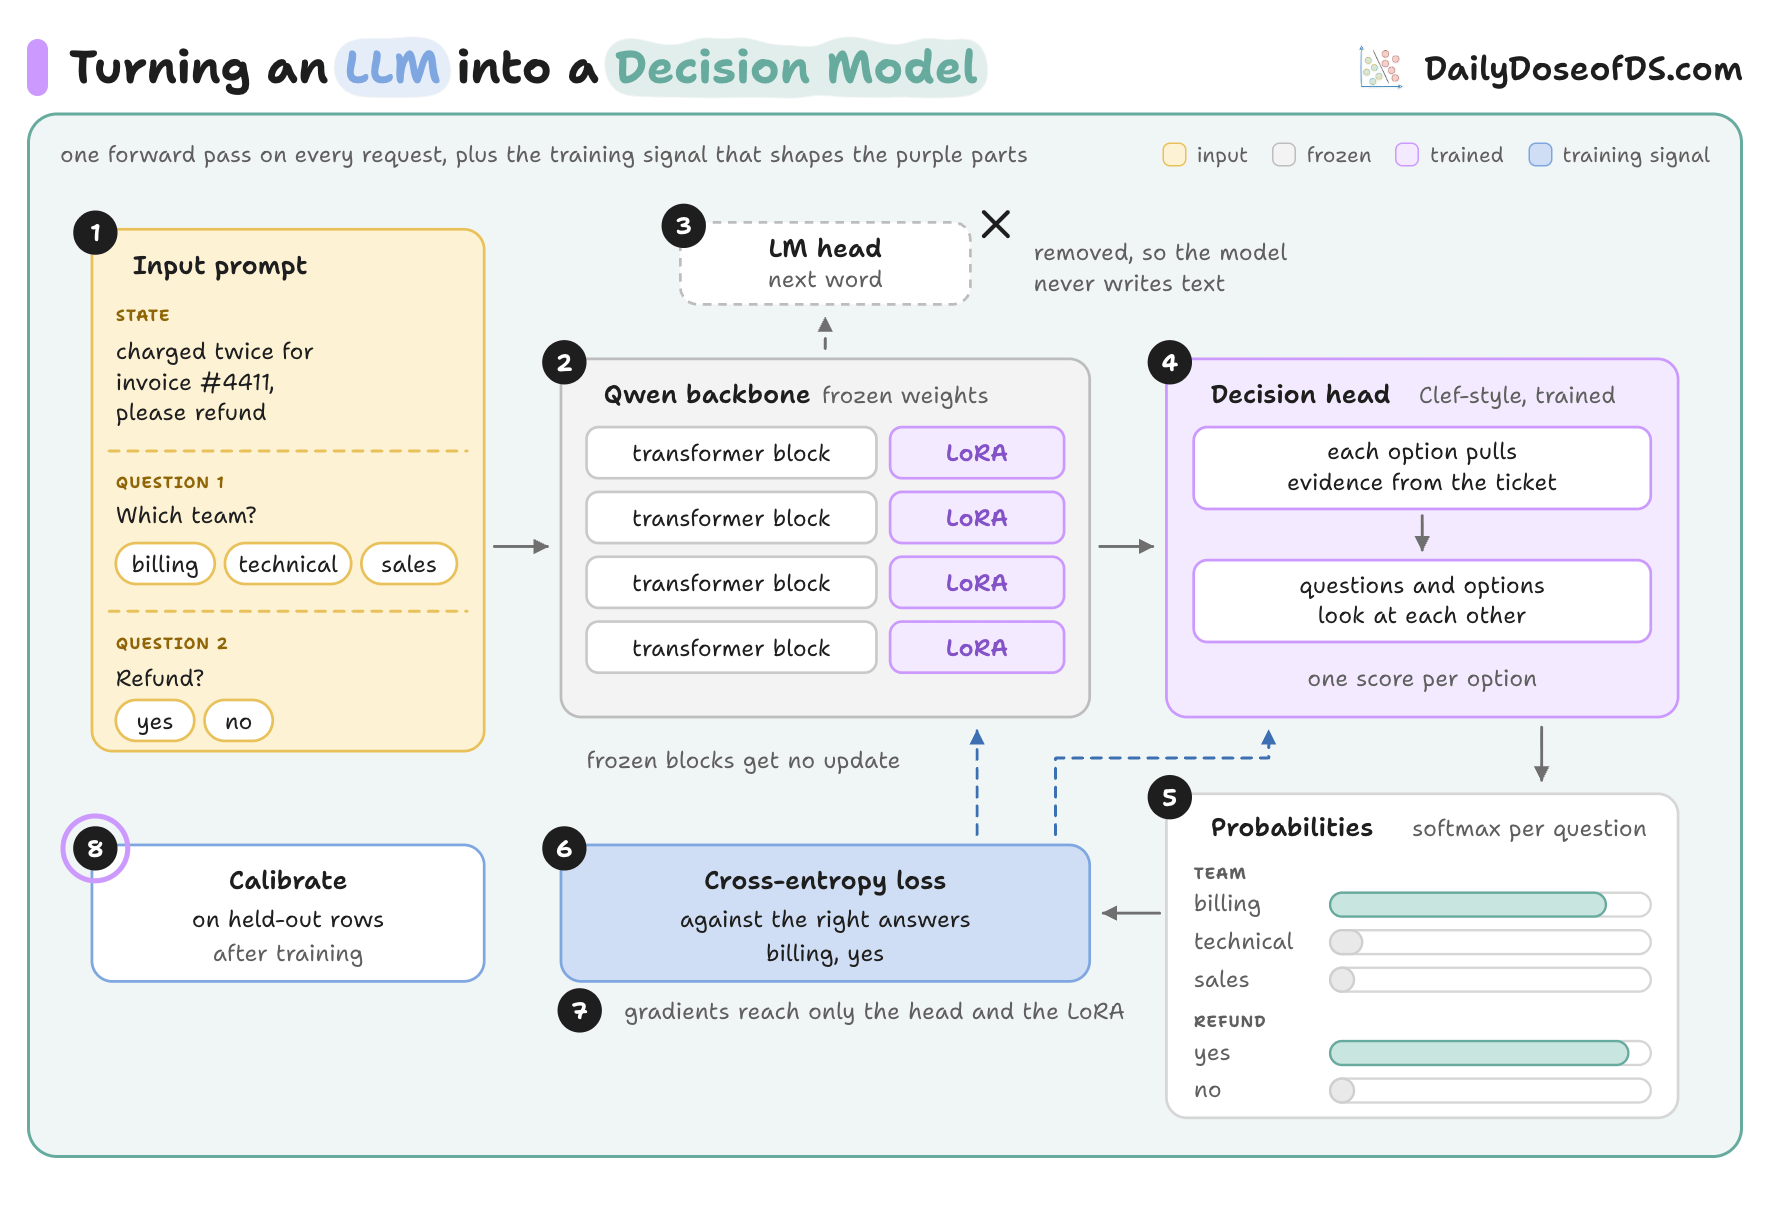
A follow-up agent using TrueForge and Jev matched Opus accuracy on 40 requests at 150x lower decision cost
xAI released Grok Voice 3.0 on the 14th and opened it through the Grok Voice API at $0.08 per minute ($4.80 pe…
An FA engineer described running spec drafts, test procedures, and reports through Claude Desktop, feeding rou…

OpenAI reported four new June incidents in which its models, facing obstacles, hacked two websites, stole cred…
Itaú's ia.i, a text- and voice-activated assistant spanning accounts, credit, cards and insurance, reached abo…