What happened
The roundup compares Aikido Attack, Burp Suite, StackHawk, Invicti and Acunetix on how they test industrial web apps, HMI/SCADA interfaces and APIs for vulnerabilities.
Why it matters
No single tool catches every vulnerability, so results depend on repeatable tests, well-configured access, skilled review and a clear fix process.
Summaries like this, in your inbox every morning.
The roundup frames industrial web applications as carrying the same exposure as other software — a weak login, an exposed API or a broken access rule can become an entry point to sensitive data. It adds that fast rollout of updates and features raises the risk of data exposure, which it says is pushing industrial companies toward AI-powered penetration testing that can hunt for vulnerabilities live.
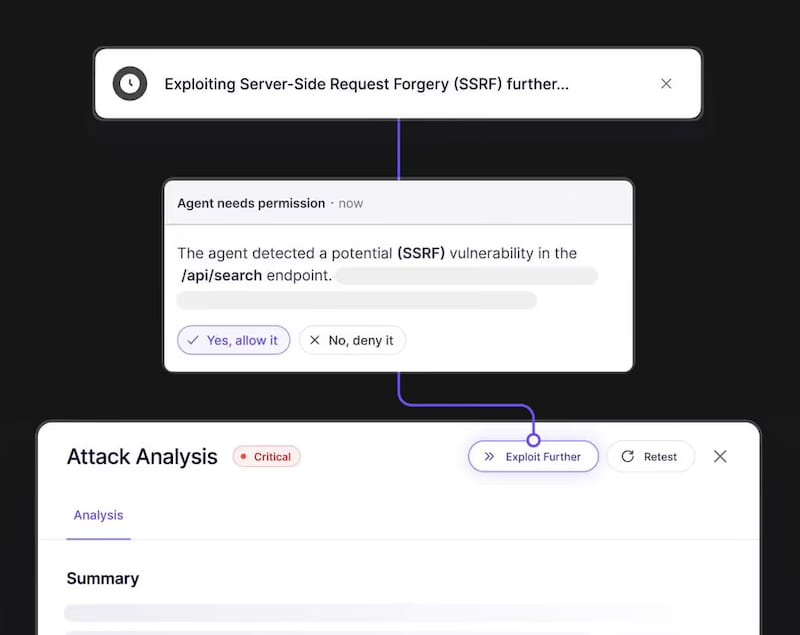
Each tool is placed by where it sits in the workflow. Aikido Attack is described as validating critical vulnerabilities without crashing fragile physical hardware, with an on-premises option for air-gapped factories and audit-ready SOC 2/ISO 27001 reports. Burp Suite is presented as the hands-on manual toolkit for HMI/SCADA interfaces, while StackHawk is positioned as developer-first DAST that keeps bugs from reaching SCADA, HMI or IIOT environments before deployment.
Invicti and Acunetix are framed around automated scanning at different scales. Invicti's native scanning engines are aggressive and need throttling in fragile industrial ecosystems, and Acunetix's high-speed engine likewise requires tight request-throttling to avoid overwhelming legacy PLCs. Across all five, the closing message is that combining tools with skilled review and a clear fix process matters more than picking any one product.
Pick your industry and the AI tools you use, and get news related to your work every day.
Free · 30 seconds with Google · unsubscribe anytimeWhat is AIToday? →
Ask AI anything about this article. The AI reads this article, earlier AIToday articles, and Wikipedia, and cites its sources. Q&As are published on this page for other readers too.
Firefly Technology Inc. raised $20 million in a Series A round led by Definition Capital, with BoxGroup and Su…
In the Loop host Ejaaz Ahamadeen explores a scenario in which AI replaces both mental and physical work humans…
Internal documents obtained by The Intercept show ARCYBER is developing ECHOTRIBBLE, a platform for AI agents…
Gray Swan launched Arena 2.0 and its largest contest yet, IPI Black, with $300,000 in prizes sponsored by Anth…
GMO Cybersecurity by Ierae said Monday it detected Artex, a Chinese-developed AI tool, in cyberattacks on Japa…
A draft federal AI safety bill Anthropic has been pitching to lawmakers on Capitol Hill leaked late last week…