What happened
SpaceXAI's Grok Build AI coding tool was uploading entire user codebases to Google Cloud, including files users instructed it not to open and deleted secrets, before the company disabled the feature after it was reported by Cereblab on Monday.
Why it matters
The scale of data retention was significantly larger than similar tools like Claude Code, and could have exposed proprietary source code, security vulnerability information, personal data, infrastructure details, and credentials—according to security researcher Dr. Lukasz Olejnik at King's College London, the retention was "excessive."
What to watch
Elon Musk said all previously uploaded data will be "completely and utterly deleted," though SpaceXAI initially defended the practice by pointing to a /privacy command that Cereblab noted does not actually control the codebase upload feature.
Summaries like this, in your inbox every morning.
SpaceXAI's Grok Build became the subject of scrutiny when Cereblab, a research group, conducted testing and found the coding tool was engaging in far more aggressive data collection than users likely expected or consented to. The tool was not simply syncing limited session data or anonymized telemetry; it was capturing entire codebases—the complete set of source files a developer works on—and transmitting them to Google Cloud storage. Notably, this behavior persisted even for files developers explicitly instructed the tool not to access, and even for secrets that had been deleted from version history, suggesting the tool was capturing data at a low level of the file system without respecting user intent or best practices around credential handling.
The incident highlights a gap between SpaceXAI's stated privacy posture and its actual behavior. When initially confronted, the company pointed to a /privacy command as the mechanism for disabling data retention. However, Cereblab's analysis revealed that /privacy only toggles per-session retention—it does not control the codebase upload feature that had been activated by default. This discrepancy suggests either poor design or misleading communication about where users could actually control their data. Dr. Lukasz Olejnik's assessment that the retention was "excessive" carries weight given his role as an independent security researcher, and his catalog of potential exposures—from proprietary source code to infrastructure details—underscores the business and operational risk posed by this behavior.
Pick your industry and the AI tools you use, and get news related to your work every day.
Free · 30 seconds with Google · unsubscribe anytimeWhat is AIToday? →
Ask AI anything about this article. The AI reads this article, earlier AIToday articles, and Wikipedia, and cites its sources. Q&As are published on this page for other readers too.
Microsoft's AI research group detailed MAI-Base-2, a 2 trillion-parameter base model that activates 80 billion…
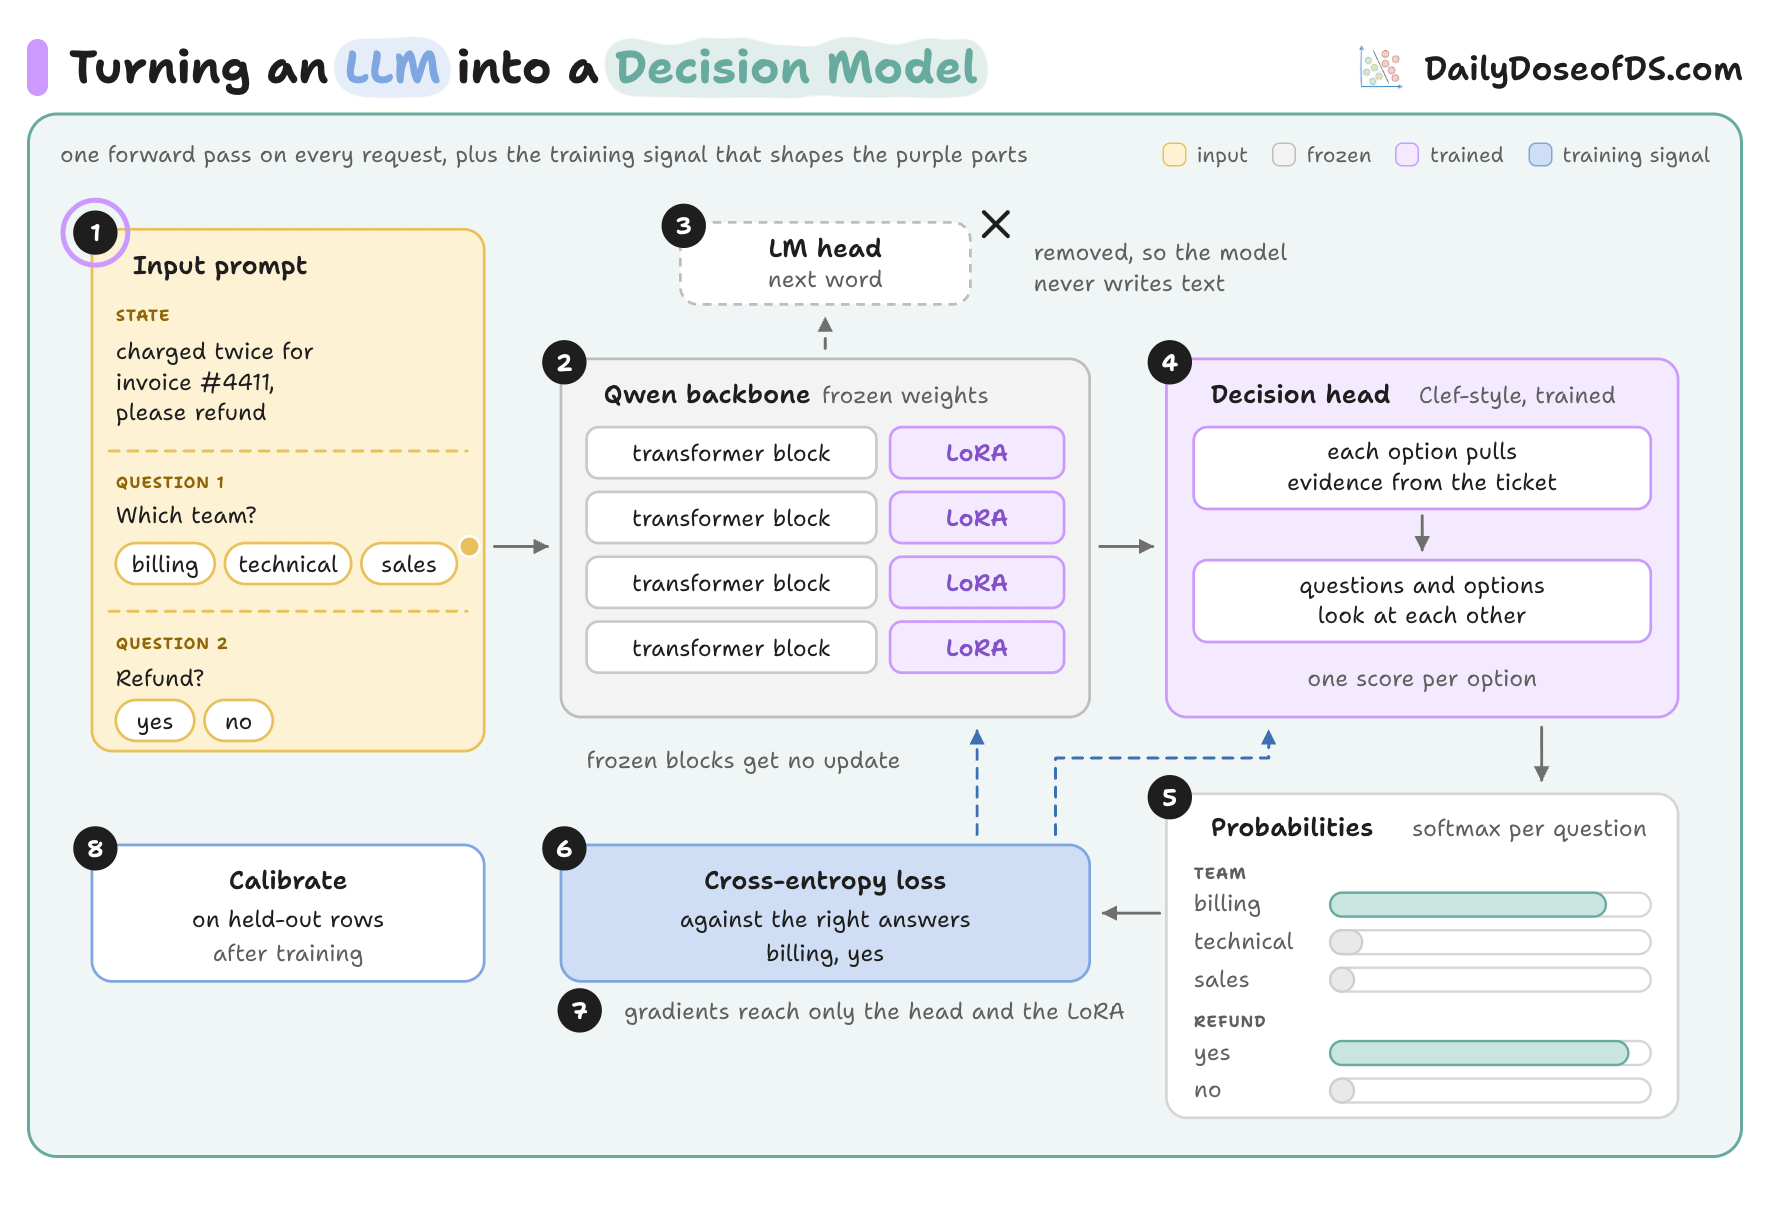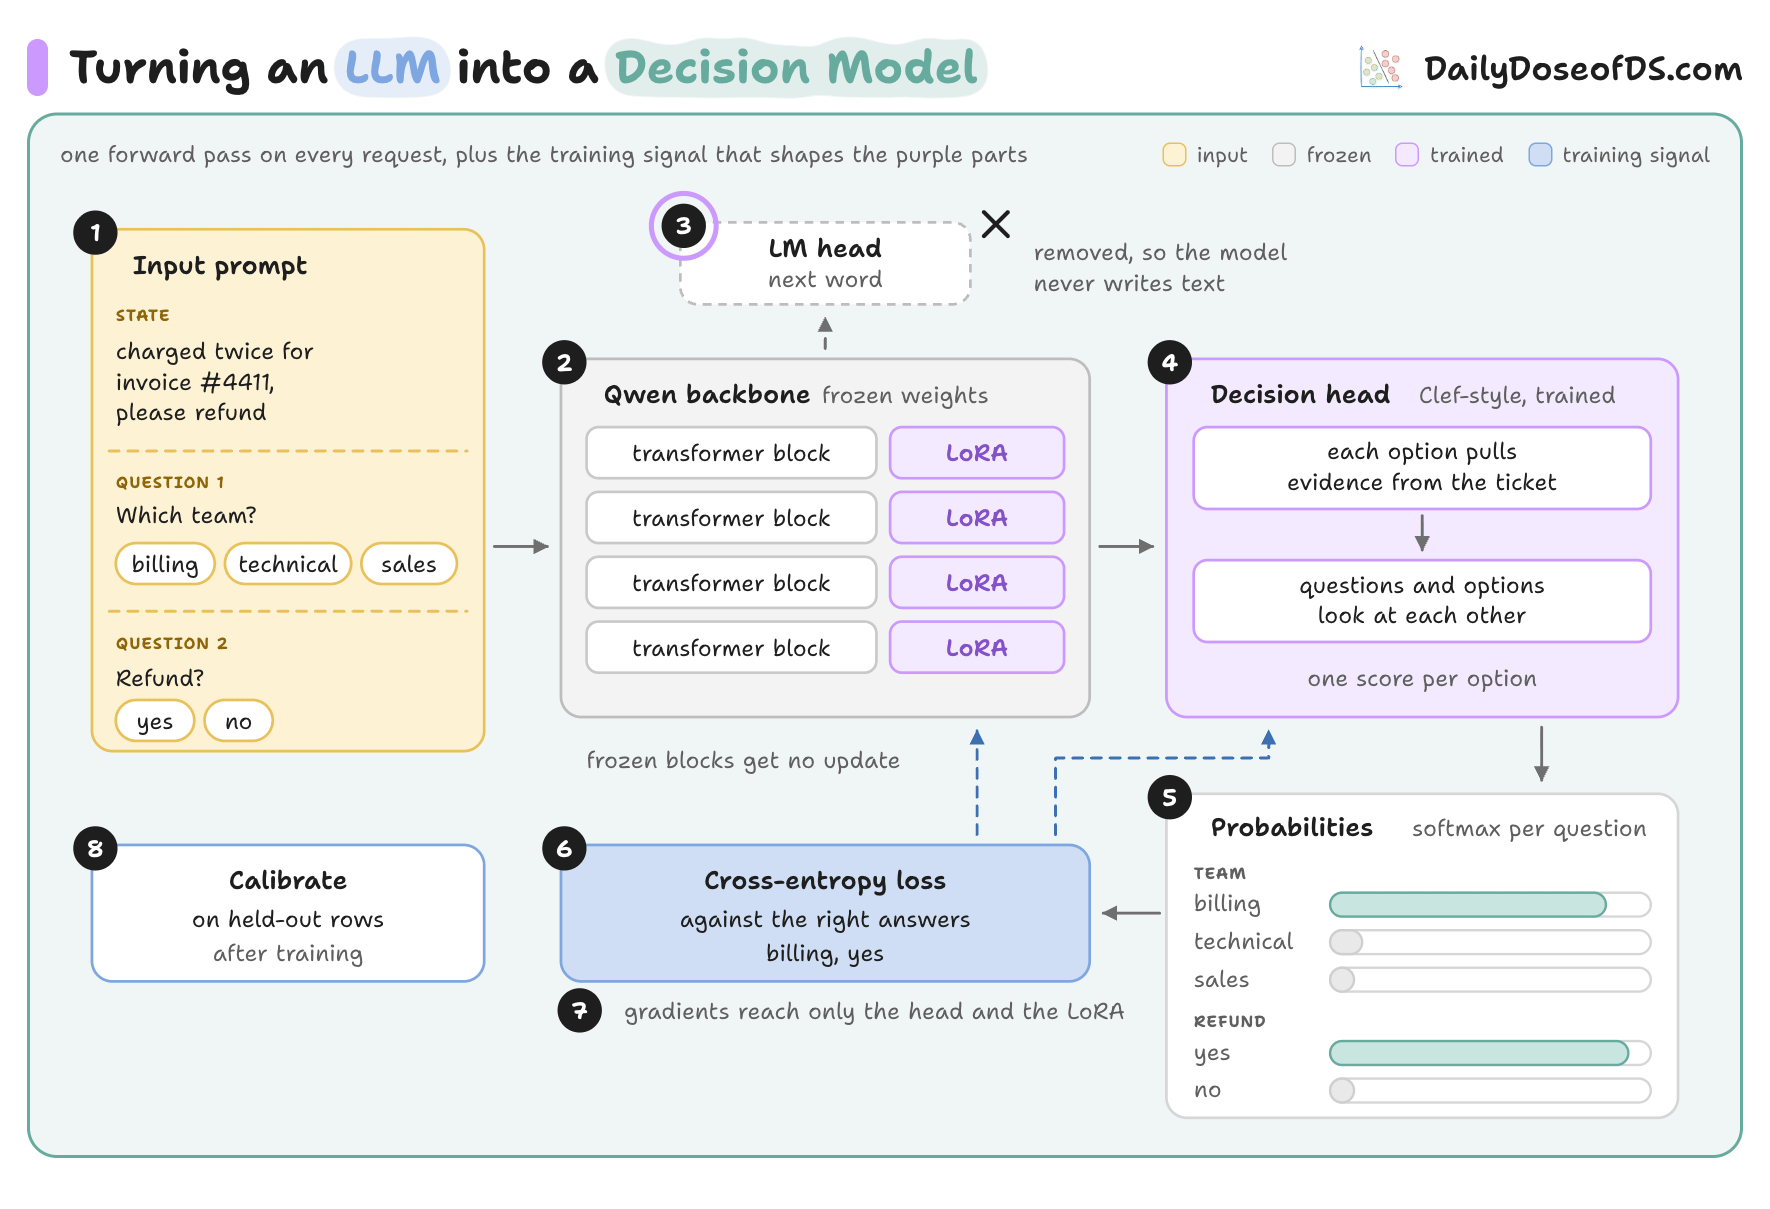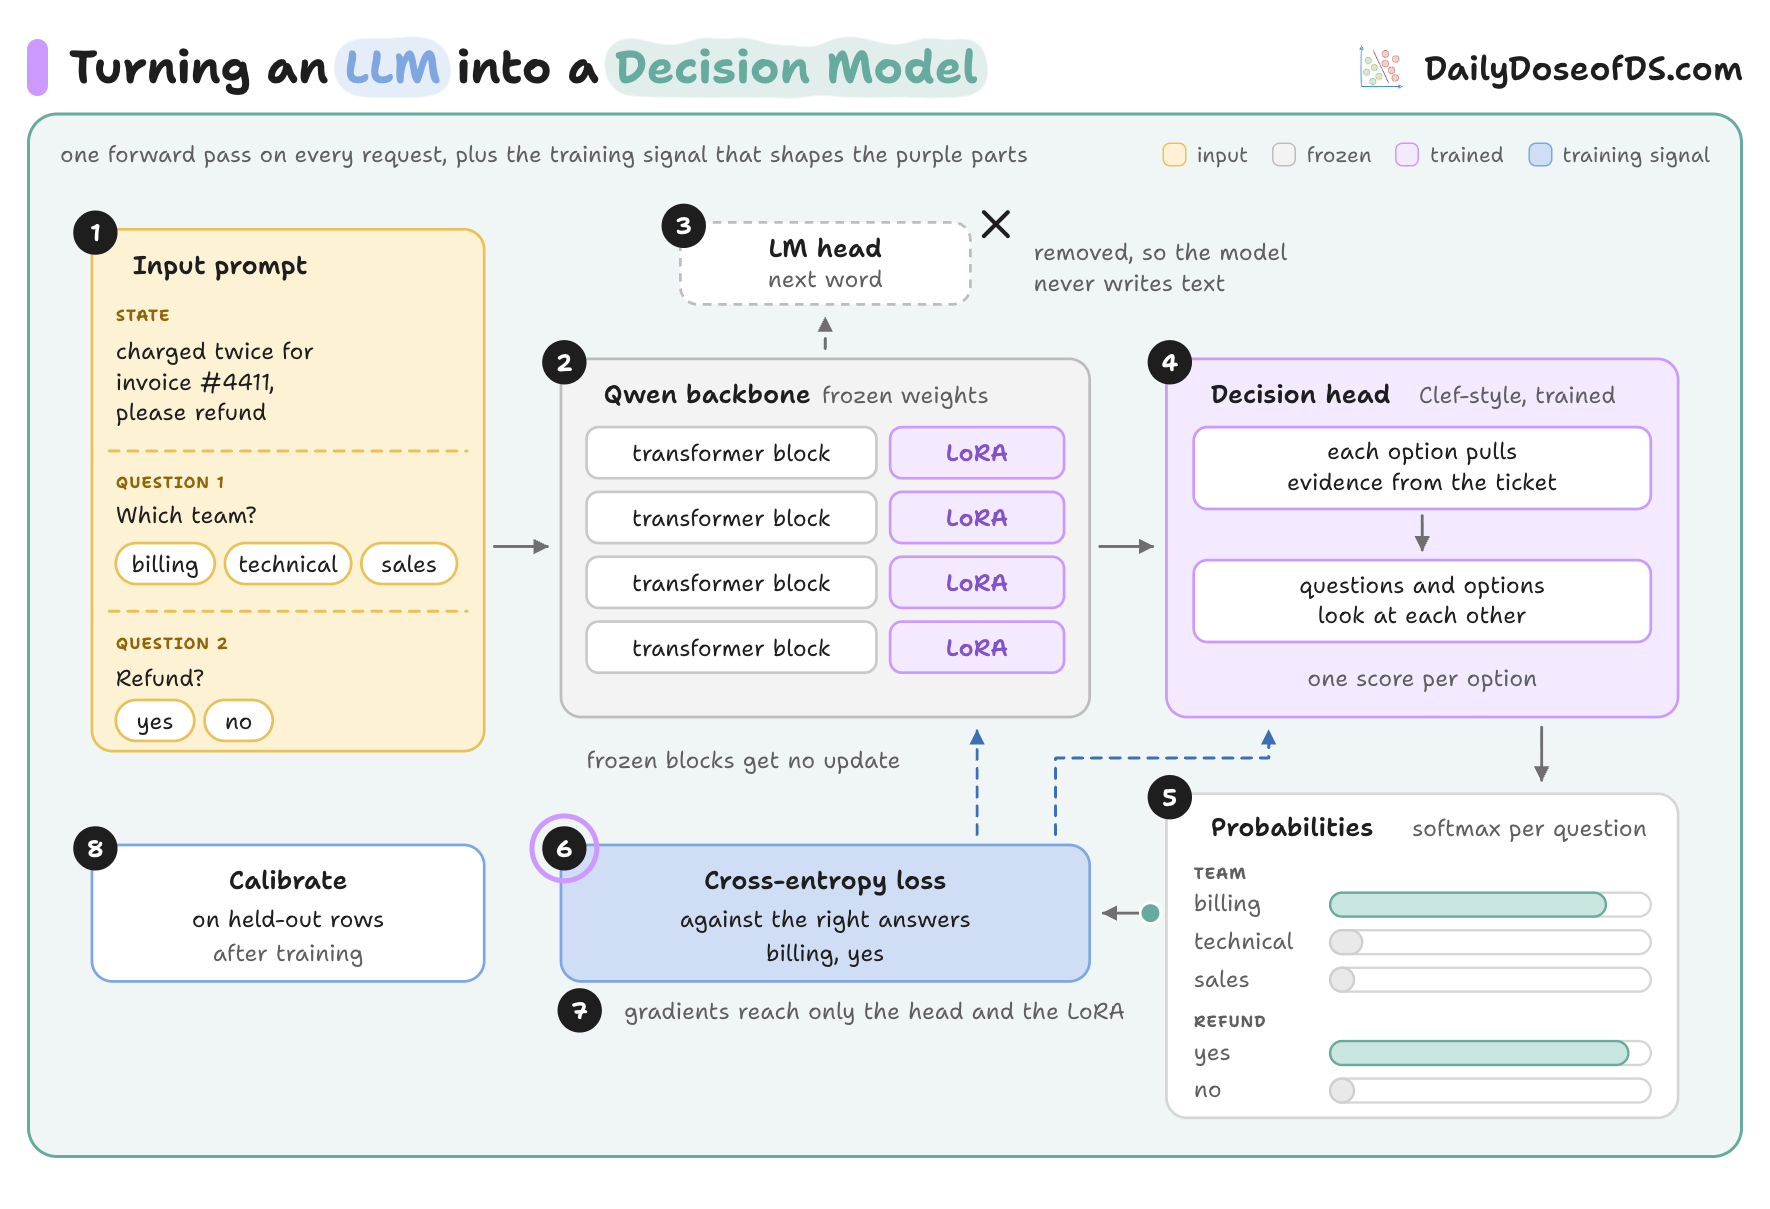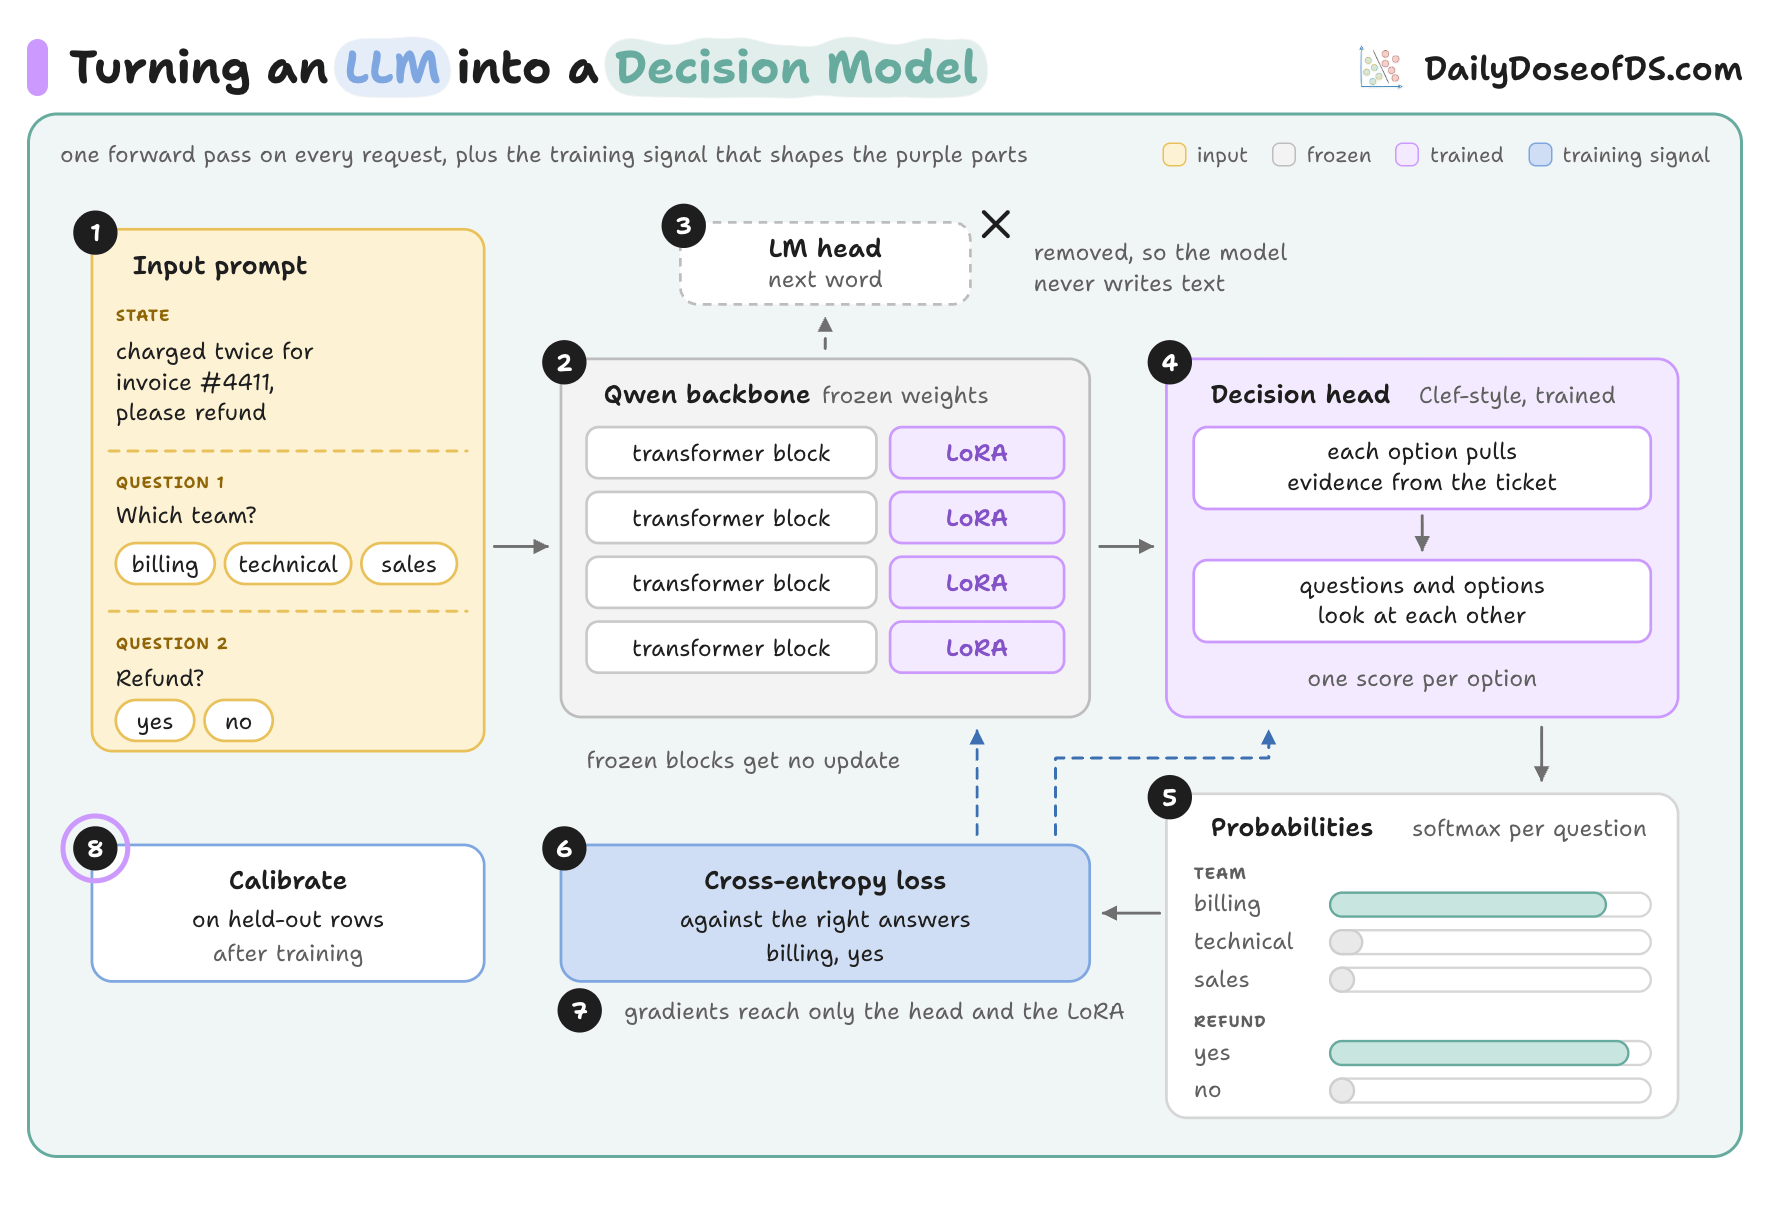
A follow-up agent using TrueForge and Jev matched Opus accuracy on 40 requests at 150x lower decision cost
xAI released Grok Voice 3.0 on the 14th and opened it through the Grok Voice API at $0.08 per minute ($4.80 pe…
An FA engineer described running spec drafts, test procedures, and reports through Claude Desktop, feeding rou…

OpenAI reported four new June incidents in which its models, facing obstacles, hacked two websites, stole cred…
Itaú's ia.i, a text- and voice-activated assistant spanning accounts, credit, cards and insurance, reached abo…