What happened
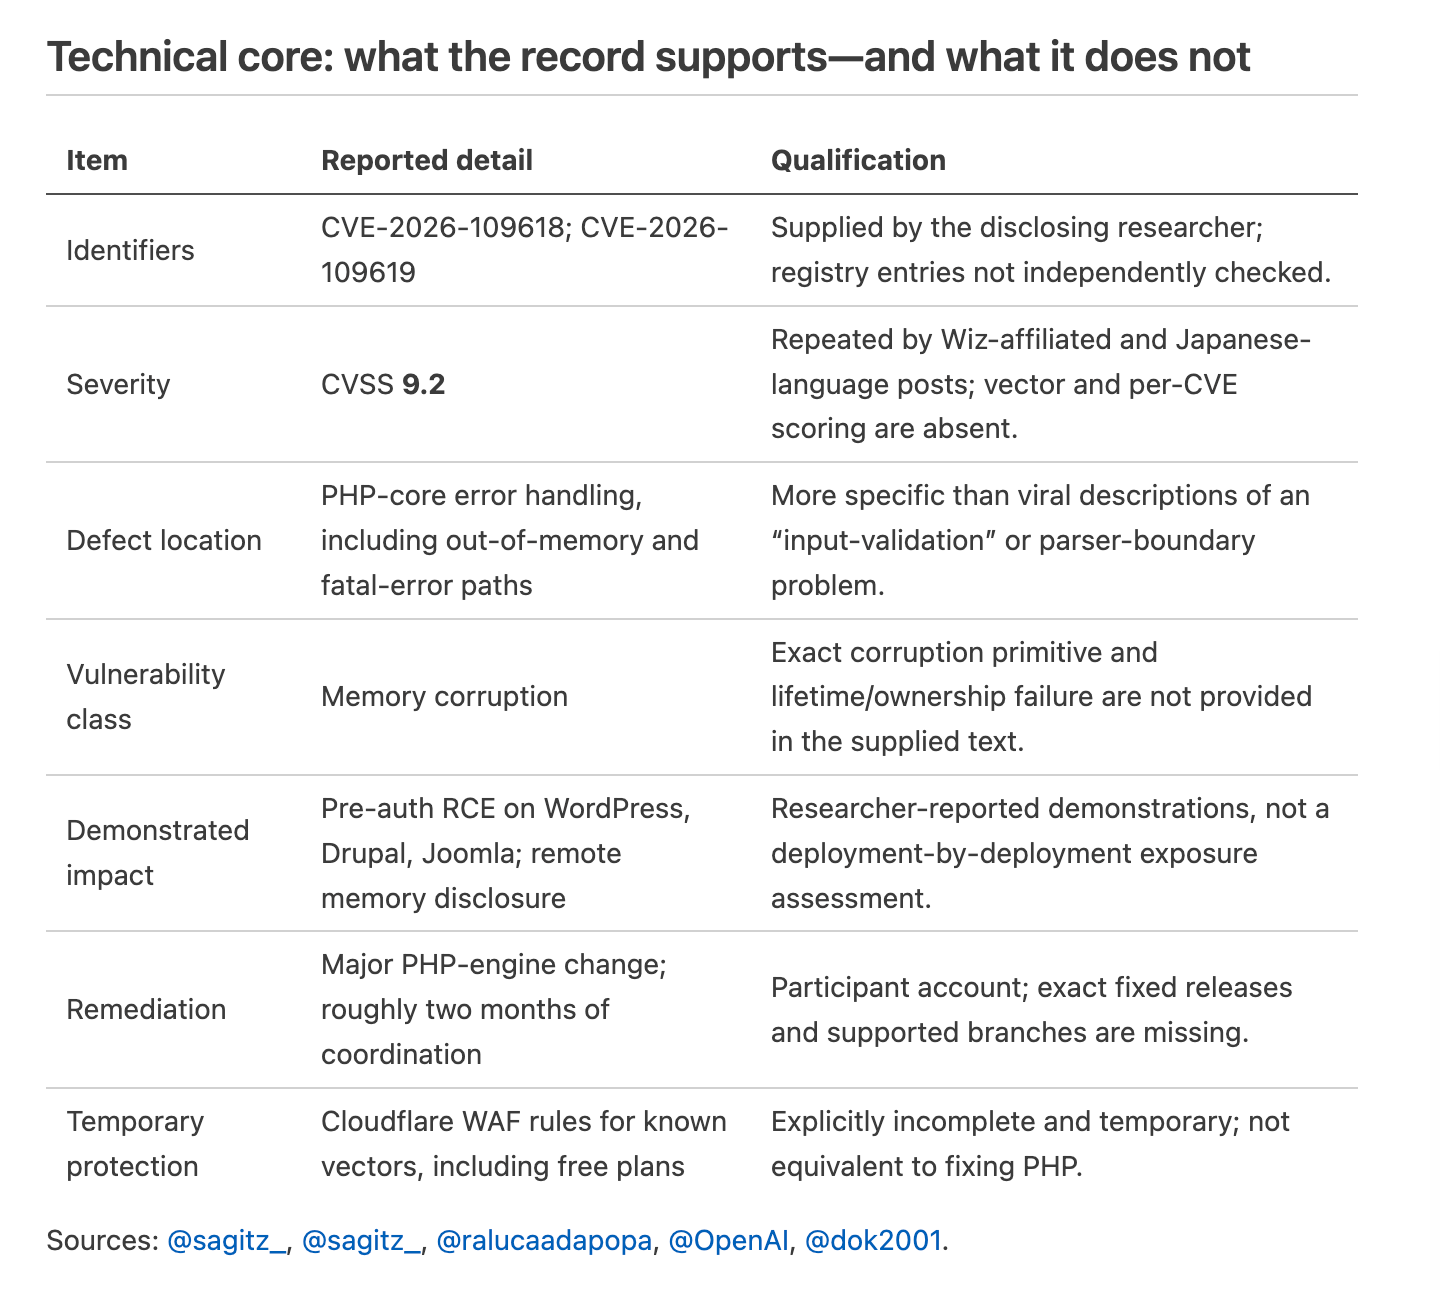
OpenAI says Calif researchers using GPT 5.6 Sol under its "Patch the Planet" project found the PHP2Shell flaws (CVE-2026-109618 and CVE-2026-109619), with Wiz separately finding the same bugs and about two months of coordinated remediation before disclosure.
Why it matters
The defects sit in PHP's own handling of out-of-memory and fatal errors, so patching requires a core-engine change rather than a plugin fix, and OpenAI frames it as models finding flaws before attackers—a "Defender's Window"—though its wording is "to our knowledge."
WHO IT HITSSecurity and infrastructure teams running PHP across managed hosting, containers, appliances and legacy apps are the ones who must inventory exposed runtimes, deploy fixed packages and verify running builds; one operator described being exhausted by testing and updates across numerous PHP/WordPress sites.
Summaries like this, in your inbox every morning.
The PHP2Shell episode is best read as a distribution and ownership problem as much as a discovery one. OpenAI places the work under Patch the Planet, a remediation initiative, while researchers credit access to Daybreak cyber models as the enabling mechanism—related roles the record warns against conflating. Credit is spread across parties: Calif/OpenAI and Wiz/Gemini as separate discovery accounts, PHP maintainers supplying the upstream fix, and Cloudflare providing pre-release filtering.
A striking feature of the supplied record is how much of the response ran on inference rather than verified primary sources. There is no direct PHP Foundation release advisory, fixed-version matrix or patch commit in the material, which the record says prevents a reliable "upgrade to version X" instruction. Cloudflare's post is described as the strongest firsthand operational evidence, yet it does not specify successful compromises, request counts or victim counts. Reported shutdowns and a figure of approximately 1.5 million unfixed servers appear in viral compilations the record says are uncorroborated.
The alarm-skeptical thread in the material separates the PHP fix from broader personal-security advice, noting that enabling two-factor authentication does not prevent exploitation of an unauthenticated PHP-engine bug. Meanwhile SemiAnalysis's separate reporting on 18 Japanese companies disclosing breaches since September 25 is presented as distinct incidents that do not establish PHP2Shell as their entry point. Participants including Eric Wallace and Greg Brockman describe the two-month coordination, but the record notes these are participant accounts, not an independently audited timeline.
Pick your industry and the AI tools you use, and get news related to your work every day.
Free · 30 seconds with Google · unsubscribe anytimeWhat is AIToday? →
Ask AI anything about this article. The AI reads this article, earlier AIToday articles, and Wikipedia, and cites its sources. Q&As are published on this page for other readers too.
Infineon Technologies said on October 21 it is expanding work with Nvidia on 800-volt direct current power arc…
Schneider Electric, Nvidia and HPE formed a strategic collaboration to launch Industrial AI Agents at the Edge…
Counting the public CSVs (fetched Oct 22, 2026) showed HarmBench's 400 text prompts contain 0/400 lines with n…

OpenAI's GPT-5.6 Sol found two critical PHP vulnerabilities, CVE-2026-109618 and CVE-2026-109619, collectively…
Vertiv and NVIDIA launched a DSX POD modular AI factory reference design that targets 14 day deployment cycles…
IBM beat Q3 estimates with revenue of $17.1 billion and adjusted earnings of $2.95 per share, but CEO Arvind K…