What happened
Ben Zimmermann scanned 7.25 million public Gitee repositories and found 26,400 still-working credentials, including 9,473 Alibaba Cloud AccessKey pairs, 3,170 DeepSeek keys and 1,348 OpenAI keys; 12,242 came from 2025 commits.
Why it matters
The keys were tested against the services that issued them, and Zimmerman had confirmed no revocations when he published — so the exposure may still be live for the vendors and their customers.
WHO IT HITSEnterprise security teams and developers who have pushed code to public Gitee repositories are the most directly exposed, since any key ever committed there may still be usable against Alibaba Cloud, DeepSeek, Zhipu or OpenAI services.
Summaries like this, every morning.
The scale of the find comes from how the scan was run: rather than checking only current files, Zimmermann ran two open-source scanners across the full commit history of 7.25 million public repositories, which is how credentials that were deleted from view but never revoked could still surface. TruffleHog and Kingfisher each flagged different sets — 12,737 and 14,664 working credentials respectively — and the combined 26,400 were confirmed to still work against the issuing services.
The timing is notable. By commit date, 12,242 of the credentials came from 2025, nearly half the total, which suggests the practice of committing keys to public repos is ongoing rather than a legacy problem. Zimmermann also found an active organization-admin credential for a major enterprise AI platform, which he left unnamed.
The disclosure gap is the part that matters for anyone using these services. Vendors with the most exposed keys received a list of their credentials, but the developers who leaked them were not contacted, and no revocations had been confirmed at publication. Zimmermann's advice to developers is unqualified: treat any key that has ever been in a public Gitee repository as exposed, and revoke it at the provider.
Pick your industry and the AI tools you use, and get news related to your work every day.
Free · 30 seconds with Google · unsubscribe anytimeWhat is AIToday? →
Ask AI anything about this article. The AI reads this article, earlier AIToday articles, and Wikipedia, and cites its sources. Q&As are published on this page for other readers too.
Japan AI Development Center announced a Claude Code seminar for December 9, 2026, 14:00–16:00, at the Higashih…

株式会社Ikigai said on 2026年10月30日 it will start a service covering ChatGPT ads, SEO and LLMO together, promising…
MediaTek reported third-quarter 2026 revenue of NT$168.06 billion (US$5.17 billion), up 10.4% quarter-over-qua…
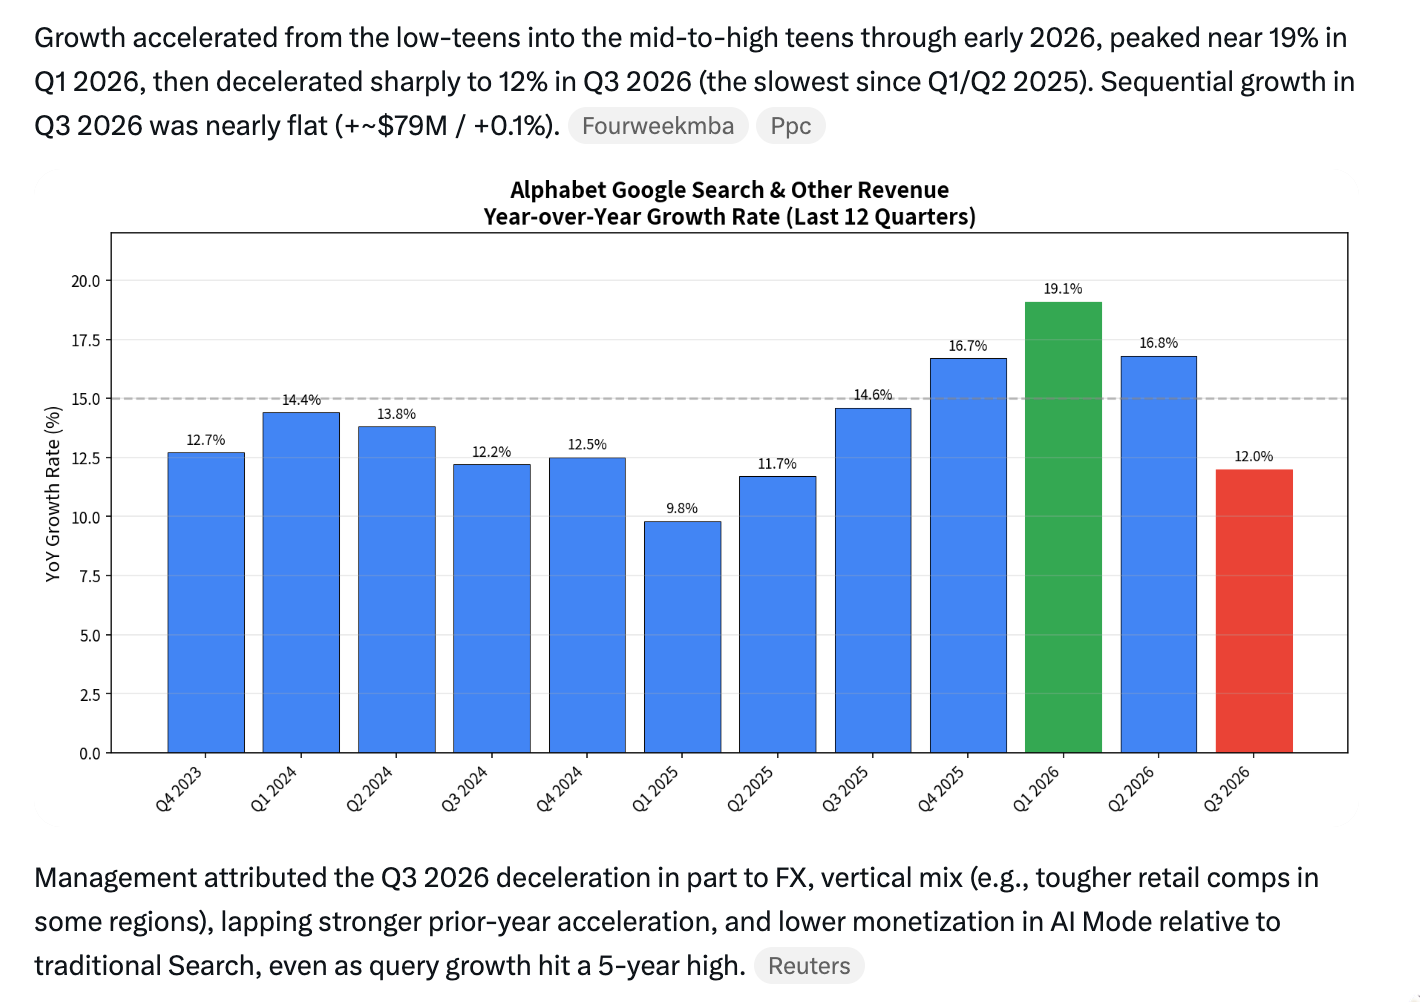
Google Chief Business Officer Philipp Schindler said the strong growth in AI Mode queries had an impact becaus…
Baidu open-sourced Unlimited-OCR-2, a 3B vision-language OCR model, and a developer's lumichy-unlimited-OCR wo…
Reddit shares fell 29.22% Friday, the worst day since its 2024 IPO, after Q4 revenue guidance of $1.00 billion…