What happened
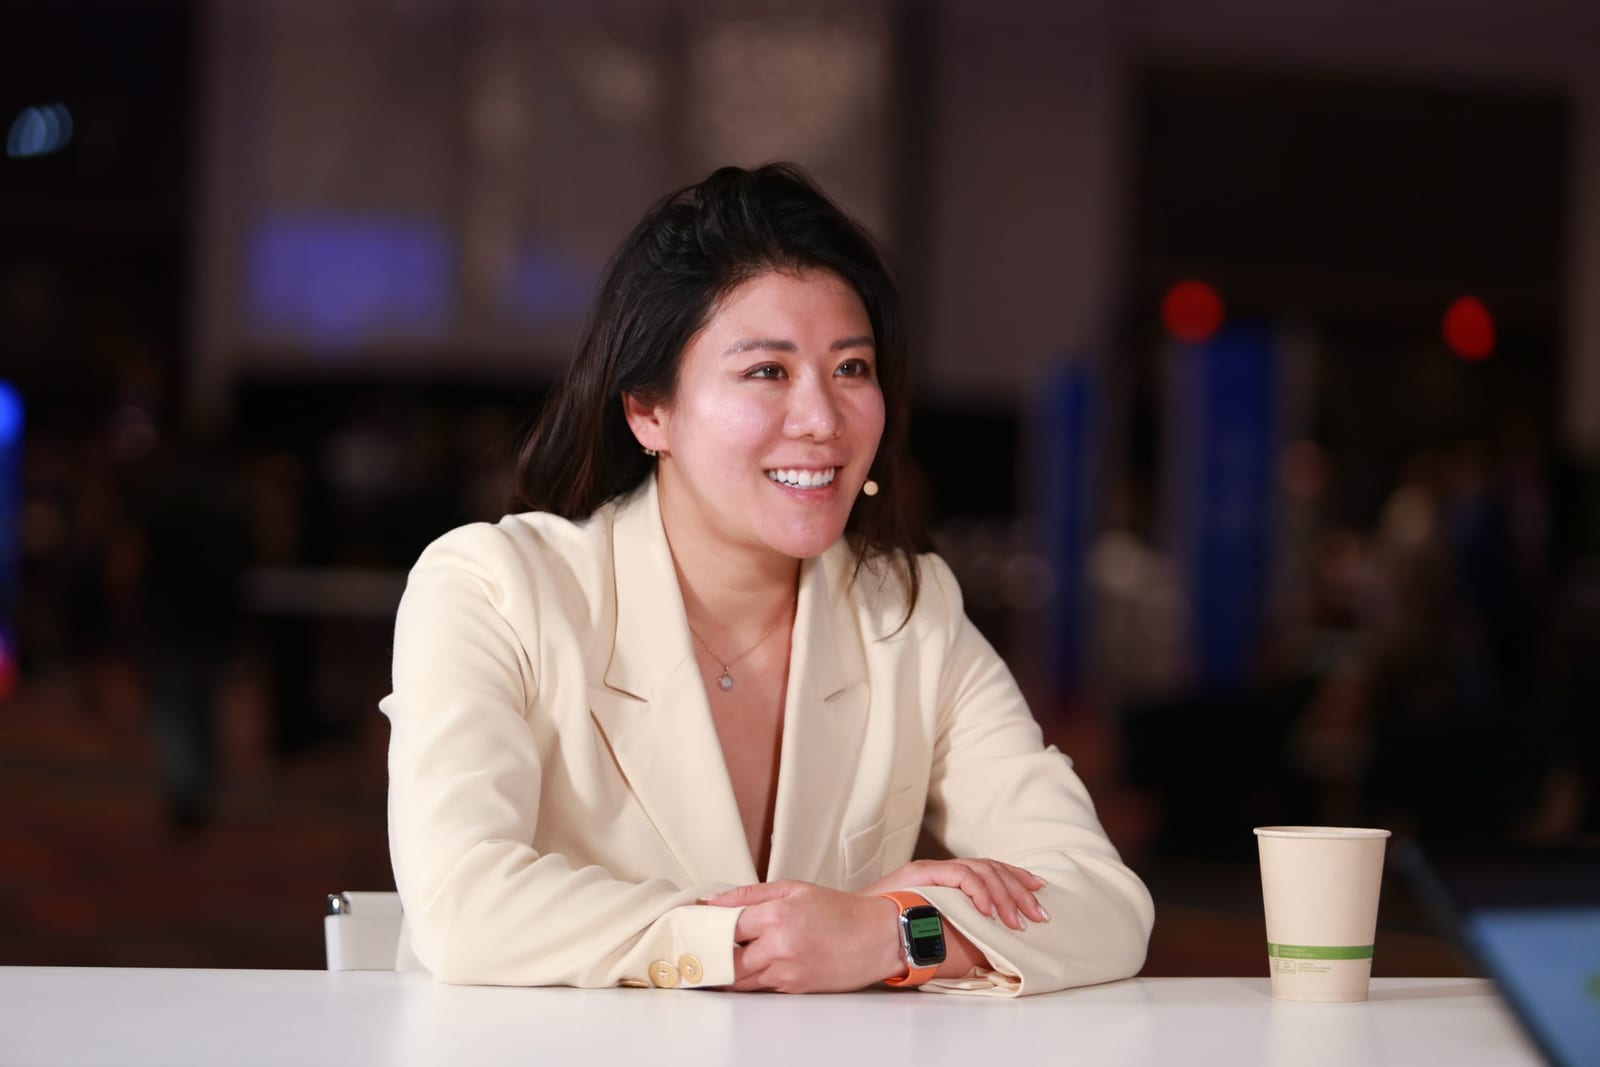
1Password CTO Nancy Wang said at Okta's Oktane event that agents need just-in-time, task-based access, and the company recently turned that into a task-scoped privileged access product.
Why it matters
Because an agent can show up in an audit log as the person it works for, security teams may struggle to attribute actions to software versus a human, according to Wang.
What to watch
1Password and Okta are backing shared identity standards so an agent's verified identity can carry across their systems; the test is whether that context travels between vendors.
WHO IT HITSSecurity and identity teams at companies deploying AI agents will need ways to attribute agent actions separately from the employees those agents act for, and to limit each agent to one task at a time.
Summaries like this, in your inbox every morning.
The problem 1Password is describing is not that agents are new, but that they blur a line identity systems were built around. An agent logs in, carries credentials and acts on someone's behalf, so it has characteristics of both a human and a machine. That overlap is what makes the audit trail ambiguous: an agent may appear as the person it works for even though software took the action. Nancy Wang's answer is to stop treating the agent as a fixed account and instead verify it task by task, the way you would check an intern's work before letting them move to the next project.
That thinking has already been packaged into a product. 1Password rejects standing privilege for humans, machines and agents alike, granting access just in time and checking why it is needed, and it recently turned that into a privileged access product scoped to a single task. The company's Credential Broker releases secrets only when needed, without exposing them to the agent or the underlying model.
The piece that is still in motion is portability. 1Password and Okta are backing shared identity standards so an agent's verified identity and authorization context can carry across their systems. For security teams, the practical question is whether that context survives the trip between vendors; if it does not, the distinction between who authorized an action and what performed it may remain hard to reconstruct.
For example, today's edition would include:
AI-summarized, only the topics you pick: one digest a day via Email, LINE, or Slack.
Free · 30 seconds with Google · unsubscribe anytimeWhat is AIToday? →
Ask AI anything about this article. The AI reads this article, earlier AIToday articles, and Wikipedia, and cites its sources. Q&As are published on this page for other readers too.
Bhakti Pitre, ServiceNow's VP of AI platform security product, said at Okta's Oktane event that agent "kill sw…
Futurum's report, sponsored by QumulusAI Inc., finds agentic AI can drive token consumption per task 10 to 100…
Claude Code's creator Boris Cherny answered a developer's question on September 11, 2026, saying throwaway pro…
ITR principal analyst Hiroaki Koumoto said Japanese firms' efforts in harness engineering are 'almost nonexist…
Stagwell CEO Mark Penn told Power Players most digital ads "are not very good" and said AI's payoff is doing t…
AMD agreed to an $8.2 billion all-stock buyout of World Labs, the San Francisco startup led by Dr