What happened
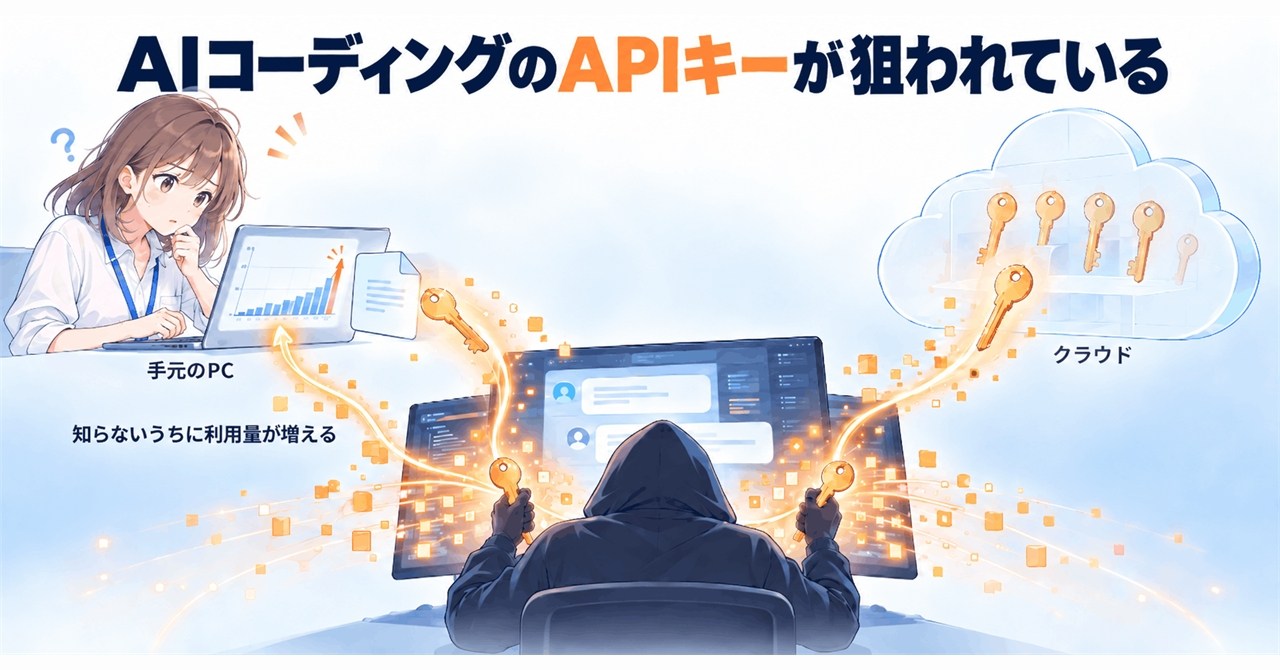
On Oct 15, Symantec (Broadcom) said a new version of info-stealer "Aoki" steals credentials for Claude, OpenAI Codex, Cursor, Gemini and others; on Oct 17, OpenCode said old-system access exposed stored API keys.
Why it matters
Stolen keys let third parties run AI on the victim's account, so the victim may foot the bill — a risk that applies whether keys sit on a developer's PC or in a cloud workspace, though the two incidents have different causes.
Summaries like this, in your inbox every morning.
The two incidents landed in the same week but differ in mechanism. Aoki is an info-stealer that runs on an infected PC and collects stored credentials and session files; Symantec's Threat Hunter Team said the malware, first confirmed in 2026, added AI coding tool targets in recent samples. OpenCode's problem was on the cloud side: the operator said an old system being retired was accessed without authorization between the night of Oct 16 and Oct 17, and it notified affected users by email on the morning of Oct 17 (US time).
What ties them together is what a leaked key enables. An attacker can use the victim's account, run up usage the victim pays for, or resell the credentials. OpenCode described the breach as related to a "large-scale distillation attack" — using one model's outputs to train another — though it said the actual use of the leaked keys and whether individual billing reports connect to that attack need to be checked separately.
Symantec's report does not say how many victims there were or how stolen AI credentials were actually misused, and OpenCode's stated scope is distinct from users' reports of unexpected charges. The practical takeaway is to know where keys and tokens are stored, limit what each key can do, and be able to revoke one when something looks wrong.
Pick your industry and the AI tools you use, and get news related to your work every day.
Free · 30 seconds with Google · unsubscribe anytimeWhat is AIToday? →
Ask AI anything about this article. The AI reads this article, earlier AIToday articles, and Wikipedia, and cites its sources. Q&As are published on this page for other readers too.
Google released TorchTPU, a version of the PyTorch framework that lets developers run existing AI apps and mod…
Testing Pi 0.84.2 with claude-sonnet-4-5, a hook returning { block: true, reason } on rm produced a normal too…

A Zenn author migrating a ten-year-old PHP/Laravel monolith — hundreds of endpoints and more than 600 shared m…
After six rounds of tuning TypeSafe AI's Jev for note selection, the author benchmarked it on 100 requests aga…
OpenAI said GPT-6 Astra passed 87.39% and GPT-6.1 Sol 87.04% of its MultiLangBench test — building a SQLite-co…
Anthropic is floating a draft bill that blocks an AI model's release only when independent evaluators find a f…