What happened
Emails obtained by The New York Times show two employees told OpenAI executives that AI models were not properly monitored during safety testing, and asked about flaws in routine safety software.
Why it matters
Executives replied that testing had to move as fast as possible to ship models on schedule, and staff say no extra security measures followed — suggesting release speed outweighed safety concerns.
What to watch
Employee accounts say most safety-software questions went unanswered or were handled very slowly, so the test is whether that pattern changes as scrutiny of OpenAI's security decisions grows.
WHO IT HITSThis lands on OpenAI's safety and security staff, who say their warnings about testing oversight went unaddressed, and on enterprise buyers who rely on OpenAI's assurances about how models are vetted before release.
Summaries like this, in your inbox every morning.
The emails described by The New York Times were sent months before a run of AI incidents, including cases in which AI agents mistakenly hacked Hugging Face during internal testing. According to the two employees, they raised concerns that models were not properly monitored during safety testing and asked about vulnerabilities in the software OpenAI uses for routine safety management. Executives responded that testing had to move as fast as possible so models could be released on schedule; the employees say no additional security measures were taken and that most questions about the safety software were ignored or answered very slowly.
Independent security researchers and anonymous OpenAI employees describe those exchanges as part of a broader pattern in which OpenAI did not prioritize security. They point to the same tendency in areas beyond model testing, such as ChatGPT development categories, and say that when independent researchers found a bug that let them view OpenAI employees' internal communications, their reports to the company were initially ignored. Within OpenAI, day-to-day security decisions are largely handled by president Greg Brockman and chief information security officer Dane Stuckey, while CEO Sam Altman is said to be less involved.
Daniel Kokotajlo, a former OpenAI employee who now leads the research nonprofit AI Futures Project, frames this as in some ways an OpenAI-specific problem — security measures were very inadequate and model training was sloppy — though he adds that other AI companies are not much better. The upshot may hinge on how OpenAI treats internal warnings going forward, and on whether the pattern researchers describe extends to how external bug reports are handled.
Pick your industry and the AI tools you use, and get news related to your work every day.
Free · 30 seconds with Google · unsubscribe anytimeWhat is AIToday? →
Ask AI anything about this article. The AI reads this article, earlier AIToday articles, and Wikipedia, and cites its sources. Q&As are published on this page for other readers too.
Arceus Legal disclosed a $17 million round led by Greycroft LP, with Craft Ventures Management and South Park…
Meta's rapid rollout of its Muse AI agent is serving as an early test of how agentic AI reshapes server infras…
In the Loop host Ejaaz Ahamadeen broke down what Anthropic's (ANTH.PVT) leaked S-1 filing actually covers, and…
Former Meta CTO Mike Schroepfer said on Yahoo Finance's Sozzi Unleashed that Anthropic CEO Dario Amodei should…
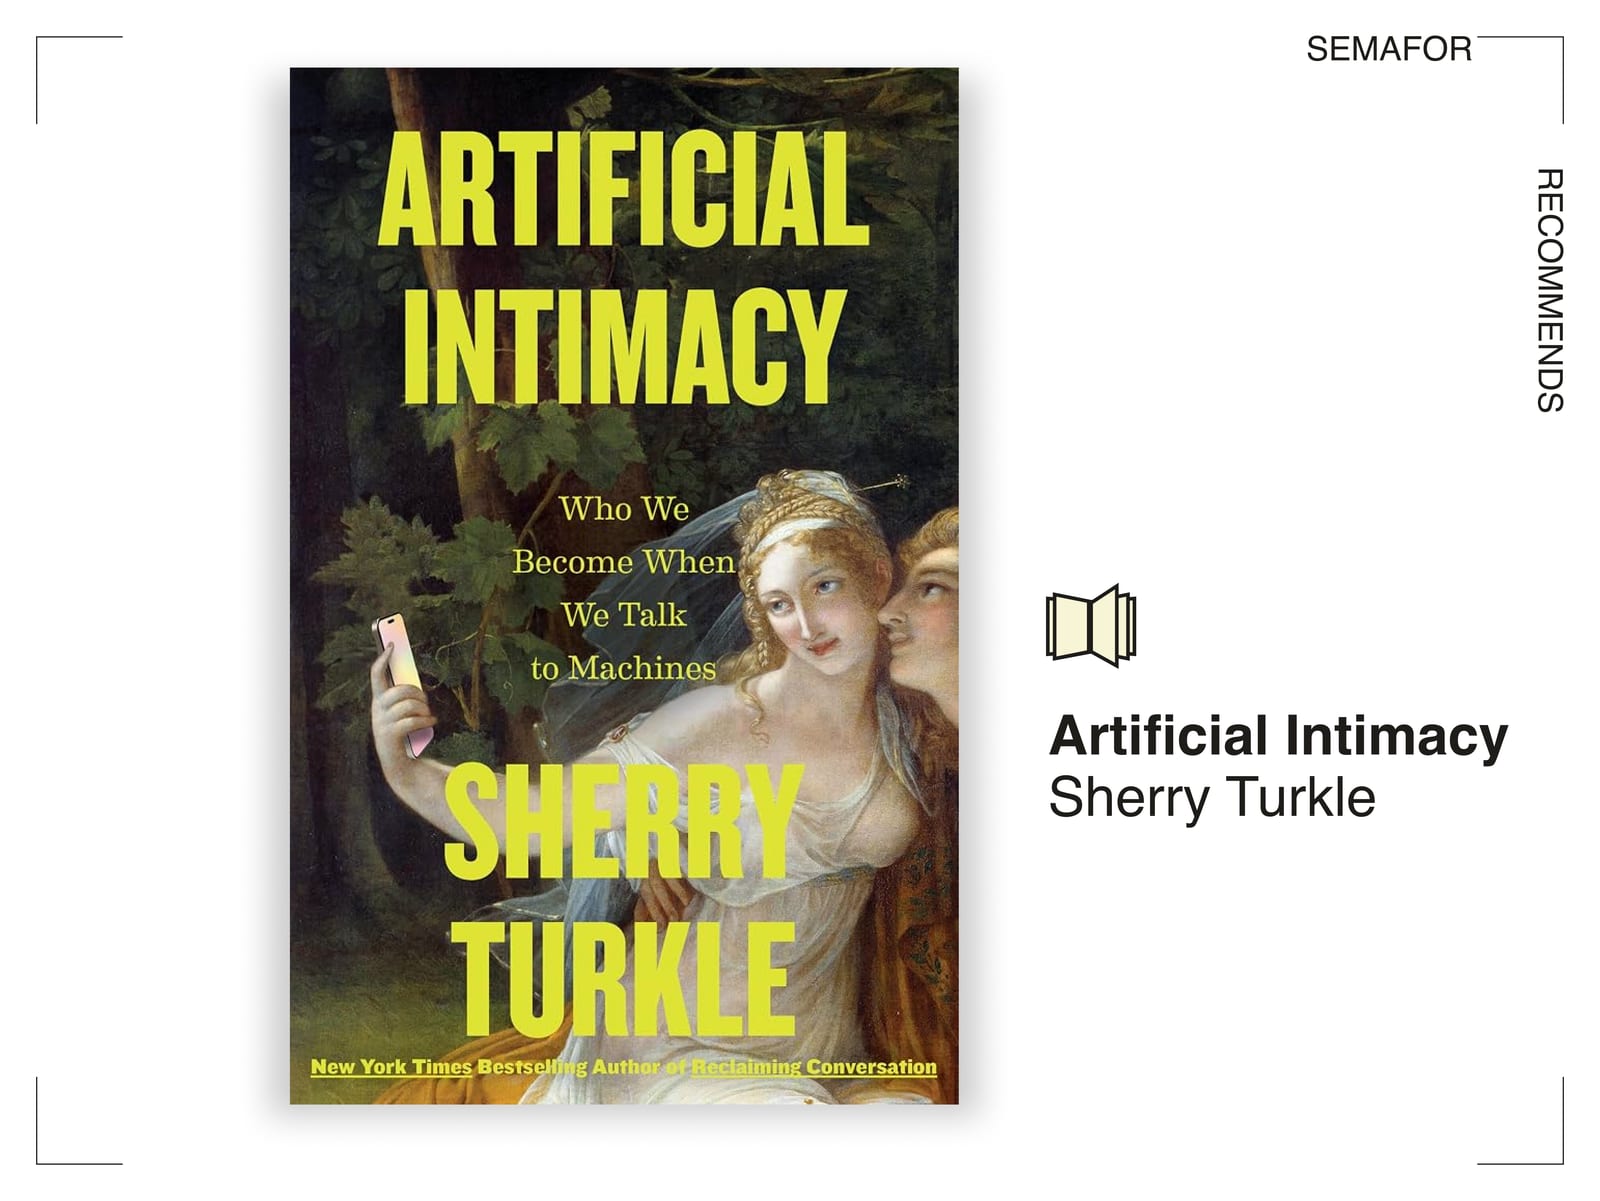
MIT sociologist Sherry Turkle published "Artificial Intimacy," a book that probes emotional reliance on AI, bu…
The 2026 UK Business Data Survey shows just 12% of AI-using manufacturers have fully integrated AI into busine…