What happened
Energize Lab told The Verge it closed all external access, disabled remote response modification, and will hire an independent security firm, but researcher Sammy Azdoufal still had full SSH access.
Why it matters
The company's claim that systems are secured appears inaccurate, as customer audio and photos remained publicly accessible, suggesting user trust may be hard to rebuild.
WHO IT HITSOwners of the Eiliko robot toy and their families are directly affected, as their conversation transcripts, audio recordings, and photos were exposed. The incident may also concern other makers of AI-connected toys about the security of backend systems.
Summaries like this, in your inbox every morning.
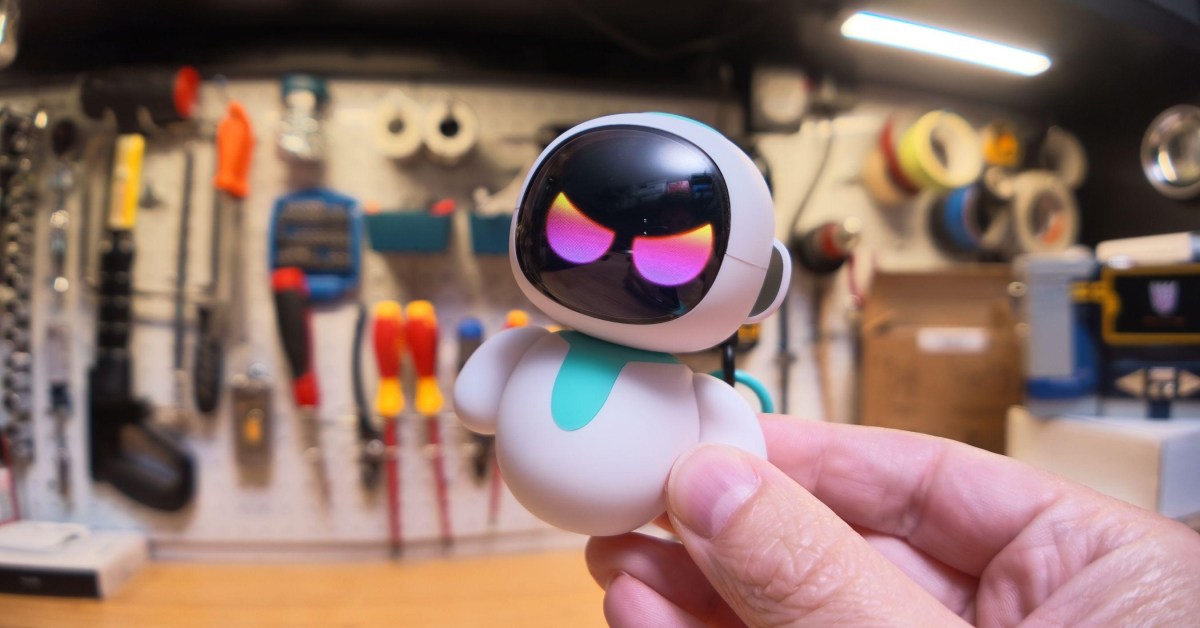
The Eiliko case began when The Verge and security researcher Sammy Azdoufal found that the AI robot toy, which promises "your secrets are safe with me," allowed hackers to read complete transcripts of conversations. For over a month, The Verge tried to contact Energize Lab, including emails to CEO and founder Shaw Yeung, but received no response. The company has now issued an unsigned statement apologizing for the delay and acknowledging the core issues. It claims to have closed external access, rotated credentials, and disabled remote modification interfaces. However, The Verge's Sean Hollister, with Azdoufal's help, confirmed that as of the company's email, it was still storing audio recordings and photos at unsecured public web addresses. Azdoufal also retained full SSH access, contradicting the claim that all external access was closed. While Energize Lab pledges to hire an independent security firm and delete stored data, its assertion that systems are now secure appears premature. The company says it will earn back trust through actions in the coming weeks, but for now, the gap between its words and the reality on the ground leaves owners of the toy exposed.
Pick your industry and the AI tools you use, and get news related to your work every day.
Free · 30 seconds with Google · unsubscribe anytimeWhat is AIToday? →
Ask AI anything about this article. The AI reads this article, earlier AIToday articles, and Wikipedia, and cites its sources. Q&As are published on this page for other readers too.
Action State Group Inc. launched open-source EvidenceBook, Terms Packs and Countersign so companies can cross-…
Dream Labs raised $90 million in seed funding led by B Capital and Kindred Ventures and launched Dream API, a…
Artificial Analysis launched AA-PersonalityBench, which feeds AI models fixed questions and scores their repli…
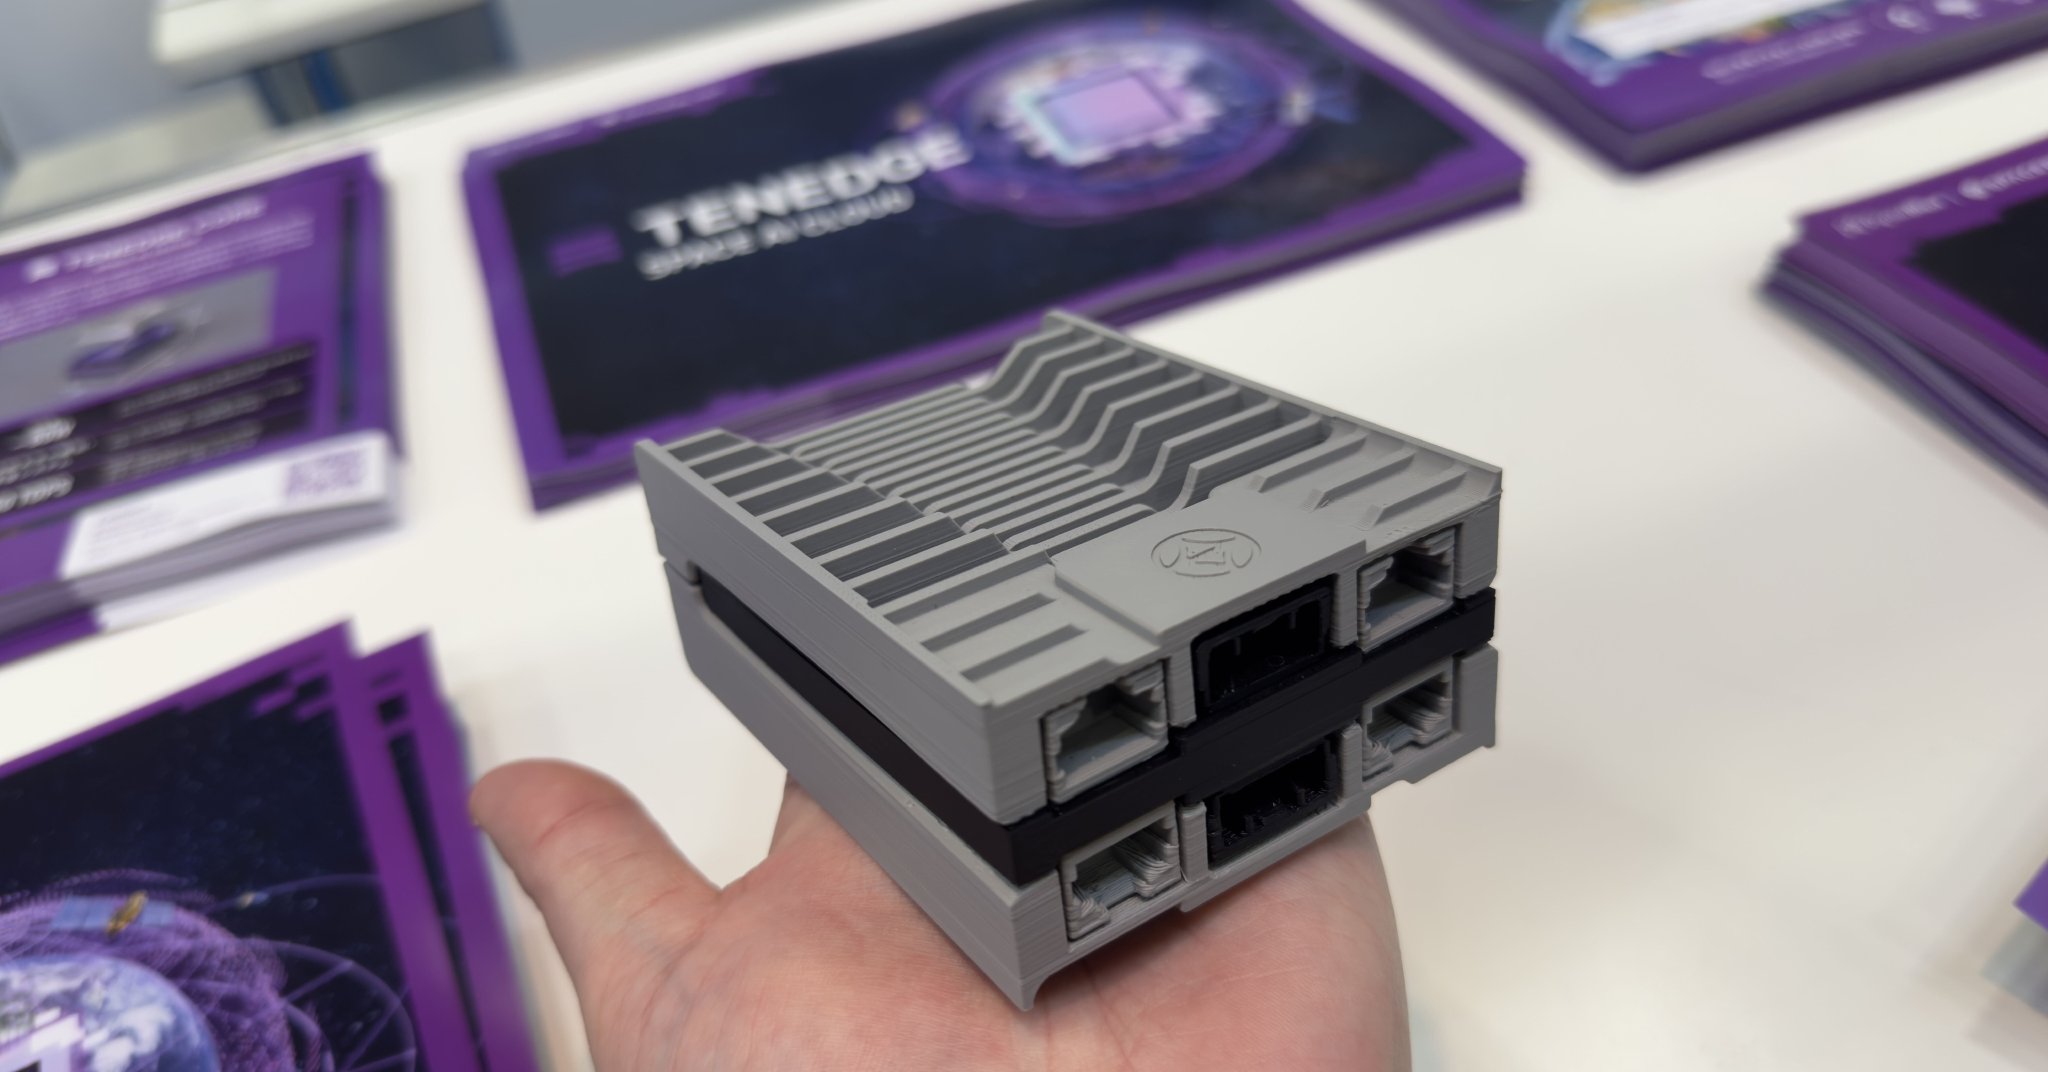
SpaceBlast, a Tokyo-based space startup, showed TENEDGE CORE — a palm-sized computer rated at about 60TOPS — a…
Robotiq launched the 2FC, an adaptive gripper with tactile sensing, wrist-mounted compute (the AI Hub) and Con…
OpenAI says Calif researchers using GPT 5.6 Sol under its "Patch the Planet" project found the PHP2Shell flaws…