
What happened
Ippu Senkin began offering Local AI Agent for Security, which runs on its Local AI Agent platform. Its IS Code engine uses a local LLM to cross-check configuration data against JVN, CVE and KEV, inspect exposure, and statically review source code.
Why it matters
Because the local LLM does not connect to the internet, configuration data and source code stay inside the customer's environment, addressing organizations that cannot hand such data to external services.
WHO IT HITSSmall information-security teams, especially at regional financial institutions and other organizations handling confidential data, may be able to automate the matching and draft-remediation work that has largely been manual.
Summaries like this, every morning.
The service builds on Ippu Senkin's on-premises AI agent platform, Local AI Agent, which the company says has been in production operation in closed environments such as regional financial institutions. The company also says it has completed technical verification of running a giant AI model with trillions of parameters entirely locally without external communication — though that track record belongs to the base platform, not to this new service.
The gap the company is targeting is not detection but follow-through. Public vulnerability information is updated daily, yet many organizations keep the matching work manual because handing configuration data or source code to an external service is itself a security risk. Even after a vulnerability is found, impact assessment, vendor requests, management reporting and budget approval tend to pile up on a small information-systems team.
Ippu Senkin's answer is to let AI handle reading and drafting inside the customer's environment, with security specialists acting as partners up to remediation. Whether that division of labor eases the burden on small teams is likely to be the point customers test first.
Pick your industry and the AI tools you use, and get news related to your work every day.
Free · 30 seconds with Google · unsubscribe anytimeWhat is AIToday? →
Ask AI anything about this article. The AI reads this article, earlier AIToday articles, and Wikipedia, and cites its sources. Q&As are published on this page for other readers too.
AI Hack completed support for Claude Haiku 5.5, Gemini 4 Argon and Gemini 3.5 Flash Lite in its AIO analysis t…
Cognition released Devin Security 2.0 on October 26, 2026, adding deep scans powered by frontier cyber models…
Yaraku will update "Yaraku Translation" to Ver.6.1 on November 1, adding an "AI Checker" that fixes number err…
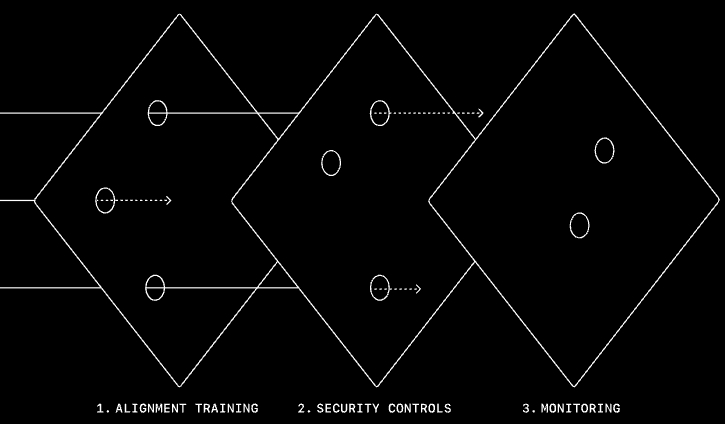
OpenAI expanded a four-layer monitoring system and said replaying the Hugging Face incident showed a warning c…
In AI Nexus's 80-question test, TypeSafe Jev hit 96.2% accuracy at 255.2 ms average latency, while GPT-5 score…
SBI損保 and Marubeni Information Systems will fully roll out MSYS Omnis across 80 seats at the contact center an…

