What happened
Cognition released Devin Security 2.0 on October 26, 2026, adding deep scans powered by frontier cyber models including Claude Mythos, intake of findings from tools like Snyk and Wiz, environment-based prioritization, and autonomous fix pull requests.
Why it matters
It gives enterprises a single workflow that turns a flood of vulnerability findings into prioritized, review-ready fixes, and Cognition is backing it with several hundred million dollars' worth of Devin credits, so security and development teams may face less backlog triage and more pull-request review.
WHO IT HITSEnterprise security teams and software developers stand to benefit: instead of triaging an ever-growing backlog of scanner alerts, they would review AI-generated fix pull requests and approve final risk decisions themselves.
Summaries like this, every morning.
Cognition frames Devin Security 2.0 as a response to a widening gap between attackers and defenders. The body notes that in October 2026, both PHP and Node.js projects disclosed remote code execution vulnerabilities affecting broad swaths of the web, and researchers using frontier models reportedly developed exploits that worked across multiple applications within hours. On the defense side, the volume of findings from AI and other tools keeps growing into a backlog that teams cannot clear. Finding more vulnerabilities alone does not reduce risk; the product's premise is that what matters is judging which findings are truly dangerous in a given environment and completing fixes quickly.
The product stitches together capabilities that enterprises often buy separately: threat modeling done with Cognition's technical team, deep scans using frontier cyber models like Claude Mythos without individual model contracts, ingestion and re-validation of findings from Snyk, Wiz, and bug bounty reports, and autonomous fixes by Devin that can process thousands of findings in parallel. Human review remains in the loop for both final risk decisions and merging fixes, and the recorded rationale is positioned for compliance documentation such as FedRAMP and PCI DSS. The free scan campaign through November 30, 2026, together with the several hundred million dollars in Devin credits, appears designed to pull enterprises into that workflow before they commit.
Pick your industry and the AI tools you use, and get news related to your work every day.
Free · 30 seconds with Google · unsubscribe anytimeWhat is AIToday? →
Ask AI anything about this article. The AI reads this article, earlier AIToday articles, and Wikipedia, and cites its sources. Q&As are published on this page for other readers too.
AI Hack completed support for Claude Haiku 5.5, Gemini 4 Argon and Gemini 3.5 Flash Lite in its AIO analysis t…
Ippu Senkin began offering Local AI Agent for Security, which runs on its Local AI Agent platform
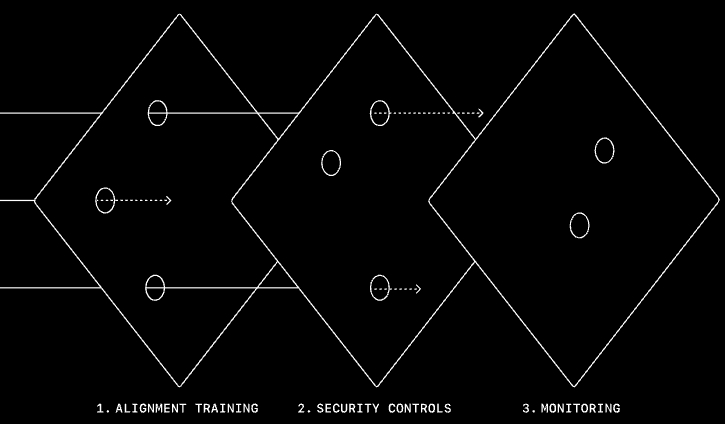
OpenAI expanded a four-layer monitoring system and said replaying the Hugging Face incident showed a warning c…
SBI損保 and Marubeni Information Systems will fully roll out MSYS Omnis across 80 seats at the contact center an…
monday.com's Ryan Nigro told theCUBE at the company's Elevate event that AI agents inherit employees' access…
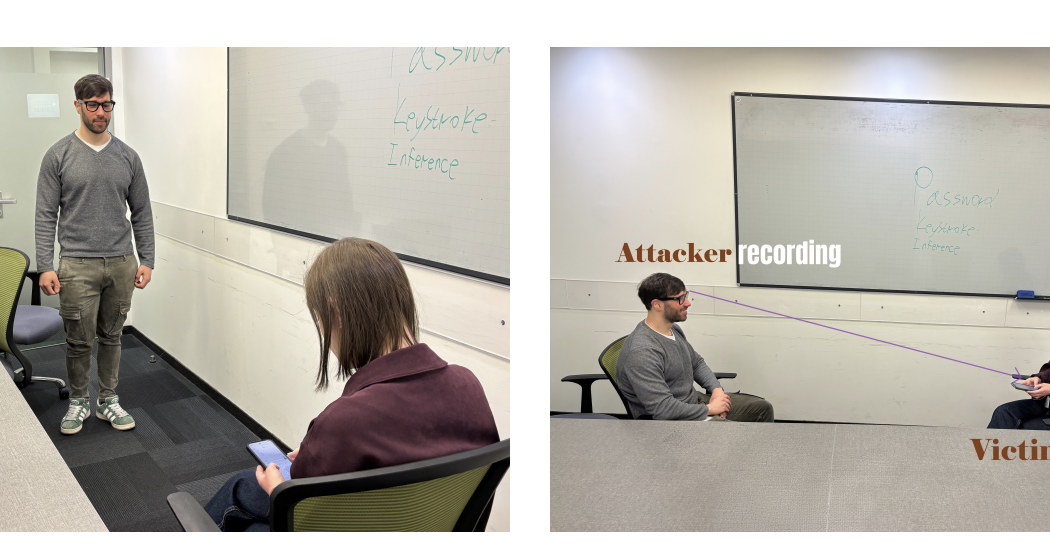
A Tel Aviv University paper, "Watch and Crack: Password Inference from Smart-Glasses Video," showed that foota…