What happened
Microsoft said Storm-0940, active since 2021, began using the open-source ARTEX framework around September to automate attacks on hundreds of organizations across aerospace, finance, government, semiconductors and other sectors.
Why it matters
Because ARTEX can run reconnaissance through data exfiltration with little human involvement and works with any AI model, the group can target many more organizations at once, Microsoft said.
WHO IT HITSSecurity teams at organizations that use or once used ConnectWise cloud backup apps with Microsoft 365 need to check sign-in and audit logs for unknown credentials or permission changes, following Microsoft's guidance.
Summaries like this, in your inbox every morning.
Storm-0940 has been active since 2021, targeting a wide range of industries to steal data, according to Microsoft. The group began using ARTEX around September, and the framework's language options include Japanese, Korean, Chinese and Spanish in addition to English.
The ConnectWise case shows how the group operates: it stole credentials for apps such as ConnectWise Cloud Backup and abused permissions already granted to those apps in customers' Microsoft 365 environments. Attackers attempted sign-ins to more than 2,250 tenants at a rate of 2,900 per minute, and in some environments they gathered information, added new credentials to apps and granted admin rights. Microsoft said its own systems and products were not exploited, and that signs of intrusion do not necessarily mean data was viewed or taken.
Separately, GMO Cybersecurity by Ierae said on October 19 that it confirmed ARTEX abuse in unauthorized access targeting Japanese companies, with about 20 targeted and eight disclosing breaches in September-October. Microsoft said ARTEX users operate in multiple regions and did not address any link between those attacks and Storm-0940.
Pick your industry and the AI tools you use, and get news related to your work every day.
Free · 30 seconds with Google · unsubscribe anytimeWhat is AIToday? →
Ask AI anything about this article. The AI reads this article, earlier AIToday articles, and Wikipedia, and cites its sources. Q&As are published on this page for other readers too.
The Agentic AI Foundation accepted four donated projects—OpenAI's Open Responses, Anthropic's Agent Skills, an…
In a contributed column, SCSK advisor Yoshihiko Murowaki cited Anthropic's April 2026 disclosure that its unre…
CoreWeave unveiled its Zero Trust AI Framework at Nvidia GTC, built around customer-controlled model, data and…
Cybersecurity firms found thousands of AI-generated websites posing as local US news sites, written not for vo…
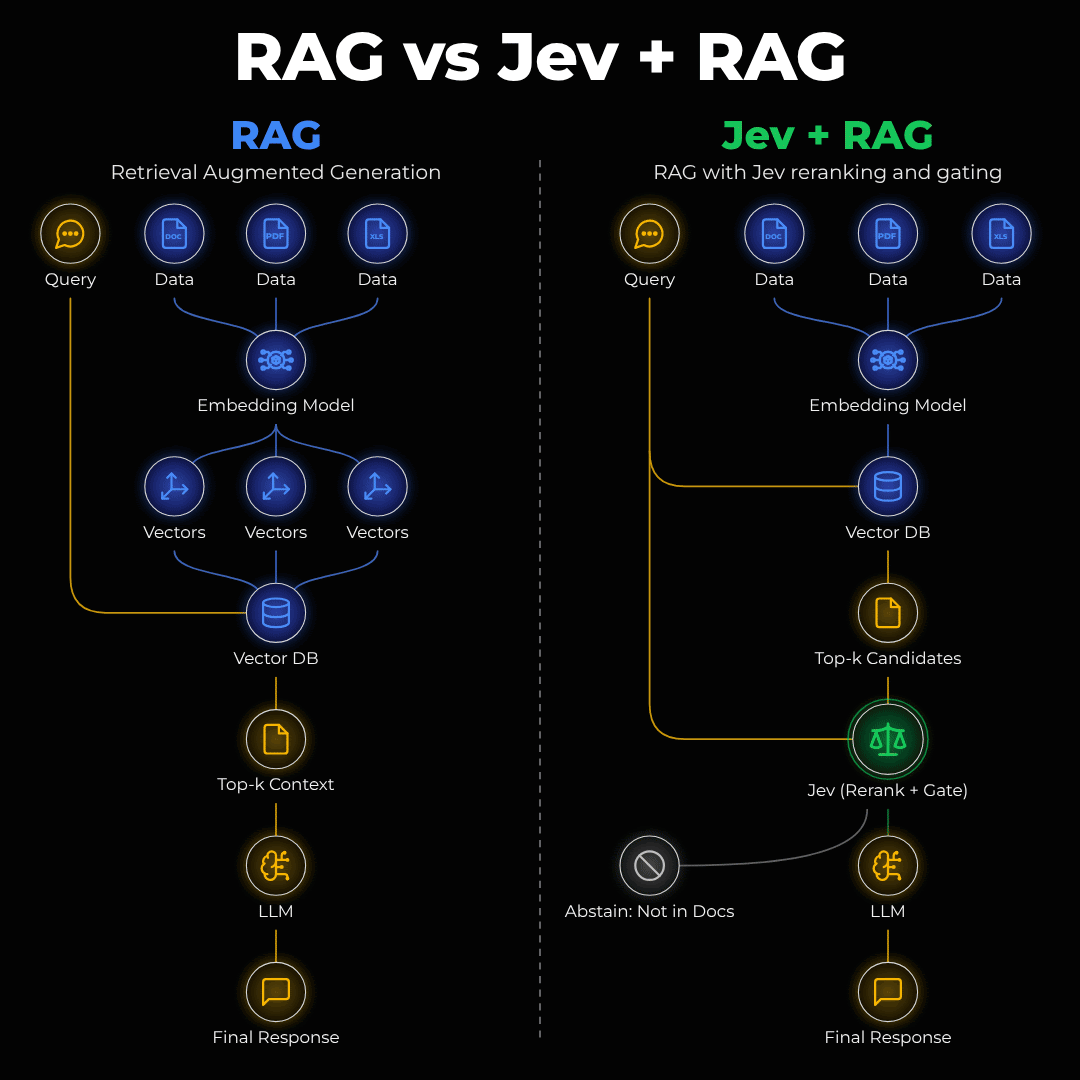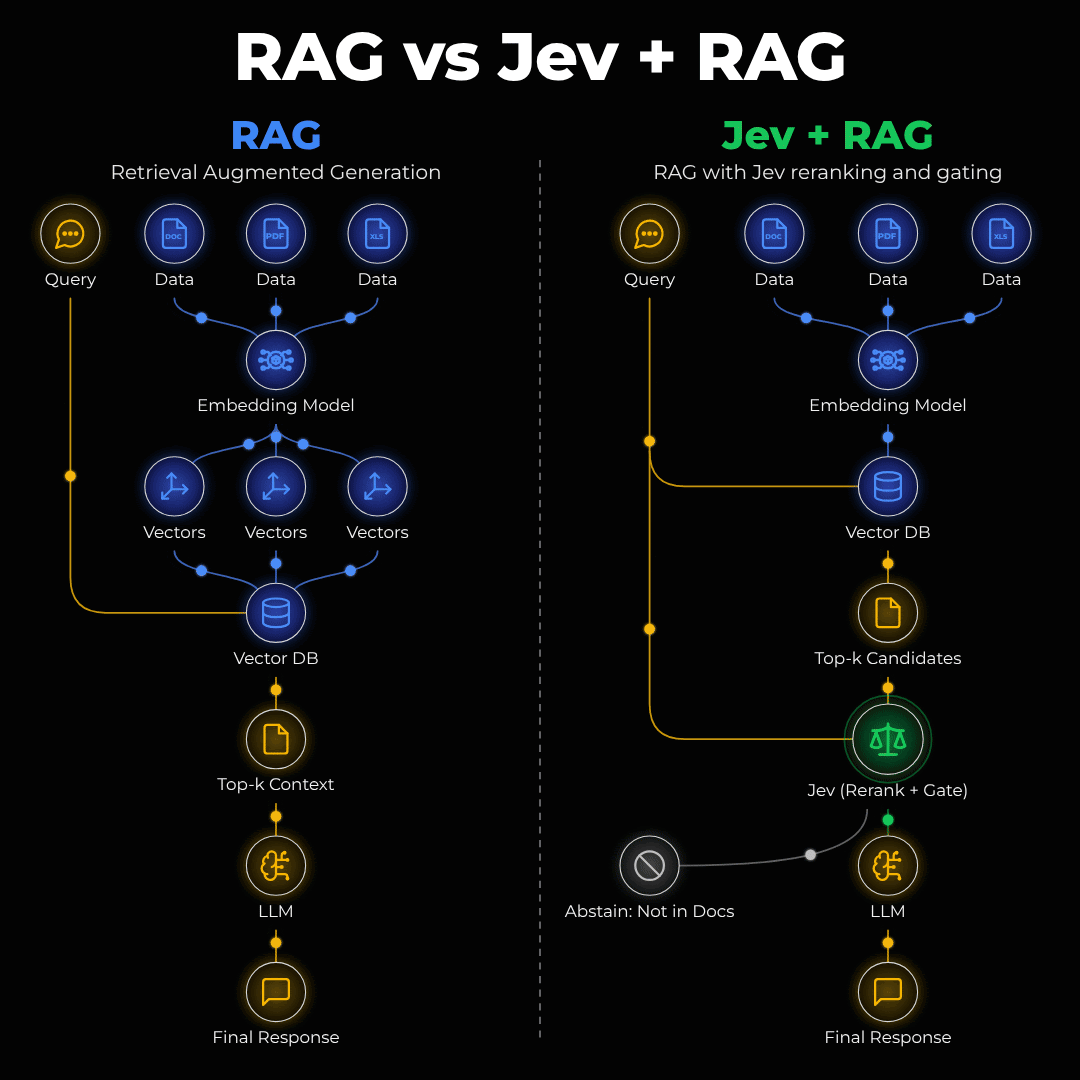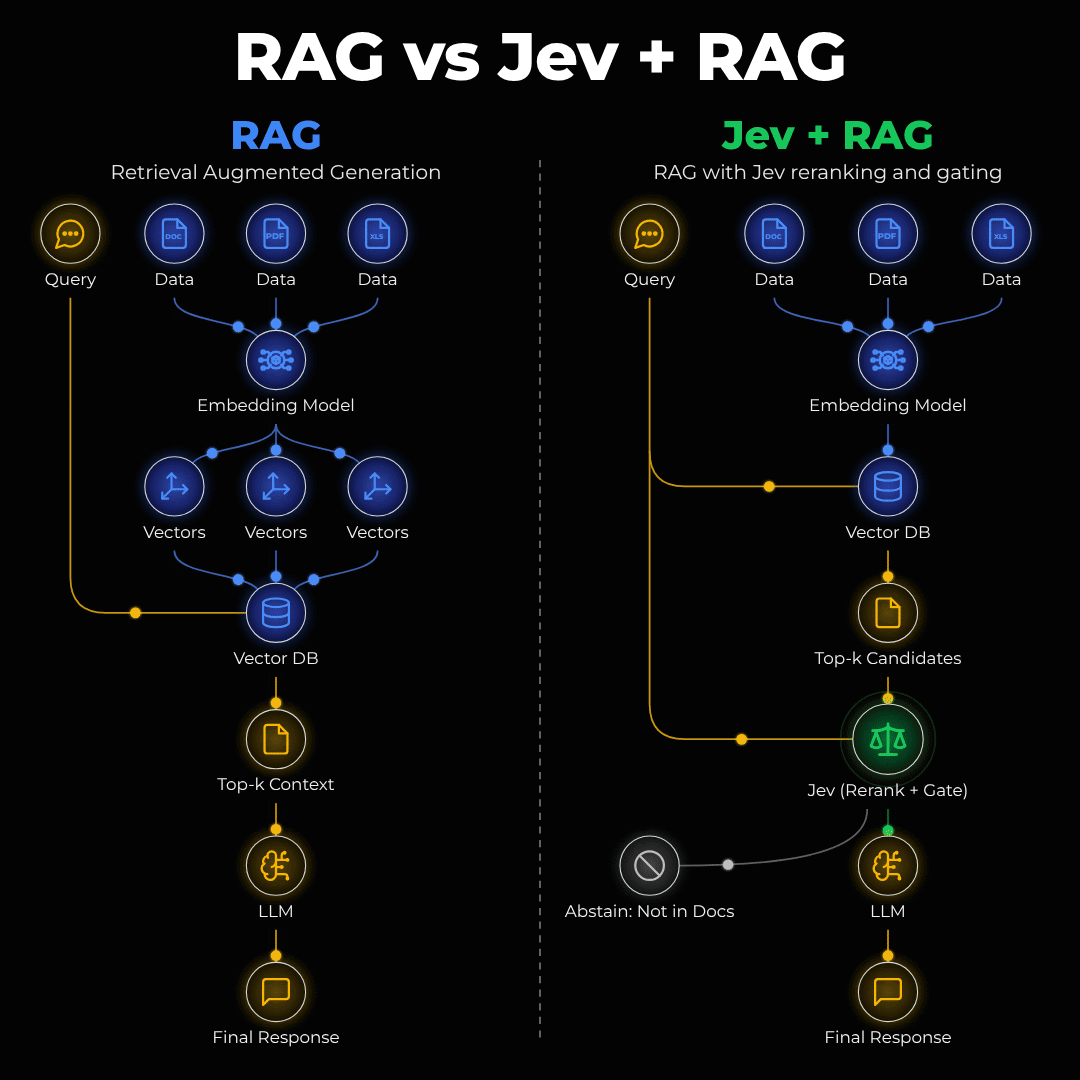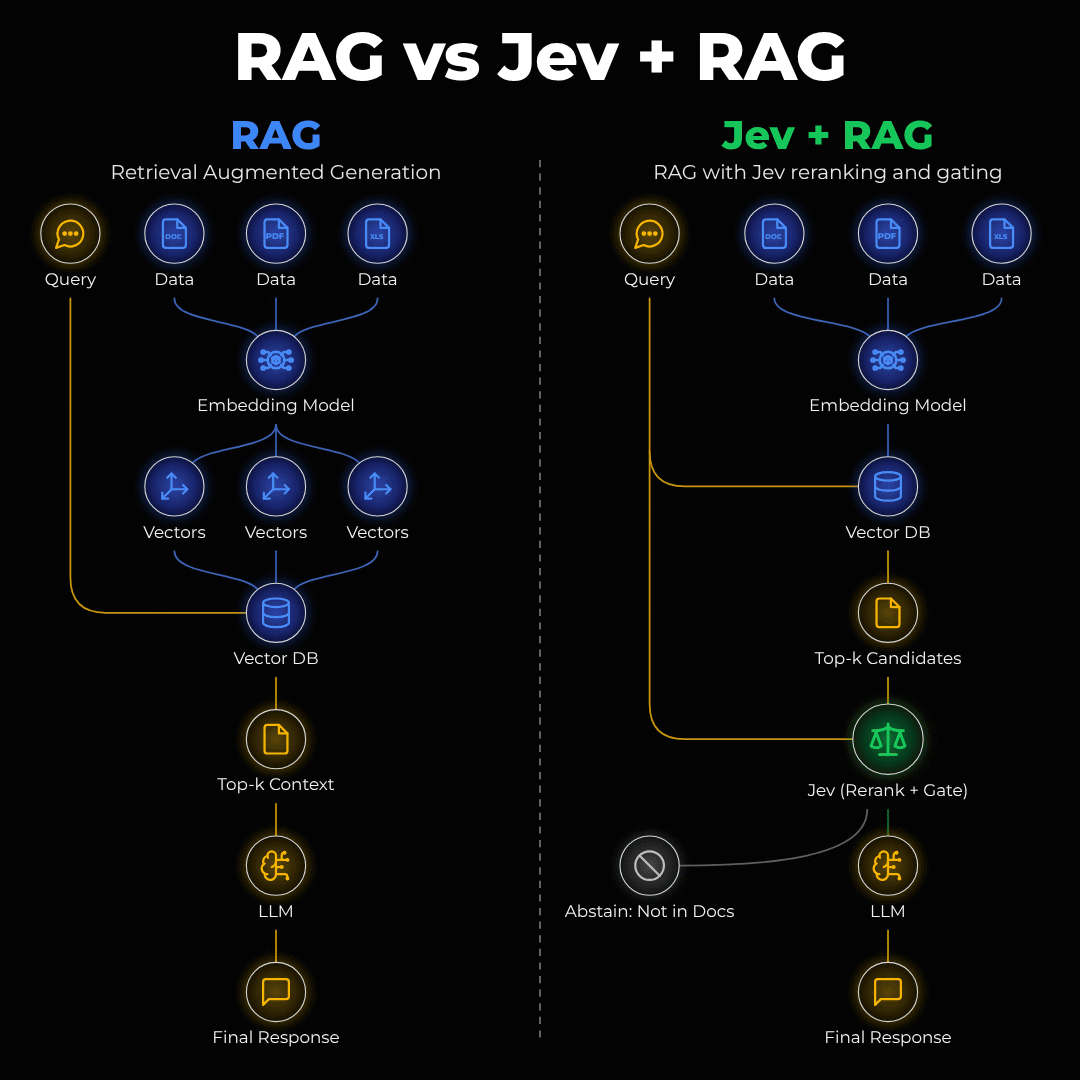
A tutorial builds an agentic RAG support desk using Liquid AI's d1-3B decision model, EmbeddingGemma 2, and In…
Google Flow puts Gemini Omni, Veo and Nano Banana in one web app, letting beginners chat through a storyboard…