What happened
Companies are rationing AI spending as costs exceed budgets—Uber burned through its annual AI budget in four months and capped employee access to agentic coding tools at $1,500 per month. In cybersecurity, the imbalance is acute: attackers need cheap, open-source AI to target one application, while defenders must continuously test thousands of applications across their entire portfolio, mostly on expensive frontier models.
Why it matters
The economics of cyber defense have fundamentally shifted. An attacker runs a capable open-source model continuously until finding one entry point; a defender running frontier models continuously across an enterprise portfolio pays orders of magnitude more for the same method. Most defensive tasks do not require the world's most advanced AI model, yet organizations price them as if they do—making the defender's cost curve unsustainable.
What to watch
The winning approach will combine proprietary specialized models with frontier models, routing each task to the model that performs best for it, rather than relying on frontier models alone. Organizations must own the full offensive AI stack—models, prompts, and routing logic—and continuously benchmark and optimize the system for recall, precision, and cost.
Summaries like this, in your inbox every morning.
The article presents a structural cost crisis in enterprise AI spending, using cybersecurity as the sharpest example of a broader pattern. Uber's budget depletion in four months signals that many organizations underestimated AI operating costs when they built their deployment plans. The real problem, the author argues, is architectural: companies have defaulted to using the same expensive frontier model (a general-purpose AI built for broad reasoning) for every task, including narrow, high-volume work that does not require that capability. This is economically unsustainable at scale.
The cybersecurity domain illustrates the asymmetry starkly. Attackers operate under completely different constraints—they need to find a single vulnerability in a single application and can afford to run cheap, specialized open-source models continuously. Defenders, by contrast, face an inventory problem: they must validate security across their entire application portfolio, every deployment, and every attack vector. Running frontier models for all of that work creates a cost curve that cannot keep pace with an attacker's economics. The author, Ido Geffen (co-founder and CEO of Novee Security), proposes that the only viable solution is to own the full stack—choosing the right model for each task rather than defaulting to the most advanced one, and continuously re-optimizing that choice as new models, costs, and attack techniques emerge. The implication is that companies that treat AI as a single fungible compute resource will lose to those that build adaptive, task-specific architectures.
Pick your industry and the AI tools you use, and get news related to your work every day.
Free · 30 seconds with Google · unsubscribe anytimeWhat is AIToday? →
Ask AI anything about this article. The AI reads this article, earlier AIToday articles, and Wikipedia, and cites its sources. Q&As are published on this page for other readers too.
Wells Fargo hired an AI executive based in San Francisco, a move The Business Journals describes as part of em…
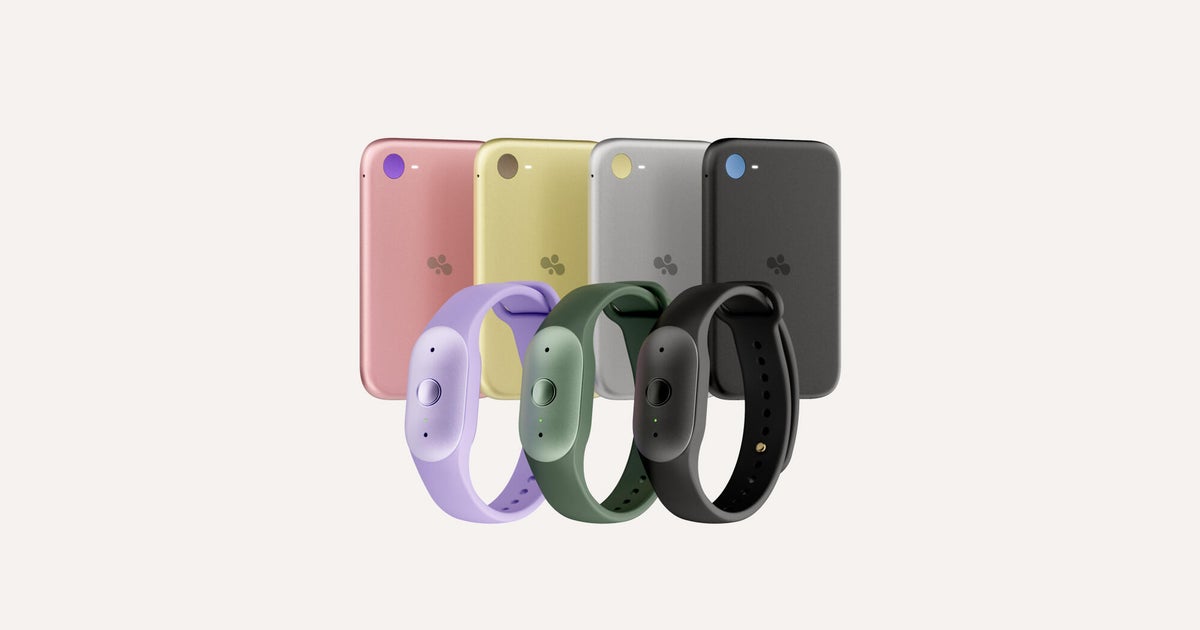
Amazon launched two Bee "personal AI" devices on Thursday: the $74.99 Bee Frontier wristband and the $99.99 Be…
Apple released MLX today, which runs the 816B-parameter Muse Spark Open on four Mac Studios at over 36 tokens…
Bloom Energy stock fell 4% to $229.83, still up 165% year to date, while Caterpillar slipped 3% to $727.55 and…
LogicMonitor announced its 2026 Elevate Award winners at its Elevate Community Conference in Chicago, honoring…
Sandisk, AMD shares fall as Anthropic adds to AI concerns, per Barron's