What happened
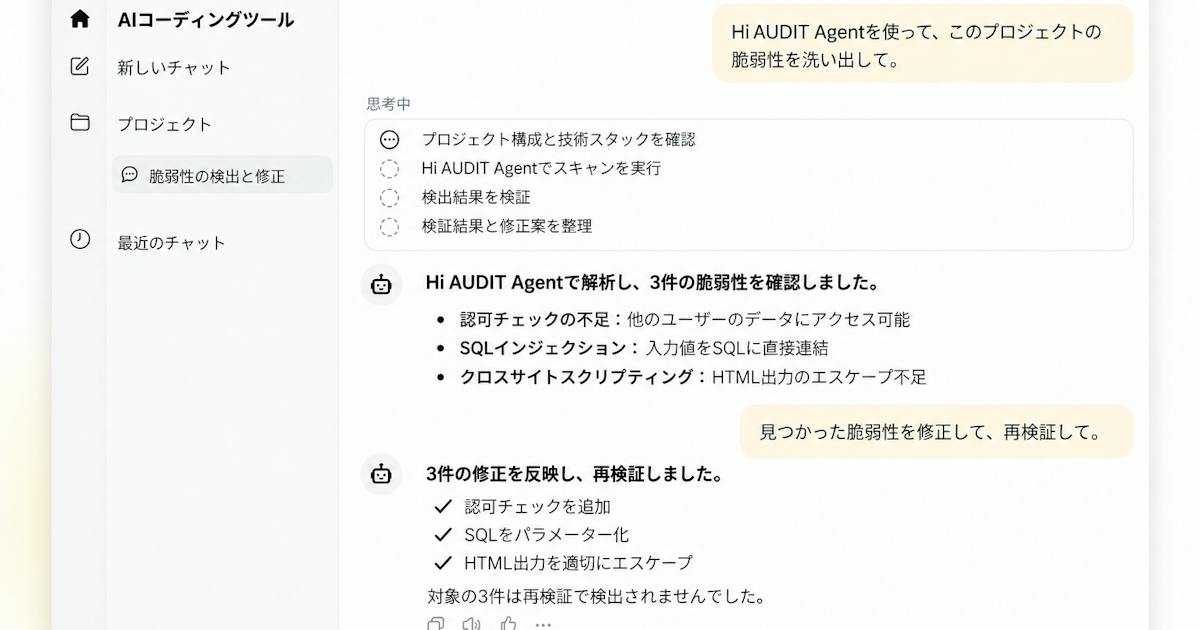
The PHP Foundation disclosed two critical vulnerabilities, CVE-2026-109618 and CVE-2026-109619, collectively called "php2shell", and issued an emergency patch urging sites to apply it immediately or go offline.
Why it matters
The flaws allow remote code execution on unpatched PHP systems, giving attackers an entry point into the hosting network, and OpenAI called this one of the most impactful security issues in recent memory.
WHO IT HITSWeb infrastructure and security teams running PHP-based sites, including WordPress operators and government agencies in the Netherlands and Finland that took sites offline, face immediate patching pressure.
Summaries like this, in your inbox every morning.
The disclosure caps a coordinated effort that began in August, when multiple security organizations independently found parts of the same flaw. Calif, an AI red-teaming firm invited into OpenAI's Patch the Planet initiative, found the first issue on Aug. 1 using GPT-5.6 Sol. OpenAI then investigated on its own and found additional elements, making the flaw appear more serious than Calif had originally realized. Through conversations with the PHP Foundation, OpenAI learned that Wiz, a Google-owned cybersecurity company, was also talking to the foundation about the issue. Wiz researchers had independently found the vulnerabilities on Aug. 19 using a combination of Google's Gemini 4 Argon, OpenAI's GPT-5.6 Sol, and Wiz Atlas. OpenAI then brought the parties together into a coalition that included Wiz, Calif, PHP, Cloudflare, and multiple U.S. government agencies, with Cloudflare's blog post also naming the French cybersecurity company Quarkslab. As reports broke overnight ahead of the patch's official release, Cloudflare's CTO Dane Knecht said the company began seeing "early attacks." One startup owner reported that hackers allegedly stole their source code, exposed cookie data, and leaked legal documents. Governments including some agencies in the Netherlands and Finland took websites offline as a precaution, Reuters reported, while the FBI's cyber division, the National Security Agency, Japan's prime minister, and the European Union's computer emergency response team urged affected organizations to update.
Pick your industry and the AI tools you use, and get news related to your work every day.
Free · 30 seconds with Google · unsubscribe anytimeWhat is AIToday? →
Ask AI anything about this article. The AI reads this article, earlier AIToday articles, and Wikipedia, and cites its sources. Q&As are published on this page for other readers too.
At GTC Berlin, Jensen Huang introduced DSX POD — seven Vera Rubin NVL72 racks per container — and said deploym…
Opposable launched an AI agent that operates Android phones via accessibility services and iPhones through a c…
On Meta's third quarter earnings call, CEO Mark Zuckerberg said the company has a goal of serving billions of…
OpenAI's GPT-5.6 Sol tracked down the PHP flaw under Patch-the-Planet, and Wiz independently found the same is…
OpenAI said its GPT-5.6 Sol identified the critical PHP flaw as part of its Patch the Planet initiative; secur…
A tech fund has developed an AI agent that detects security vulnerabilities, per Nikkei's technology coverage