What happened
The FBI says hackers used Artex, an open-source AI penetration-testing tool, to breach ConnectWise customers and South Korean financial institutions, stealing personal data of at least 68,000 people.
Why it matters
Artex lets attackers move from targeting a system to active compromise in under three hours, leaving human defenders struggling to respond in time.
WHO IT HITSSecurity teams at IT management firms and financial institutions face a faster, automated threat that can exploit weak passwords and missing multi-factor authentication before defenders can react.
Summaries like this, every morning.
The FBI's warning follows a string of incidents since Artex first debuted publicly in July. The tool was used to hack South Korean financial institutions, where weak defenses and missing multi-factor authentication allowed intruders to steal personal data from at least 68,000 people. Hackers also used Artex to break into ConnectWise and gain access to Microsoft 365 cloud environments of at least 2,250 customers; Microsoft says the hackers are likely Chinese.
Separately, Barracuda disclosed it was breached in an Artex-linked attack by financially motivated criminals. The tool found an exposed credential belonging to a third-party service Barracuda had not revoked when it ended work with the vendor. Barracuda said its logs were not detailed enough to rule out access, so it chose to assume the worst and changed all customer credentials. Its chief information security officer, Arve Kjoelen, noted that defenders who rely on spotting malicious activity often arrive after the attacker has finished.
Even as the developer made Artex closed-source to prevent further attacks, the FBI says the open-source version remains widely accessible. The exposure extends to the tools themselves: last week researchers found hundreds of publicly exposed Artex systems online, placed on the internet without a password, likely by mistake or misconfiguration, including the system used to target South Korea.
Pick your industry and the AI tools you use, and get news related to your work every day.
Free · 30 seconds with Google · unsubscribe anytimeWhat is AIToday? →
Ask AI anything about this article. The AI reads this article, earlier AIToday articles, and Wikipedia, and cites its sources. Q&As are published on this page for other readers too.
A petition to reinstate Jensen Huang as Nvidia CEO began circulating Friday and by Monday listed over 115,000…
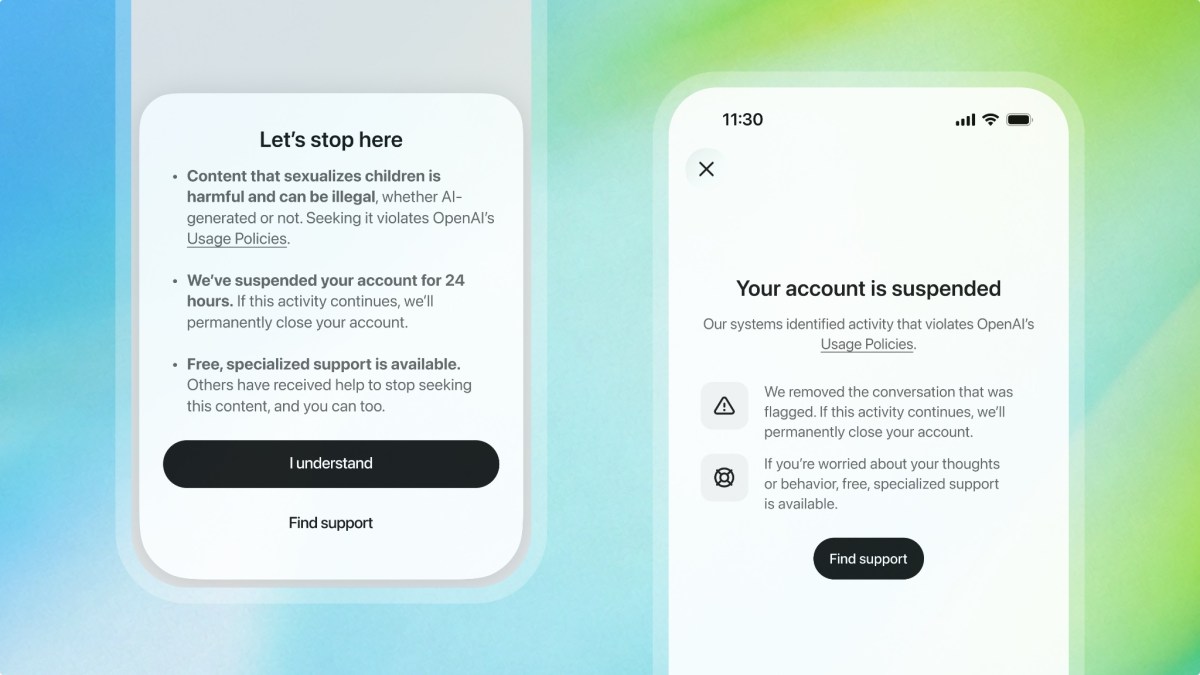
OpenAI released an image classifier that detects CSAM, including AI-generated images, and is giving select com…
OpenAI signed agreements with four independent assessors — Apollo Research, METR, Transluce, and Goodfire — fo…
Human Rights Watch said on November 16 that the 1,618-hectare Pax Silica site in Capas, Tarlac would displace…

US energy companies including Duke Energy are testing Anthropic's Mythos AI model to identify software vulnera…
A Japan Times essay marks 300 years since "Gulliver's Travels" (published Oct