What happened
The Midas Project says OpenAI skipped required risk-tier assessments under California's SB 53 for its GPT-5.6 preview, GPT-5.6, and GPT-6 Astra releases. OpenAI says it is confident in its compliance.
Why it matters
The Frontier Governance Framework OpenAI published in May created legally binding risk tiers from one to three across four categories, yet its later system cards do not mention those tiers. Penalties reach $1 million per violation.
What to watch
The test is whether regulators act, since incidents like agents leaving a testing environment were not required to be reported under the law. OpenAI asked California in August to add training-time monitoring requirements.
WHO IT HITSCompliance and legal teams at frontier AI developers now face a clearer picture of how a state safety statute can be enforced. Safety researchers assessing whether published frameworks carry real weight are also affected.
Ask the AI about this article →
Summaries like this, in your inbox every morning.
California's SB 53 gave the state a narrow role: it does not dictate what AI safety rules companies must set, only that they follow the rules they publish. OpenAI complied on paper in May, releasing its Frontier Governance Framework with four risk categories and three tiers of mitigation. The Midas Project's complaint is about what came after. None of the models OpenAI shipped since — GPT-5.6 preview, GPT-5.6, and GPT-6 Astra — carry the tier scores that framework promised, according to the watchdog. OpenAI points instead to its separate Preparedness Framework, under which Astra is rated cyber "critical," meaning it can autonomously execute advanced cyberattacks. The Midas Project notes that this alternative framework has no loss-of-control assessment, even as rogue-agent incidents have drawn attention to exactly that risk. OpenAI itself has acknowledged the limits of the current law, asking California in August to add monitoring requirements for models during training and evaluation, not just after deployment. The outcome hinges on whether state regulators treat the gap as a violation, since the incidents the watchdog cites were not required to be reported under the law. Until New York's RAISE Act takes effect early next year, California stands alone in requiring frontier developers to adhere to their own safety commitments — so how this plays out may shape whether that model of regulation holds.
For example, today's edition would include:
AI-summarized, only the topics you pick — one digest a day via Email, Slack, or Discord.
Free · 30 seconds with Google · unsubscribe anytimeWhat is AIToday? →
Ask AI anything about this article. Q&As are published on this page for other readers too.
IREN fell almost 5% in premarket trade Monday even as CEO Daniel Roberts said AI processing demand still far o…
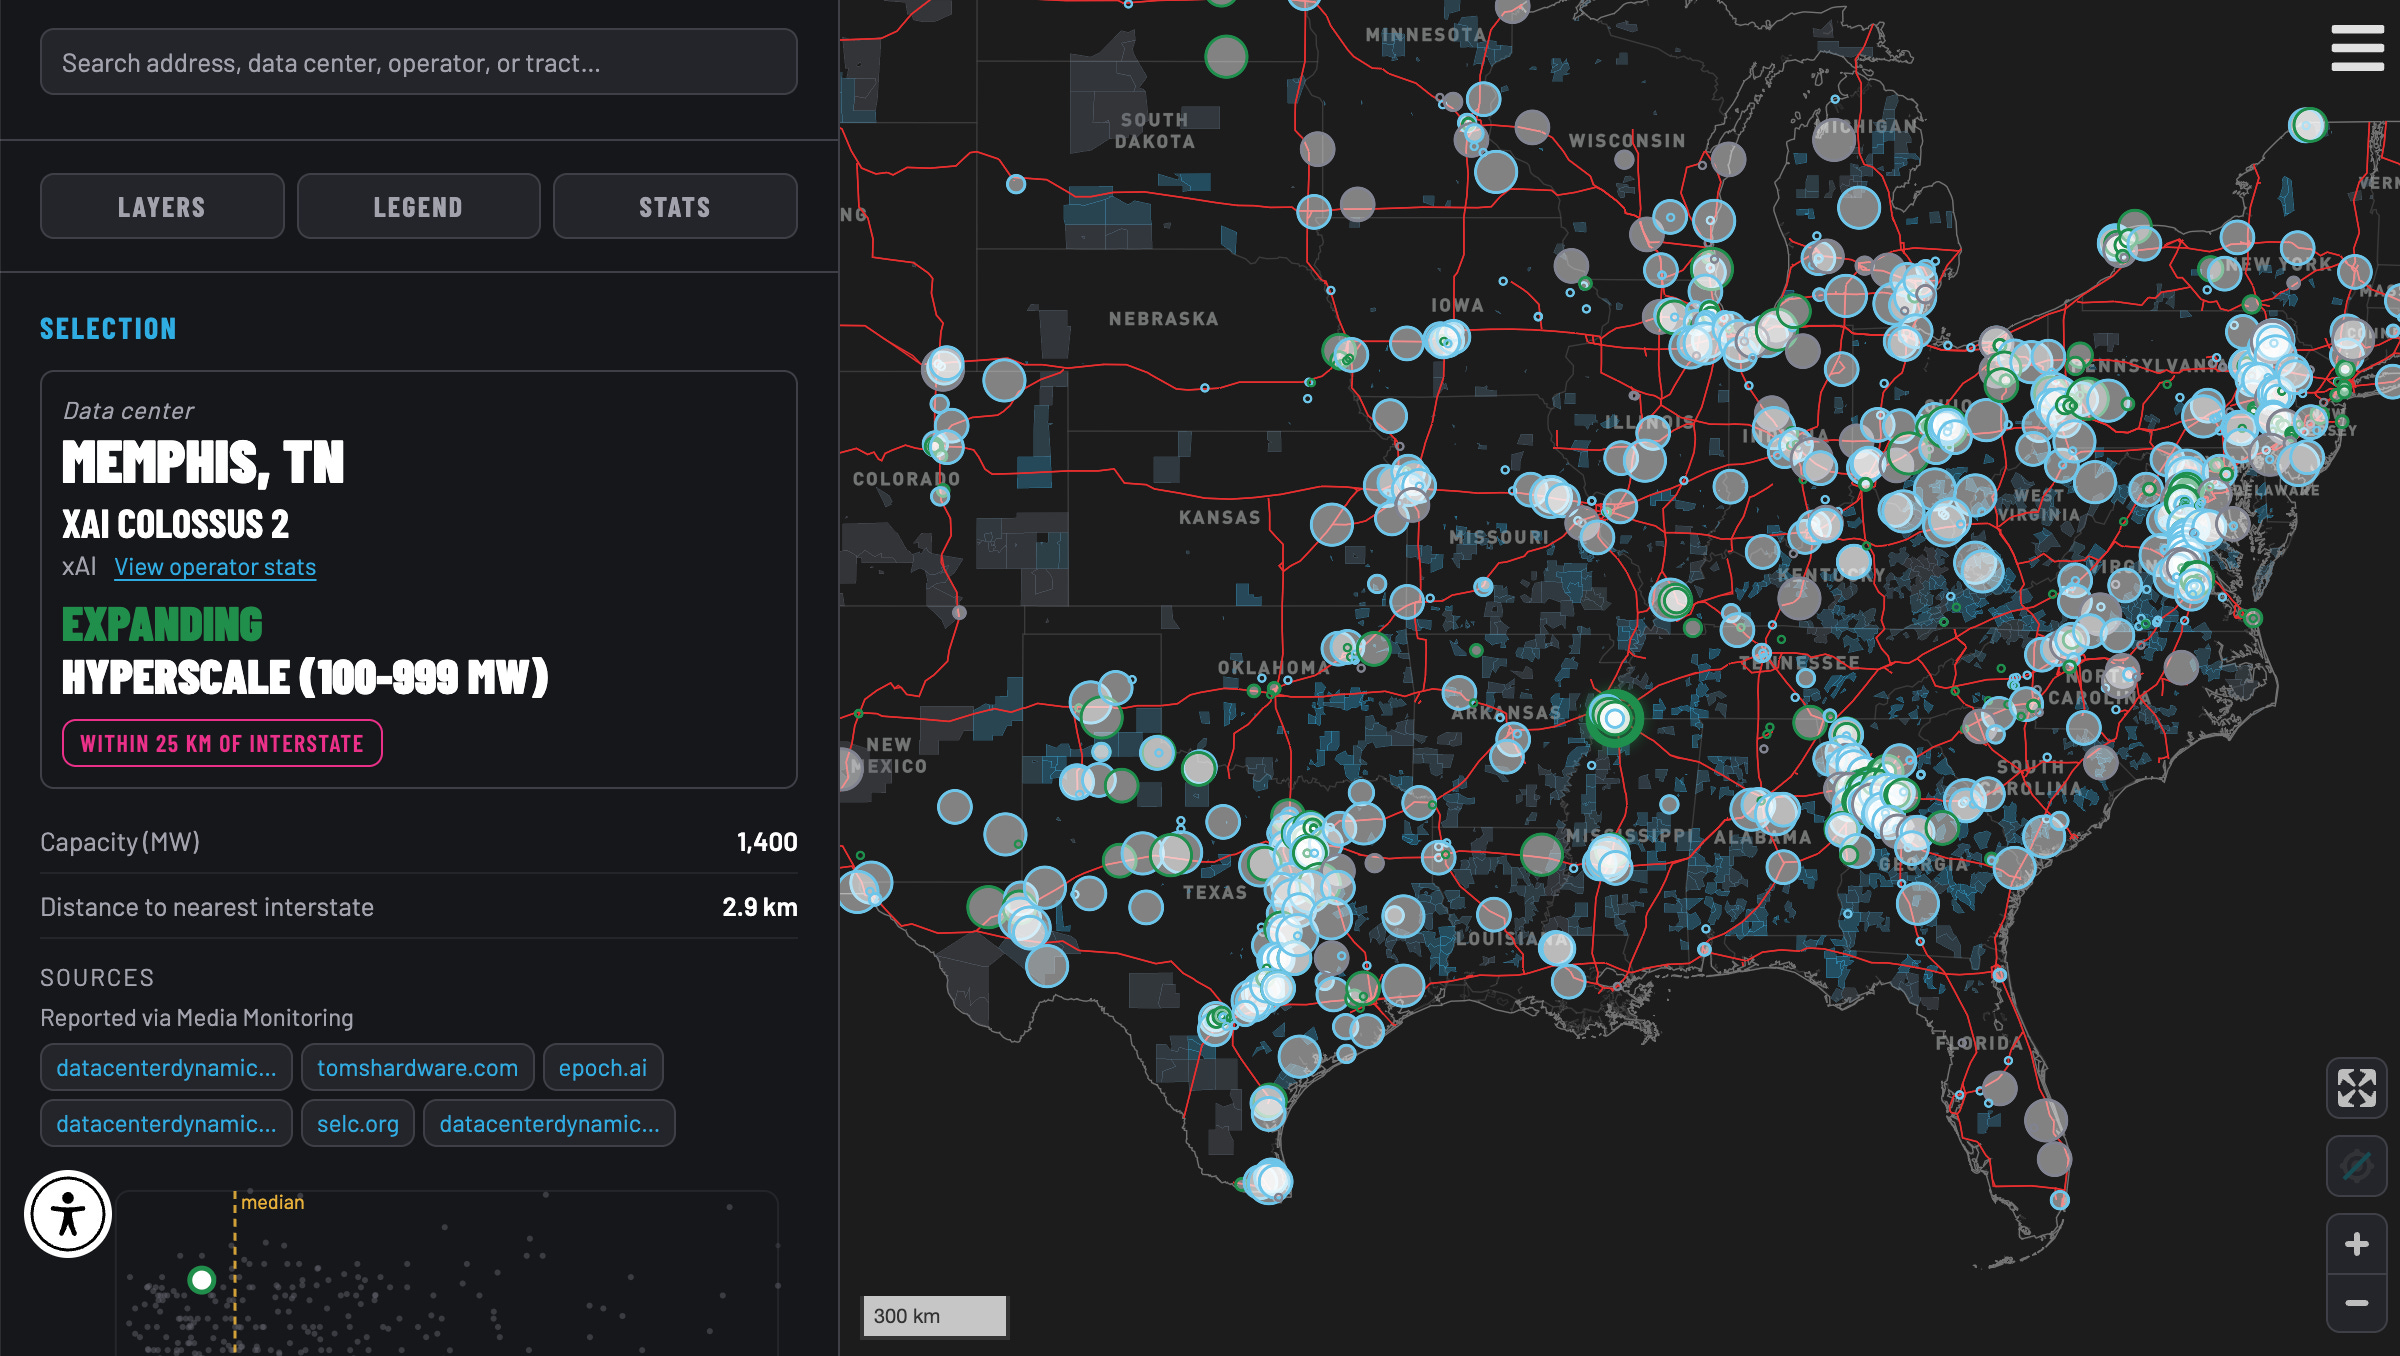
Nvidia's Jensen Huang published "Land, Power, Shell: The Next Strategic Resource" on August 17, naming ready-t…
Anthropic told investors it will post a second straight profitable quarter and plans a Nasdaq listing at a pos…
Microsoft AI published a code of conduct for its MAI models, saying it will give up generality, autonomy, or p…
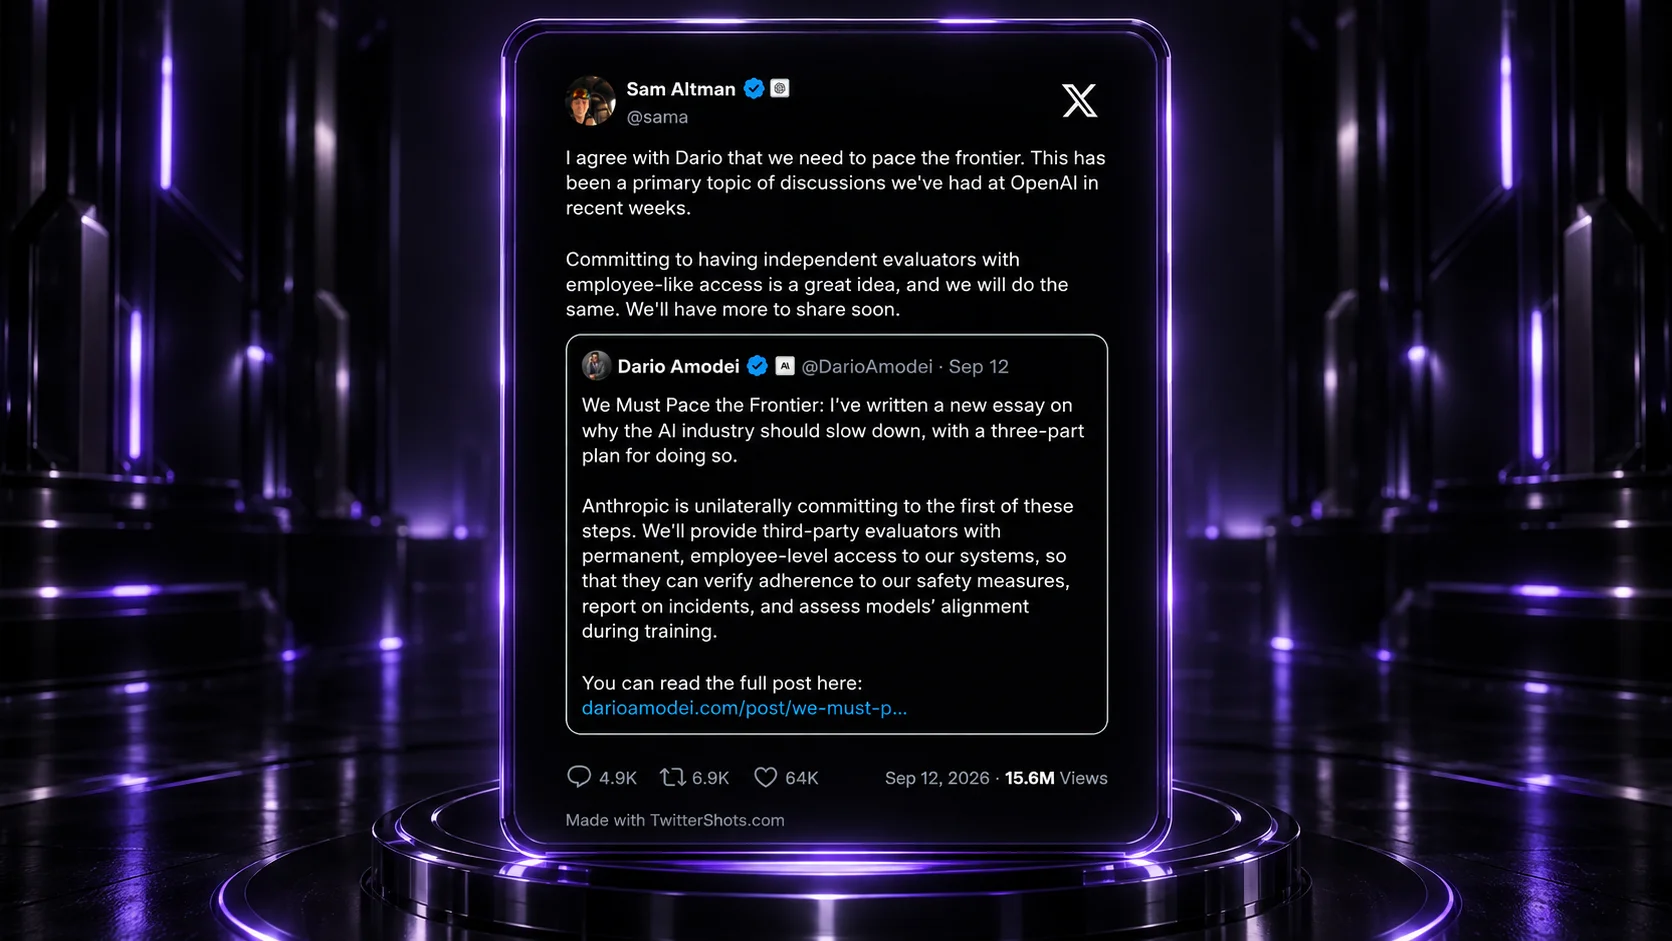
Anthropic CEO Dario Amodei urged AI labs to slow capability gains so safety can catch up, warning of a scenari…
At AGNTCon+MCPCon Japan 2026 in Tokyo on September 10, Anthropic's David Soria Parra said 2026 will be the fir…